Attacking DevOps Systems and What it Costs You
Explore real-world DevOps security vulnerabilities through bug bounty examples, including Facebook Github runners and organization compromises, while learning practical defense strategies and attack mitigation techniques.
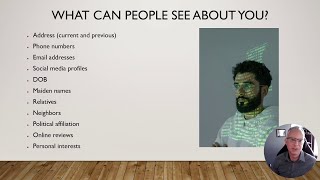
Protecting Yourself Online: Social Engineering Defense and Privacy Strategies
Discover essential strategies for protecting your digital footprint from social engineering attacks, learning how pentesters gather public information and implementing effective countermeasures.
Creating Personal Disinformation Campaigns for Digital Safety and Privacy
Discover innovative strategies for personal security by creating deliberate digital noise and misinformation to protect yourself from stalkers while maintaining an active online presence.
Inside Dash Cam Custom Protocols and Security Vulnerabilities
Delve into comprehensive security analysis of network-connected dash cams, exploring vulnerabilities in boot processes, custom protocols, and configuration systems across multiple international manufacturers.
Unlocking the Gates: Hacking Industrial Remote Access Solutions
Dive into the vulnerabilities of industrial VPN gateways, exploring security flaws in remote access solutions and learning techniques to identify and understand potential system compromises.
Exploiting Security Vulnerabilities in Microhard Radio Equipment
Uncover critical security vulnerabilities in Microhard's radio equipment, including command injections and buffer overflows, while exploring implications for SCADA and utility systems.
Prototype Pollution Leading to Remote Code Execution in NodeJS
Delve into prototype pollution vulnerabilities in Node.js, exploring how they enable remote code execution, analyzing real-world exploits, and understanding recent security mitigations.
Real-Time Video and Audio Deep Fake Impersonation - A Security Demonstration
Explore real-time deepfake technology and its potential security risks through practical demonstrations of CEO impersonation using open-source tools and accessible hardware.
HL7Magic: Medical Data Hacking and Security Testing Tool
Discover how to intercept and analyze HL7 medical device communications using HL7Magic, a new security testing tool designed to identify vulnerabilities in healthcare data transmission systems.
Finding Zero-Day Vulnerabilities in Vilo Home Routers - Security Research Process and Discoveries
Discover how student researchers uncovered 9 zero-day vulnerabilities in Vilo routers through hardware hacking, firmware analysis, and cloud infrastructure investigation, highlighting IoT security challenges.
Hacking Norwegian Banks Through Paper-Based Identity Theft
Uncover shocking vulnerabilities in Norwegian banking systems through real-world examples of identity theft and unauthorized access, revealing critical lessons about paper-based security flaws.
Time-Based SQL Injection Techniques and Defense Strategies
Dive into time-based SQL injection techniques through Operation GhostShell, featuring live demos and defense strategies for protecting against sophisticated database vulnerabilities.
Social Engineering Techniques for Physical Access Red Team Operations
Dive into real-world social engineering tactics through a first-person narrative of complex red team operations, exploring methodologies for physical access and critical infrastructure penetration testing.
Exploiting Voice Cloning in Adversarial Simulation - Security Testing and Defense Strategies
Explore the security vulnerabilities of voice verification systems through deep learning voice cloning techniques, including practical demonstrations, risk assessment, and defensive countermeasures.
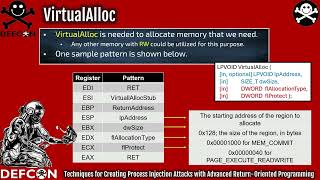
Process Injection Attacks with Return-Oriented Programming - Advanced Techniques and Methodologies
Discover advanced process injection techniques using return-oriented programming (ROP), including unique string comparison solutions, multiple WinAPI patterns, and practical methodologies for reliable implementation.
Scam as a Service Powered by Telegram
Uncover how cybercriminals leverage Telegram for scam operations, exploring tactics, infrastructure, and prevention methods in modern digital fraud schemes.
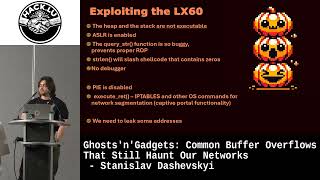
Ghosts and Gadgets - Common Buffer Overflows That Still Haunt Our Networks
Explore common buffer overflow vulnerabilities in network systems, their detection methods, and practical mitigation strategies for securing modern networks.
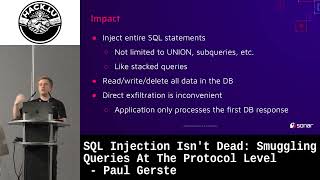
SQL Injection Isn't Dead - Smuggling Queries at the Protocol Level
Dive into advanced SQL injection techniques and protocol-level query smuggling, exploring sophisticated database security vulnerabilities and modern attack vectors.
Free Web App Pentesting Tools and Resources
Discover essential free tools and resources to enhance your web app pentesting and bug bounty skills. Learn about Caido, Burp Suite, browser plugins, and hands-on learning platforms.
Cloud Kleptos: Lessons Learned Responding to Scattered Spider - SANS DFIR Summit 2024
Explore advanced cloud-focused attack techniques and defense strategies against persistent threat actors like Scattered Spider. Learn about their methodical approach, TTPs, and how to protect your organization's assets.
Debugging Memory Issues with Valgrind and GDB
Discover techniques for debugging memory issues using Valgrind and GDB in C/C++ programs. Learn to identify and resolve buffer overflows, memory leaks, and other low-level errors efficiently.