Hacking a Cat - Going Beyond Traditional Attack Vectors
Explore the future of cybersecurity as implants and medical tech advance, examining potential threats to connected humans and the evolving digital landscape.
Hacking Humans - Social Engineering Techniques and How to Protect Against Them
Explore social engineering tactics, their impact on organizations, and learn effective strategies to protect yourself and your company from manipulation and security breaches.
Making the Most of Security Tests
Explore real-world security testing through a multi-layer product attack, covering various test types, their impacts, and strategies for improving overall product and environment security.
Hacking with Go
Hands-on exploration of Go for security tools: network enumeration, information extraction, packet sniffing, port scanning, and brute force techniques. Gain practical insights for developing security applications in Go.
Can AI Fix Vulnerable Code? - Exploring AI's Potential in Cybersecurity
Explore AI's ability to fix vulnerable code through XSS, injection attacks, and LFI examples. Assess ChatGPT's effectiveness in addressing these security issues in web applications.
Combining the Power of Builders and Breakers in Cybersecurity - USENIX Enigma 2018
Exploring the evolving relationship between companies and security researchers in bug bounty programs, examining challenges, benefits, and future implications for cybersecurity.
Exploiting Windows COM - WinRT Services
Discover techniques for exploiting Windows COM/WinRT services, uncovering vulnerabilities in cross-process communication and UWP applications for potential LPE, RCE, and sandbox escape attacks.
Diving Into Spooler - Discovering LPE and RCE Vulnerabilities in Windows Printer
Uncover critical vulnerabilities in Windows Printer Spooler, exploring potential LPE and RCE exploits. Learn from past attacks and discover hidden security risks in this essential system component.
Is WebAssembly Really Safe? - Wasm VM Escape and RCE Vulnerabilities Have Been Found in New Way
Explore WebAssembly security vulnerabilities through a new fuzzing framework, focusing on VM escape and RCE risks in Wasm runtimes for edge computing and web applications.
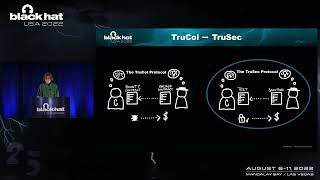
Eliminating Triage Intermediaries for Zero-day Exploits Using a Decentralised Payout Protocol
Explore a protocol for collectivizing security bounties, enabling companies to showcase software security and ethical hackers to retrieve bounties without ambiguity, eliminating subjectivity in triage processes.

Hackers - The Internet's Immune System
Cybersecurity expert Keren Elazari explores how hackers can positively impact society by exposing vulnerabilities, fighting corruption, and advocating for rights, ultimately strengthening the internet.
HackTheBox Blue Walkthrough - Learn Windows Enumeration
Comprehensive guide to exploiting the Blue machine on HackTheBox, covering Windows enumeration techniques and post-exploitation using Metasploit modules.
HackTheBox Walkthrough - Optimum
Step-by-step guide to exploiting vulnerabilities in the Optimum machine on HackTheBox, demonstrating penetration testing techniques and system compromise methods.
Physical OSINT: Finding and Investigating Facilities Using Open Source Intelligence
Discover essential physical OSINT techniques and tools for gathering intelligence, from basic social media searches to advanced facility reconnaissance and data collection methods.
Evading Modern Defenses When Phishing with Pixels - QR Code Exploitation Techniques
Explore advanced QR code phishing techniques, from fundamental concepts to creative obfuscation methods, focusing on exploiting Outlook Mail rendering vulnerabilities for enhanced penetration testing.
Empathy as a Skill
Explore the evolution of empathy from primal connections to AI-driven interactions, and discover how understanding others can create a happier world in this thought-provoking talk.
Curiosity Killed the Hack
Explore ethical hacking tools and techniques, including insights on vehicle hacking, security issue detection, and corporate protection strategies from an experienced security analyst.
Let Me Show You How React Applications Get Hacked in the Real-World
Explore real-world React application vulnerabilities and learn how to prevent cross-site scripting attacks through secure coding practices and proper API usage.
Secure Code, Safe Future: Mastering Security in Critical Software Development
Discover practical secure coding techniques and strategies for developing robust software, including vulnerability management, SBOM implementation, and hands-on security practices for critical infrastructure projects.
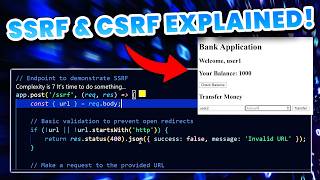
Understanding CSRF and SSRF Web Security Vulnerabilities - Demo and Examples
Explore CSRF and SSRF web security vulnerabilities through practical demonstrations, understanding attack mechanisms, key differences, and essential prevention strategies for robust application security.
Discord as Malware Infrastructure - Emerging Threats and Attack Trends
Explore how cybercriminals leverage Discord as malware infrastructure and discover emerging threats targeting hackers, with insights into Turkish threat actors' tactics.