Constructing a Dynamic CFG for EVM-Based Smart Contracts
Explore dynamic control flow graph construction for Ethereum smart contracts, enhancing security analysis and vulnerability detection in blockchain applications.
Sound Dynamic Deadlock Prediction in Linear Time
Explore a novel approach to dynamic deadlock prediction in concurrent systems, introducing sync-preserving deadlocks and efficient algorithms for sound, linear-time detection.
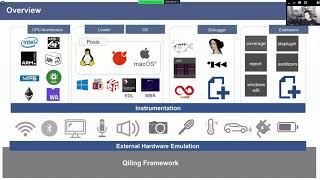
When Qiling Framework Meets Symbolic Execution
Exploring Qiling Framework's new symbolic execution capabilities for advanced binary analysis across architectures, with demonstrations and insights into its development and applications.
Instrumenting System Applications on Android Images
Instrumenting Android system apps on stock images using Frida for dynamic analysis. Explores various approaches, their limitations, and a successful method for analyzing Google Play Protect Services.
Sum Total of ISA Knowledge - Analyzing Your Binary Analysis Tools
Explore techniques to measure and verify architecture support in binary analysis tools, enhancing firmware reverse engineering through selective application of dynamic analysis methods.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
Using WPP and TraceLogging Tracing to Facilitate Dynamic and Static Windows
Explore advanced Windows tracing techniques using WPP and TraceLogging for enhanced dynamic and static analysis in cybersecurity investigations.
Unveiling the Underground World of Anti-Cheats
Explore the ongoing battle between cheat developers and anti-cheat technologies in gaming. Learn about bypassing techniques and tools for testing anti-cheat software effectiveness.
A New Trend for the Blue Team - Using a Symbolic Engine to Detect Evasive Forms of Malware - Ransomware
Explore symbolic engines for detecting evasive malware and ransomware, enhancing blue team capabilities in reverse engineering and threat analysis.
Invoke-DOSfuscation - Techniques for S-level CMD Obfuscation
Explore advanced CMD obfuscation techniques used by threat actors, including string manipulation and encoding methods. Learn about new obfuscation approaches and their detection implications for cybersecurity professionals.
The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
Trick or Treat - Unveil the "Stratum" of the Mining Pools
Unveil mining pool strategies, identify Stratum servers, and explore cryptomining malware detection techniques through static and dynamic analysis, web scraping, and network scanning.
The Ways Hackers Are Taking To Win The Mobile Malware Battle
Explore cutting-edge mobile malware techniques, security paradigms, and detection methods. Live demo showcases creation of undetectable malware, highlighting challenges in mobile security.
Why Hackers Are Winning The Mobile Malware Battle - Bypassing
Explore mobile malware challenges, hacker tactics, and bypassing techniques in this insightful talk on the evolving landscape of mobile security threats and defenses.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
SecDevOps - Current Research and Best Practices
Explore current research and best practices in SecDevOps, covering static and dynamic analysis, security scaling, and infrastructure best practices for improved application security.
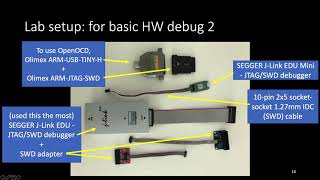
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.
Mac-A-Mal - An Automated Platform for Mac Malware Hunting
Automated platform for macOS malware analysis, featuring kernel-level behavioral monitoring and extending Cuckoo sandbox capabilities. Supports various sample types and detects evasion techniques.

IoT Malware - Comprehensive Survey, Analysis Framework and Case Studies
Comprehensive exploration of IoT malware, covering its evolution, analysis frameworks, and real-world case studies. Insights into vulnerabilities, detection methods, and future challenges in securing connected devices.
Code Deobfuscation - Intertwining Dynamic, Static and Symbolic Approaches
Explore advanced code deobfuscation techniques combining dynamic, static, and symbolic approaches to enhance software analysis and reverse engineering capabilities.