New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Bugs Ruin Everything - Keynote on Vulnerability Analysis and Exploitation
Explore vulnerability analysis techniques, their strengths and weaknesses, and real-world case studies with security expert Charlie Miller in this engaging keynote from AppSecEU 2016.
Verifying Software for Security Bugs - Dynamic Analysis and Fuzzing Testing
Learn dynamic analysis and fuzzing techniques to verify software security, including mitigations and vulnerability checks. Explore BinSecSweeper, an open-source tool for binary analysis on Windows and Linux.
Static Analysis for Dynamic Assessments - OWASP AppSecUSA 2014
Explore techniques for using static analysis tools in dynamic web vulnerability assessments without source code, enhancing detection of security weaknesses in complex applications.
Hunting Fileless Malware with Treesitter
Explore advanced techniques for detecting obfuscated, fileless malware using Treesitter parser generator library. Learn to create scalable and accurate detections for malicious PowerShell and Bash payloads.
Finding Vulnerabilities in Your Codebase Using Open Source Tools
Explore open-source tools for identifying vulnerabilities in your codebase. Learn effective techniques to enhance software security and protect against potential threats.
Ransomware in Action - MedusaLocker ReadText34
Explore MedusaLocker ransomware's behavior and tactics through dynamic analysis, gaining insights into its encryption process and file manipulation techniques.
101 Things Your Application is Doing Without Your Knowledge
Uncover hidden behaviors in your applications, including unexpected file operations and network connections, even when using trusted dependencies. Learn to identify and manage these covert activities.
Practical Steps to False Positive Reduction and Benign File Analysis
Learn efficient techniques for identifying false positives and analyzing clean files in malware analysis. Gain actionable tips from real-world examples to enhance your workflow and save time and resources.
A Posteriori Taint-Tracking for Demonstrating Non-Interference in Expressive Low-Level Languages
Explore a novel approach to information-flow analysis in low-level languages, focusing on non-interference proofs, taint-tracking optimization, and performance improvements in security applications.
ConDySTA - Context-Aware Dynamic Supplement to Static Taint Analysis
Explore innovative techniques for enhancing static taint analysis with context-aware dynamic analysis, improving detection of security vulnerabilities in software systems.
Uncovering OWASP's Mobile Risks in iOS Apps - AppSec California 2015
Explore iOS app vulnerabilities through reverse engineering techniques. Learn to extract, analyze, and identify common security risks in mobile applications using real-world examples.
CopperDroid: Reconstructing Android Malware Behaviors
Explore CopperDroid, an innovative system for analyzing Android malware behaviors through VMI-based dynamic analysis, capturing both OS-specific and Android-specific actions to enhance mobile security.
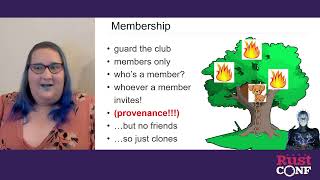
What If We Pretended Unsafe Code Was Nice, and Then It Was? - RustConf 2022
Explore Rust's Strict Provenance APIs for safer and more efficient unsafe code. Learn how pretending unsafe code is nice can lead to better documentation, libraries, and tools.
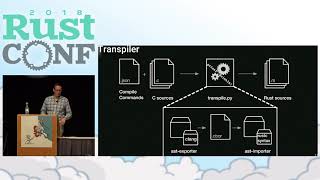
C2Rust: Migrating Legacy Code to Rust - RustConf 2018
Explore tools for migrating C/C++ to Rust: transpiler for equivalent code, dynamic analysis for computation checks, and refactoring tool for idiomatic Rust. Automate steps and detect discrepancies during migration.
Inside the Wizard Research Engine - WebAssembly Innovations and Challenges
Explore WebAssembly's potential with Wizard, a new engine designed for instrumentation and VM experimentation. Learn about its innovative in-place interpreter and advanced capabilities.
OpenJDK Development and Optimization at Google
Explore Google's OpenJDK development, static and dynamic analysis, profiling challenges, and GC optimization with Jeremy Manson in this insightful talk on Java engineering practices.
Testing GUI Apps - What to Test and How to Test It - Mini Coding Course for Beginners
Learn automated software testing with a hands-on Kivy GUI project. Covers static and dynamic analysis, unit testing, and various test scenarios to improve code quality and reliability.
Inside the Wizard Research Engine
Explore WebAssembly's potential, challenges, and innovations through the Wizard engine, designed for instrumentation and VM experimentation in various deployment contexts.
Sanitizing the Linux Kernel - KASAN and Other Dynamic Bug-finding Tools
Explore KASAN and other Sanitizers for detecting memory safety issues in the Linux kernel, including implementation details and practical usage techniques.
Syzbot and the Tale of Thousand Kernel Bugs
Explore Linux kernel bug detection tools and their impact on system security. Learn about syzbot, syzkaller, and sanitizers for improving kernel stability and reliability.