Messing with Forensic Analysts - Modifying VSS Snapshots
Learn techniques to modify Volume Shadow Copy snapshots, understand VSS basics, and explore methods to detect tampering in forensic analysis.
The Ouroboros of Cybercrime - From Pwn to Pwned
Explore the cyclical nature of cybercrime as threat actors transition from attackers to victims, examining real-world cases and evolving cybersecurity dynamics.
Breaking the Ransomware Tool Set - When an OPSEC Failure Became an Intel Goldmine
Dive into a revealing analysis of ransomware operations through a critical OPSEC failure, uncovering valuable intelligence insights and defensive strategies against cybercrime toolsets.
SIERRA - Automating and Scaling Forensic Investigations at Siemens CERT
Discover how Siemens CERT automates and scales digital forensic investigations through SiERRA, exploring practical approaches to handling large-scale security incidents efficiently.
SOC Analyst's Arsenal - Essential Tools, Tips and Tricks for Effective Investigations
Master essential tools and investigative techniques for SOC analysis, featuring proven tips and tricks to enhance security incident response and threat detection capabilities.
Cracking The Chaos Ransomware Family
Dive into the technical analysis and decryption methods of the Chaos ransomware family, exploring its characteristics, vulnerabilities, and countermeasures.
Using Media Variants to Uncover Coordinated Influence Operations
Discover innovative techniques for uncovering coordinated influence operations through media metadata analysis, illustrated with a real-world case study of pro-PRC operator Dragonbridge.
OSINT Fundamentals - A Guide to Open Source Intelligence Gathering
Discover the art of Open Source Intelligence through a Dr. Seuss-inspired exploration of OSINT tools, techniques, and ethical considerations for gathering and analyzing publicly available information.
Simulating Attacks Against Hydroelectric Power Plants Using ICS Firing Range
Dive into a comprehensive simulation of cyberattacks on hydroelectric facilities, exploring both offensive tactics and defensive strategies through a custom-built ICS firing range environment.
Solving the Lover Stalker Killer Murder Case Using Digital Forensics Tools
Delve into forensic digital investigation techniques used to solve a real murder case, exploring how basic Unix tools and Perl programming helped crack a complex cyberstalking homicide investigation.
Exploit Password Management Software to Obtain Credentials from Memory
Discover techniques for exploiting password management software vulnerabilities to extract credentials from system memory, focusing on security assessment and penetration testing methodologies.
Codifying Digital Forensic Intelligence
Explore digital forensic intelligence codification methods and frameworks with expert Thomas Chopitea, enhancing your investigative capabilities and analytical approach to cybersecurity.
Elevating Cloud Forensics - Hypervisor-Level Methods for Evidence Unveiling
Explore innovative hypervisor-level methods for cloud forensics using AI and machine learning to detect and preserve potential evidence in cloud platforms.
Security Incidents for DevOps Teams
Learn essential security incident knowledge for DevOps teams. Discover what to do during incidents, when to seek help, how to preserve evidence, and why security teams need your support. Gain insights through real-world stories.

Unmask The DeepFake - Defending Against Generative AI Deception
Explore deepfake technology, its risks, and mitigation strategies in this insightful talk. Learn to stay ahead of evolving AI-driven deception threats in the digital landscape.
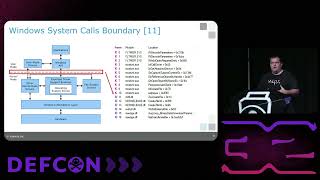
Defeating EDR Evading Malware with Memory Forensics
Discover advanced memory forensics techniques to detect and analyze EDR-evading malware, including system call manipulation, module overwriting, and debug register abuse.

The Little Dutch Boy - Don Quixote
Explore cybersecurity challenges and solutions in this engaging talk, drawing parallels to the classic tale of the Little Dutch Boy and modern digital threats.
Hivemind - Distributed File Storage Using Javascript Botnets
Explore distributed file storage using JavaScript botnets, covering WebSockets, Redis, and web workers. Learn about data prioritization, network traffic optimization, and potential security implications.
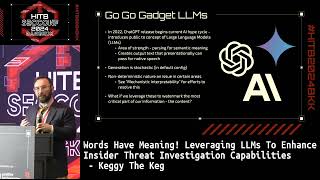
Leveraging Large Language Models to Enhance Insider Threat Investigation Capabilities
Discover innovative methods using LLMs for cybersecurity investigations, focusing on semantic watermarking techniques to detect and trace unauthorized data exfiltration across air-gapped systems.
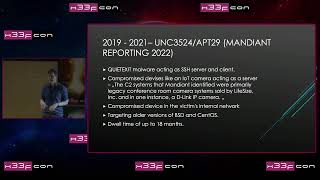
Addressing Tactics Related to Edge Device Compromise - Security Detection and Defense
Explore advanced threat hunting techniques and defense strategies against edge device compromises, focusing on detection methods, forensic analysis, and proactive security measures for network infrastructure.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.