The Action Group Model for Incident Response
Discover a flexible framework for coordinating incident response teams, improving support structures, and developing staff capabilities during security incidents.
The Action Group Model for Incident Response
Discover a flexible framework for coordinating incident response teams, improving support structures, and developing staff capabilities during security incidents.
Windows System Monitor (Sysmon) for Incident Investigation and Threat Response
Master Windows System Monitor (Sysmon) for incident investigation, learning to track program execution, registry writes, and DNS queries to effectively trace threat actor activities and enhance system security.
Hackers in Jurassic Park: When Attackers Find a Way
Explore real-world cybersecurity breaches through engaging hacking stories, drawing parallels with Jurassic Park to understand how attackers penetrate seemingly secure digital systems.
Leakonomics 101: The Last Year in Data Leaks - Analysis and Trends
Explore the anatomy of data leaks through real-world cases from the past year, examining breach patterns, criminal marketplace dynamics, and emerging trends in cybersecurity threats and vulnerabilities.
Social Engineering and Real-Time Malware Attack Strategies - War Stories
Explore real-world social engineering tactics in targeted malware attacks, where attackers use direct communication and psychological manipulation to achieve successful system compromises.
Private Until Presumed Guilty - Digital Privacy and Law Enforcement Surveillance
Explore how law enforcement leverages personal data from phones and apps for investigations, focusing on privacy implications, forensic tools, and legal protections in the digital age.
StackMoonwalk: Advanced Memory Evasion Techniques Through Call Stack Tampering
Delve into advanced memory evasion techniques for cybersecurity, exploring novel "Full Moon" and "Half Moon" approaches to call stack tampering, plus learn detection methods using the Eclipse algorithm.
Secret Life of Rogue Devices: Lost IT Assets on the Public Marketplace
Uncover the alarming journey of lost corporate devices in public markets through data scraping, OCR clusters, reverse engineering, and conversations with underground collectors.
Signature-Based Detection Using Network Timing - Malware Traffic Analysis
Explore advanced malware detection techniques using network timing patterns and Python, learning to identify malicious behavior through transaction intervals rather than traditional code signatures.
Digital Forensics and Technical Analysis of Phishing Email Campaigns
Dive into comprehensive digital forensics techniques for analyzing phishing emails, from examining suspicious attachments to investigating malicious websites and understanding SOC response protocols.
The Gist of Hundreds of Incident Response Cases
Gain insights into incident response patterns and best practices drawn from analyzing hundreds of real-world cybersecurity cases, delivered by expert Stephan Berger.
Understanding File Type Identifiers and Scanners
Dive into file type identification techniques and scanning mechanisms, exploring how different systems detect and process various file formats for enhanced digital forensics and security.
Dredge - An Open Source Framework for Cloud Incident Response
Discover how to effectively respond to cloud security incidents using Dredge, an open-source framework that streamlines investigation and remediation processes in cloud environments.
CyberMirage: AI DeepFake LIVE Demo
Witness a groundbreaking AI DeepFake LIVE demo showcasing the viral CyberMirage technology. Explore cutting-edge cybersecurity implications with seasoned expert Brandon Kovacs at HackMiami XI.
CompTIA Security+ Exam Practice Questions - Part 1
Comprehensive practice session for CompTIA Security+ exam, covering incident response, digital forensics, physical security, network security, and application security with detailed explanations and strategies.
Leveraging Global Partnerships Against Cyber Adversaries
Explore strategies used by international agencies to combat global cyber threats through collaboration, unique authorities, and advanced capabilities.
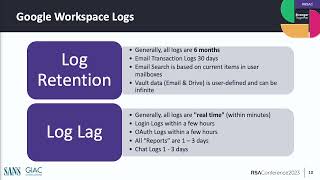
DFIR Evidence Collection and Preservation for the Cloud
Learn essential techniques for collecting and preserving digital forensics evidence in cloud environments, focusing on major platforms like Azure, AWS, Google Cloud, Microsoft 365, and Google Workspace.
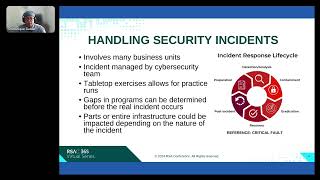
Infrastructure Security: Digital Forensics, Vendor Assessment, and SASE/SSE Risks - Traditional Sessions
Explore digital forensics, vendor assessment, and SASE/SSE risks in infrastructure security. Learn methodologies for enhancing investigations, evaluating partners, and optimizing zero-trust security configurations.
Begin Your Journey into DFIR, Blue Team, Malware and Threat Hunting
Explore digital forensics, blue team strategies, malware analysis, and threat hunting techniques with expert guidance for cybersecurity professionals and enthusiasts.
Combating Fraud in High-End Marketplaces - Lessons from a Year-Long Battle
Dive into a developer's intense year-long battle against fraud in a high-end marketplace, exploring technical challenges, phishing tactics, and crucial lessons for safeguarding online platforms.