Potentially Unnecessary and Unwanted Programs AKA PUPs
Explore potentially unwanted programs (PUPs), their detection challenges, and mitigation strategies through real-world case studies and forensic analysis techniques.
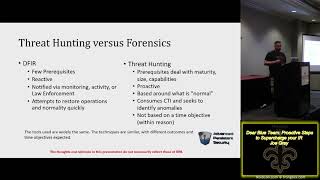
Dear Blue Team - Proactive Steps to Supercharge Your IR
Proactive strategies for enhancing incident response, covering threat intelligence, forensics, and threat hunting. Explores tools and techniques for effective cybersecurity defense.
The Future of Digital Forensics
Explore emerging trends and technologies shaping digital forensics, including AI, cloud computing, and IoT, and their impact on cybercrime investigation and evidence analysis.
IoT Forensics - The Growing Impact of the Internet of Things on Digital Forensics
Explore the impact of IoT on digital forensics, examining data sources from various devices and discussing key considerations for investigators.

Phishing Forensics - Is It Just Suspicious or Is It Malicious
Learn techniques to analyze and differentiate between suspicious and malicious phishing attempts, enhancing your cybersecurity skills and threat detection capabilities.
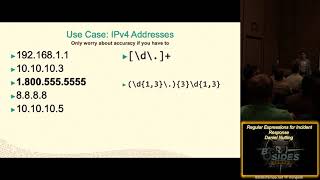
RegEx for Incident Response
Learn powerful RegEx techniques for efficient incident response, enhancing your ability to quickly analyze logs and identify security threats.
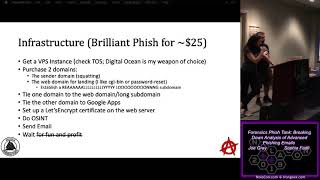
Forensics Phish Tank - Breaking Down Analysis of Advanced Phishing Emails
Explore advanced techniques for analyzing sophisticated phishing emails, enhancing your ability to detect and mitigate cyber threats in this comprehensive forensics session.
IR with Volatility Framework
Explore incident response techniques using the Volatility Framework for memory forensics and malware analysis in this informative cybersecurity presentation.
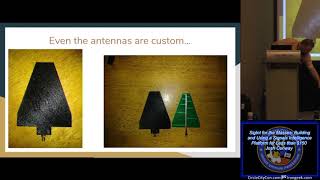
SigInt for the Masses - Building and Using a Signals Intelligence Platform for Less than 15
Learn to build and utilize a cost-effective Signals Intelligence Platform, exploring innovative techniques for gathering and analyzing signal data on a budget.
Beginning DFIR - How to Get Started with Cooties
Explore digital forensics and incident response (DFIR) basics, tools, and techniques. Learn practical skills for handling incidents, managing logs, and communicating effectively in cybersecurity scenarios.
Stable 13 - The 1995 Anonymous Cyber Profile Patrick Matthews
Explore the intriguing 1995 anonymous cyber profile of Patrick Matthews, uncovering the mysteries and implications of this early internet persona.
Dance Fancybear Dance - A Study in macOS Cat Self
Explore macOS security through the lens of art forgery, threat profiling, and red teaming. Learn practical techniques for information gathering, software development, and testing in cybersecurity.
Catching Cyber Criminals - Investigative Techniques to Identify Modern Threat Actors
Explore investigative techniques for identifying modern cyber threat actors, enhancing your ability to catch and prevent cybercrime in today's digital landscape.
Losing Our Reality - Understanding and Combating the Deep Fake Threat
Explore the deep fake threat, its implications, and strategies to combat this emerging technology. Learn detection techniques, countermeasures, and the future of digital reality.
These Artifacts Aren't Fiction
Explore Windows artifacts, browser history, and PowerShell forensics. Learn data preservation, SRUM analysis, and network resource usage for effective digital investigations.
Autopsy Module Competition Videos
Explore winning Autopsy modules: SpeechToText, AD1_Extractor, and FAMA. Discover innovative forensic tools enhancing digital investigations and evidence analysis capabilities.
Investigating Windows Subsystem for Linux - WSL Endpoints
Explore forensic artifacts and investigation techniques for compromised Windows Subsystem for Linux (WSL) endpoints, covering attacker techniques and architectural changes relevant to digital forensics professionals.
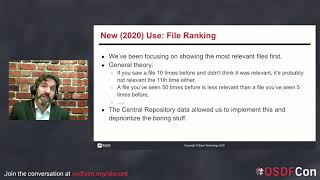
Using Past Data to Determine Relevance in Autopsy
Explore Autopsy's File Discovery UI and Central Repository for efficient digital forensics. Learn how past data analysis enhances file prioritization and streamlines investigations.
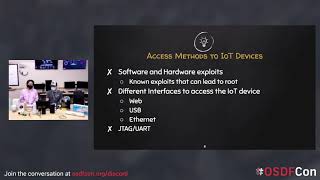
Linux Forensics for IoT - Hello World
Exploring Linux forensics techniques for IoT devices, from smart homes to security systems. Showcases research on applying digital investigation methods to various IoT platforms running Linux operating systems.
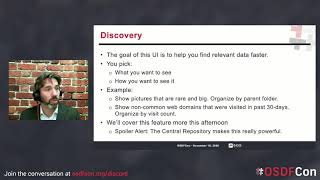
Autopsy's Year in Review - OSDFCon
Comprehensive overview of Autopsy's latest features, including new interfaces and analysis modules, highlighting advancements in digital forensics and incident response capabilities.
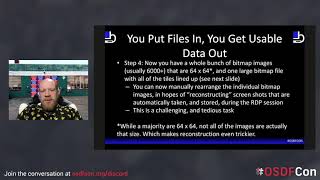
Putting Together the RDPiece
Explore RDP Bitmap Cache forensics for ransomware investigations. Learn to extract, analyze, and reconstruct crucial evidence often overlooked in digital forensics and incident response.