OS X Forensics
Explore OS X forensics techniques and methodologies for digital investigations, focusing on unique aspects of Apple's operating system and file structures.
Abstract Tools for Effective Threat Hunting
Learn effective threat hunting techniques using abstract tools, investigative processes, and data-driven observations. Develop expertise in pivoting, aggregation, and creating a knowledge base for cybersecurity investigations.
Playing in Memory - Examples of User Thievery and Hunting for Malware
Explore memory forensics techniques using Volatility and other tools to investigate user activity and hunt for malware in captured system memory.
Where Cypherpunk Meets Organized Crime - The Shifting Landscape of Underground Economies
Explore the intersection of cypherpunk ideology and organized crime, examining how underground economies are evolving in the digital age.
OSINT and Your World - A Love Story
Explore the power of Open Source Intelligence (OSINT) and its impact on personal and professional life in this engaging presentation by Michael James.
A Needle in the Cloud
Explore cloud incident response techniques, from preparation to log analysis and application forensics, enhancing your ability to detect and investigate security incidents in cloud environments.
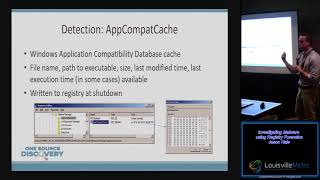
Investigating Malware Using Registry Forensics
Explore malware detection and investigation techniques using Windows Registry forensics, covering key hives, detection methods, and tools for uncovering malicious activities.
Bots, Trolls, and Warriors - The Modern Adversary Playbook
Explore the tactics of modern digital adversaries, including bots, trolls, and warriors, and learn strategies to counter their influence and protect against cyber threats.
Cybercrime Enlarged
Explore the evolution and impact of cybercrime related to pharmaceutical fraud, focusing on illegal online pharmacies and their sophisticated tactics.
Building Google for Criminal Enterprises
Explore techniques for creating specialized search engines tailored to criminal activities, examining ethical implications and potential countermeasures.
To Catch a Spy - Tyler Hudak
Explore advanced Windows persistence techniques, including registry auditing, shell extensions, and bootkits. Learn detection methods and forensic examination strategies.
Memory Based Library Loading - Someone Did That Already
Explore memory-based library loading techniques and their existing implementations, focusing on advanced cybersecurity concepts and practical applications in system exploitation.
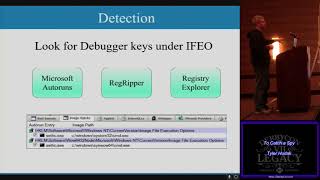
To Catch a Spy - Tyler Hudak
Explore advanced Windows persistence techniques, including registry auditing, shell extensions, and bootkits. Learn detection methods and forensic examination strategies for enhanced cybersecurity.
Love is in the Air - DFIR and IDS for WiFi Networks
Explore WiFi network security through DFIR and IDS techniques, enhancing your ability to detect and respond to wireless threats effectively.
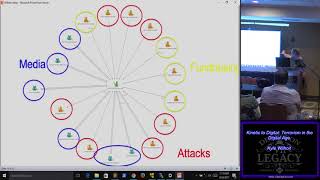
Kinetic to Digital - Terrorism in the Digital Age
Explore the evolution of cyber terrorism, from hacktivist groups to ISIS, examining their tactics, tools, and online presence in the digital age.
Learning from InfoSec Fails
Learn from InfoSec failures to improve vulnerability management, DLP, web app security, and more. Explore key topics like pattern-based protection, IoT security, and the balance between security and compliance.
Network Forensics Using Kali Linux and SANS Sift
Learn network forensics techniques using Kali Linux and SANS SIFT, covering tools and methods for investigating digital evidence and analyzing network traffic.
Forensics Technical Testimony - Doing the Heavy Lifting for the Jury
Explore effective techniques for presenting complex digital forensics evidence in court, focusing on clear communication and relatable explanations for juries.
Courtroom01 You Can Run but You Can't Hide - Bruce Anderson
Explore digital forensics techniques for uncovering hidden evidence in criminal investigations, focusing on advanced methods to track and analyze digital footprints.
Modern Day Vandals and Thieves - Wireless Edition
Explore wireless security vulnerabilities in smart homes, including network exploitation, device intelligence, and metadata analysis for potential intrusions and theft.
Phishing Forensics - Is It Just Suspicious or Is It Malicious
Explore phishing forensics techniques to distinguish suspicious from malicious emails, covering header analysis, tools, and practical strategies for effective threat assessment.