Detecting the Undetectable - What You Need to Know About OSINT
Learn essential techniques for Open Source Intelligence (OSINT) gathering, enhancing your ability to detect and analyze hidden information in the digital landscape.
Why Cybercriminals Are Following The Money Into Online Video Games
Explore how cybercriminals exploit online gaming ecosystems for financial gain, examining vulnerabilities and emerging threats in virtual economies.
Fantastic OSINT and Where to Find It
Explore 306 fantastic Open Source Intelligence (OSINT) resources and techniques with expert Tony Robinson, enhancing your information gathering and analysis skills.
Anti Forensics - int0x80 of Dual Core
Explore anti-forensics techniques for Android devices, covering encryption, hardware forensics, and strategies to protect sensitive data from forensic analysis.
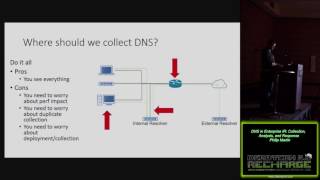
DNS in Enterprise IR Collection Analysis and Response
Explore DNS logging techniques for enterprise incident response, covering data collection, analysis, and response strategies to enhance network security and threat detection.
Anti Forensics AF
Explore anti-forensics techniques with int0x80 of Dual Core, delving into methods to counter digital forensic investigations and protect digital privacy.
Yara Rule QA - Can't I Write Code to Do This for Me?
Learn techniques for efficient Yara rule management, including file organization, rule separation, and quality assurance practices to enhance malware detection capabilities.
Mobile Device Forensics
Explore mobile device forensics, covering iOS, Android, BlackBerry, and Windows Mobile. Learn about technical specifications, file systems, artifacts, and limitations in digital investigations.
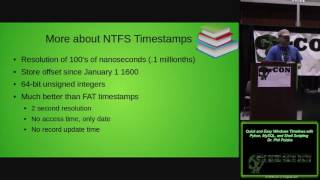
Quick and Easy Windows Timelines with Python, MySQL, and Shell Scripting
Learn to create efficient Windows timelines using Python, MySQL, and shell scripting for enhanced digital forensics and incident response capabilities.
Evidence Collection - Part 1
Comprehensive guide to digital forensics principles, procedures, and best practices for evidence collection, emphasizing integrity, documentation, and proper handling techniques.
Evidence Collection
Learn advanced techniques for digital evidence collection, focusing on best practices and legal considerations in cybercrime investigations.
Key to Forensic Success - Examination Planning
Learn essential strategies for effective forensic examination planning, focusing on key elements that contribute to successful digital investigations.
Windows Timelines in Minutes
Aprenda a extrair e analisar timestamps de sistemas Windows para investigações forenses digitais, incluindo técnicas para criar e visualizar linhas do tempo de atividades de arquivos.
Network Forensics Using Kali Linux and SANS Sift
Explore network forensics techniques using Kali Linux and SANS SIFT, learning essential skills for digital investigations and cybersecurity analysis.
Mobile Forensics - An Introduction
Explore mobile device forensics techniques, evidence collection, and analysis methods for criminal investigations and digital security.
Knowing the Enemy - Creating a Cyber Threat Actor Attribution Program
Explore cyber threat actor attribution, from understanding attacker behaviors to implementing effective monitoring and investigative techniques for enhanced cybersecurity.
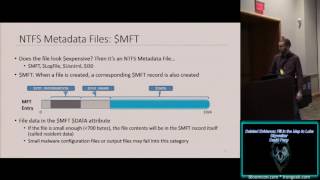
Deleted Evidence - Fill in the Map to Luke Skywalker
Explore techniques for recovering deleted attacker files, analyzing NTFS metadata, and leveraging Windows artifacts to reconstruct evidence in digital forensics investigations.
Black Box Mac OSX Forensics
Explore Mac OSX forensics techniques for uncovering hidden data and analyzing system artifacts, enhancing your digital investigation skills in Apple environments.
Honey I Stole Your C2 Server - A Dive into Attacker Infrastructure
Explore attacker infrastructure through a Mandiant investigation, covering Metasploit indicators, command and control, encoding, and insights into attacker techniques and tools.
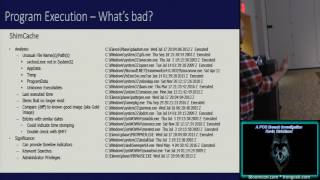
A POS Breach Investigation
Explore POS breach investigation techniques, covering malware analysis, network examination, and forensic methods to detect and respond to retail cybersecurity incidents.
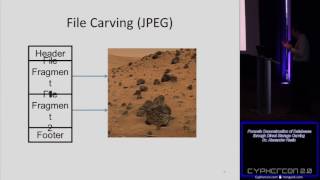
Forensic Deconstruction of Databases through Direct Storage Carving
Explore forensic database deconstruction techniques, including file carving, parameter detection, and stochastic forensics. Learn about database components, caching, and evidence preservation.