C3CM - Defeating the Command Control and Communications of Digital Assailants
Explore strategies to disrupt and defeat digital attackers' command, control, and communication systems, enhancing cybersecurity defenses against sophisticated threats.
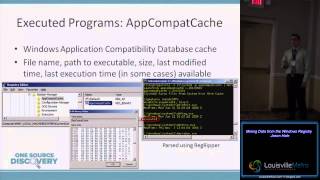
Mining Data from the Windows Registry
Explore Windows Registry forensics, including key hives, data extraction, program execution tracking, file access analysis, and anti-forensics techniques for cybersecurity professionals.
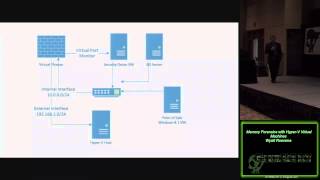
Memory Forensics with Hyper V Virtual Machines
Explore memory forensics techniques for Hyper-V virtual machines, enhancing your ability to investigate and analyze digital evidence in virtualized environments.
A Basic Guide to Advanced Incident Response
Advanced incident response techniques for effective cybersecurity defense, covering intelligence-driven strategies, active defense, network forensics, and collaborative approaches to enhance organizational security posture.
OSXCollector Forensic Collection and Automated Analysis for OS X
Learn forensic collection and automated analysis techniques for OS X systems using OSXCollector, enhancing your digital investigation skills for Apple environments.
Human Hunting - Sean Gillespie
Explore advanced cybersecurity techniques for detecting and countering human adversaries, focusing on automation, threat research, and practical hunting strategies using GRR.
ISLET - Isolated, Scalable, & Lightweight Environment for Training
Explore ISLET: a containerized environment for scalable, isolated training. Learn about its benefits, use cases, security features, and implementation using Docker.
BREAKING in BAD - I’m the One Who Doesn’t Knock
Explore physical security vulnerabilities and social engineering tactics with expert Jayson Street, learning how to identify and mitigate risks in various environments.
Of History and Hashes
Explore the evolution of cryptographic hashes, their applications in security, and common vulnerabilities. Gain insights into hash functions' history and practical implications.
Mobile Forensics and its Anatomy of Extractions
Explore mobile forensics, extraction techniques, and tools for Android and Apple devices. Learn about device seizure, evidence analysis, and live demonstration of extraction processes.
Getting Started - Help Me Help You
Learn essential incident response techniques, from memory analysis to registry examination, with practical tools and real-world scenarios to enhance your cybersecurity skills and preparedness.
When Steganography Stops Being Cool
Explore the limitations and potential risks of steganography in digital security, examining its effectiveness and vulnerabilities in modern cybersecurity landscapes.
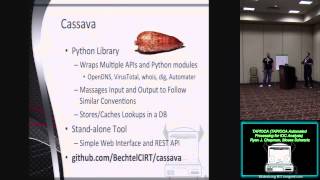
TAPIOCA Automated Processing for IOC Analysis
Explore automated processing for IOC analysis with TAPIOCA, covering data pivoting, OPSEC, atomic indicators, and tools for efficient threat intelligence gathering and analysis.
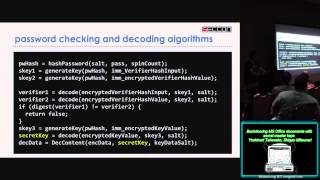
Backdooring MS Office Documents with Secret Master Keys
Learn techniques for embedding hidden master keys in Microsoft Office documents, exploring potential security vulnerabilities and countermeasures.
Poppin Digital Locks
Explore digital lock vulnerabilities and hacking techniques with expert insights on security weaknesses and potential exploits in electronic locking systems.
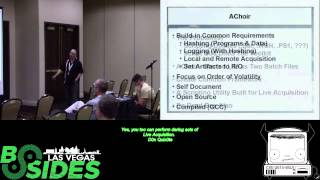
Yes You Too Can Perform Daring Acts of Live Acquisition Don Quixote
Learn techniques for performing live acquisition in digital forensics, focusing on daring methods and practical applications.
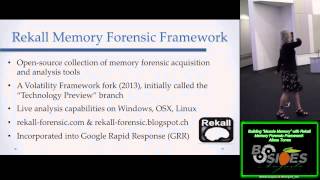
Building a Muscle Memory with Rekall Memory Forensic Framework
Explore memory forensics using Rekall framework. Learn process enumeration, malware identification, and rootkit detection techniques. Gain practical skills for digital investigations and incident response.
Dynamic Analysis of Flash Files
Dynamic analysis techniques for Flash files, exploring methods to uncover vulnerabilities and potential security risks in SWF content.
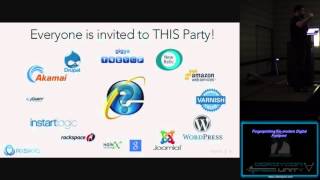
Fingerprinting the Modern Digital Footprint
Explore modern digital footprinting techniques, including decentralization challenges, third-party security risks, and innovative methods for mapping and analyzing digital presence.
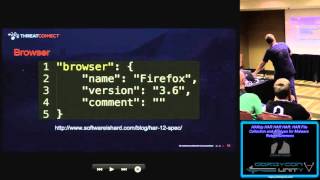
The 3 Way16 Hardy Har Har Har Har File Collection and Analysis for Malware
Explore HAR file collection and analysis techniques for malware detection, focusing on innovative approaches to enhance cybersecurity and threat intelligence.
Memory Acquisition in Digital Forensics and Incident Response
Learn memory acquisition techniques for digital forensics, including hardware and software methods, challenges, and anti-forensic considerations in this comprehensive overview.