Heavy Hitter Estimation over Set-Valued Data with Local Differential Privacy
Explore local differential privacy for heavy hitter estimation on set-valued data. Learn about randomized response, RAPPOR, and the LDPMiner framework for privacy-preserving data analysis.
Advanced Probabilistic Couplings for Differential Privacy
Explore advanced probabilistic couplings for differential privacy, covering composition theorems, program logic, and accuracy-dependent privacy in this in-depth technical presentation.
How to Build with Data Trust and Privacy as a Baseline
Explore tactical approaches for data stewardship, privacy, and trust in software development, including differential privacy techniques, in the face of growing regulations.
Privid - Practical, Privacy-Preserving Video Analytics Queries
Explore privacy-preserving video analytics with Privid, a system enforcing duration-based privacy for public surveillance footage while maintaining utility for various applications.
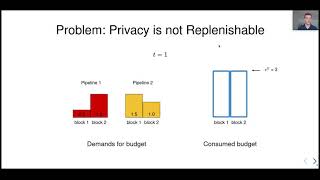
Privacy Budget Scheduling
Explores privacy budget scheduling in machine learning, introducing PrivateKube for managing differential privacy as a resource. Presents DPF algorithm for fair allocation of non-replenishable privacy budgets in ML workloads.
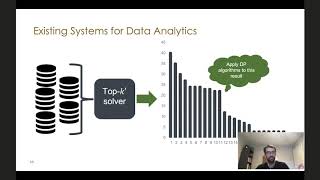
A Differentially Private Data Analytics API at Scale
LinkedIn's privacy system uses differential privacy to protect member data while providing audience engagement insights, enabling marketing analytics with user-level privacy guarantees and strict budget management.
Improving Usability of Differential Privacy at Scale
Explore a framework enhancing Differential Privacy usability, allowing practitioners to visualize privacy-utility trade-offs and simplify complex concepts for better implementation and understanding.
Learning Differentially Private Mechanisms
Explore techniques for developing privacy-preserving algorithms and mechanisms, focusing on differential privacy principles and their practical applications.
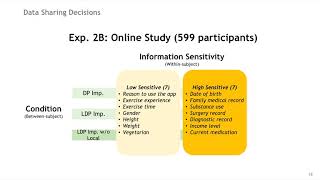
Towards Effective Differential Privacy Communication for Users' Data Sharing Decision and Comprehension
Exploring user comprehension and data sharing decisions in differential privacy, focusing on effective communication strategies for laypersons in health app settings.
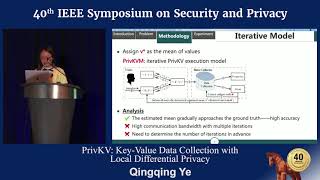
PrivKV - Key Value Data Collection with Local Differential Privacy
Explores local differential privacy for key-value data collection, proposing PrivKV, PrivKVM, and PrivKVM+ solutions to improve estimation accuracy while preserving user privacy in distributed data collection.
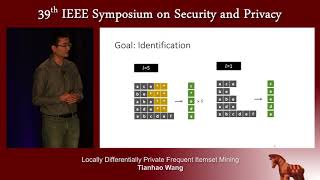
Locally Differentially Private Frequent Itemset Mining
Explore techniques for mining frequent itemsets while preserving user privacy through Local Differential Privacy. Learn about PSFO protocols and the SVIM method for improved efficiency and accuracy.
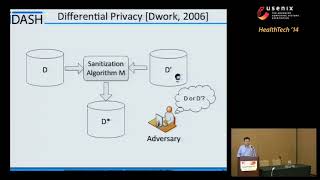
Differentially Private Genome Data Dissemination Through Top-Down Specialization
Innovative approach for sharing genomic data while preserving privacy through differential privacy techniques. Explores block splitting, top-down subdivision, and noise addition to protect sensitive information while maintaining data utility.
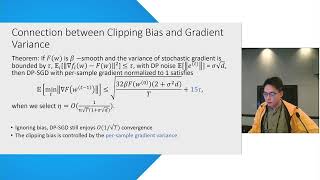
A Theory to Instruct Differentially-Private Learning via Clipping Bias Reduction
Explore a novel theory for enhancing differentially-private learning through clipping bias reduction, offering insights into privacy-preserving machine learning techniques.
Demystifying Privacy Preserving Computing
Explore cutting-edge Privacy-Preserving Computing techniques like secure multiparty computation, fully homomorphic encryption, and differential privacy for protecting data confidentiality during processing.
Deep Learning with Differential Privacy
Explore deep learning with differential privacy, focusing on techniques to protect data privacy while maintaining model accuracy in machine learning applications.
Differentially Private Bayesian Programming
Explore techniques for implementing differential privacy in Bayesian programming, enhancing data analysis while preserving individual privacy in statistical computations.
Differential Privacy as a Mutual Information Constraint
Explore differential privacy through mutual information constraints, presented by Princeton researchers at ACM's Computer and Communications Security conference.
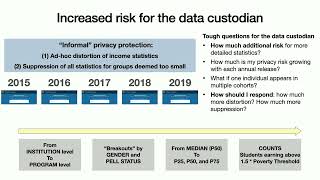
Negotiating Privacy - Utility Trade-Offs under Differential Privacy
Explore privacy/utility trade-offs in differential privacy through a real IRS-DOE case study, examining challenges faced by data custodians when establishing data release standards.
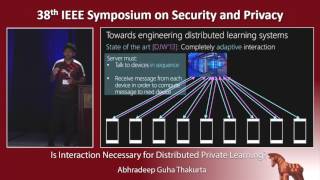
Is Interaction Necessary for Distributed Private Learning?
Explores the necessity of interaction in locally differentially-private algorithms for convex optimization, presenting new algorithms and lower bounds on noninteractive approaches.
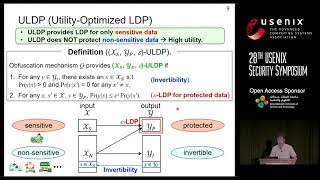
Utility-Optimized Local Differential Privacy Mechanisms for Distribution Estimation
Explores utility-optimized local differential privacy mechanisms for distribution estimation, enhancing data utility while maintaining privacy for sensitive information.
Manipulation Attacks in Local Differential Privacy
Explore manipulation attacks in local differential privacy, examining vulnerabilities and potential countermeasures in privacy-preserving data collection systems.