Preserving Data Privacy in Federated Learning - Xiaokui Xiao
Explore privacy-preserving techniques in federated learning, including differential privacy, model privacy, and vertical factory learning, with insights on future developments and challenges.
Finding Fairness - Incorporating Societal Values in Computer Algorithms
Exploring algorithmic fairness and privacy in computer science, addressing concerns about incorporating societal values into technology as it increasingly impacts our lives.
Hacking AI - Security & Privacy of Machine Learning Models
Explore adversarial machine learning with Prof. Dan Boneh, examining security challenges in AI models, defenses against attacks, and the balance between accuracy and privacy in ML systems.
Getting Robust - Securing Neural Networks Against Adversarial Attacks
Explore adversarial attacks on machine learning, their impact, and defense strategies. Learn to incorporate adversarial considerations in research and development for more robust AI systems.
The Privacy Considerations of Production Machine Learning
Explore state-of-the-art research on privacy in machine learning, including estimating and defending against privacy leakage, secure collaboration, and machine unlearning for GDPR compliance.
HoloClean and Kamino - Structured Learning for Private Data Generation
Explore structured learning for private data generation using HoloClean and Kamino frameworks. Learn to preserve data correlations while ensuring privacy in synthetic data instances.
How MLOps Tools Will Need to Adapt to Responsible and Ethical AI - Stay Ahead of the Curve
Explore ethical AI guardrails for MLOps platforms, focusing on GDPR compliance, data privacy, and future regulatory requirements. Learn to implement responsible AI practices in machine learning operations.
Imitation Games - Avi Wigderson
Explore cryptography, randomness, and privacy with Avi Wigderson in this talk on imitation games, covering modern encryption, pseudorandomness, and differential privacy.
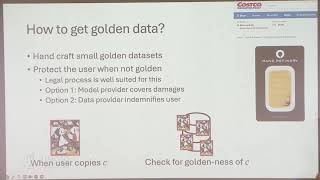
Differential Privacy in the Clean Room - Copyright Protections for Generative AI
Explore the intersection of differential privacy and copyright law in AI, examining how mathematical frameworks can prevent infringement while enabling generative model development.
Differentially Private Synthetic Data for Private LLM Training
Explore cutting-edge techniques for generating private synthetic data in LLM training, focusing on differential privacy methods and their practical applications in AI development.
Gaussian Differential Privacy
探索高斯差分隐私:一种新的隐私保护方法,提供更精确的组合分析和子采样隐私放大,并通过中心极限定理证明其在组合下的收敛性。
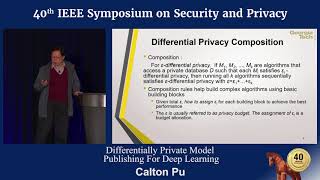
Differentially Private Model Publishing for Deep Learning
Explore techniques for publishing deep learning models with differential privacy, optimizing privacy loss and model accuracy through concentrated differential privacy and dynamic budget allocation.
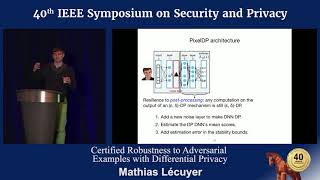
Certified Robustness to Adversarial Examples with Differential Privacy
Explore certified defense against adversarial examples using differential privacy. Scalable solution for large networks and datasets, providing robustness guarantees for various model types.
Adversary Instantiation - Lower Bounds for Differentially Private Machine Learning
Explore lower bounds for differentially private machine learning, focusing on DPSGD, membership inference, and gradient poisoning attacks in this IEEE presentation.
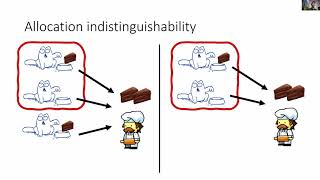
Private Resource Allocators and Their Applications
Introduces private resource allocators to prevent allocation-based side-channel attacks in systems like anonymous messaging, with various constructions offering different privacy guarantees and trade-offs in efficiency.
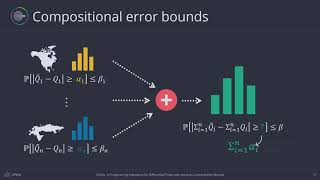
A Programming Framework for Differential Privacy with Accuracy Concentration Bounds
Explore a programming framework for differential privacy, balancing data protection and analysis accuracy through novel static tracking and taint analysis techniques.
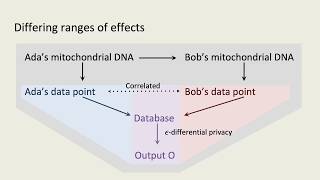
SoK- Differential Privacy as a Causal Property
Explores differential privacy as a causal property, offering a simple characterization without data independence assumptions and resolving prior disagreements about its consequences and applications.
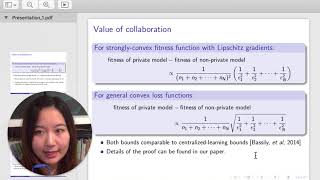
The Value of Collaboration in Convex Machine Learning with Differential Privacy
Explores collaborative machine learning on distributed private data using differentially-private gradients, quantifying trade-offs between privacy and utility, and validating performance predictions with real-world financial datasets.
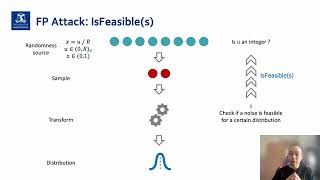
Are We There Yet? Timing and Floating-Point Attacks on Differential Privacy Systems
Explore timing and floating-point vulnerabilities in differential privacy systems, uncovering potential privacy leaks and discussing mitigation strategies for enhanced data protection.
DP-Sniper - Black-Box Discovery of Differential Privacy Violations Using Classifiers
Explore a novel approach to detect differential privacy violations using classifiers, enhancing data protection and privacy in machine learning systems.
Theory Seminar - Differential Privacy in Theory and Practice, Abie Flaxman
Explore differential privacy in the US Census, its impact on data accuracy, and potential improvements. Insights from analyzing test runs and 1940 data application.