Premonitions of Public Data for Private ML
Explore how public data pre-training enhances private machine learning, examining its impact on accuracy, zero-shot learning, and the future of privacy-preserving AI techniques.
Differentially Private Sampling from Distributions
Explore techniques for private sampling from distributions, focusing on accuracy, privacy guarantees, and applications in statistical data analysis.
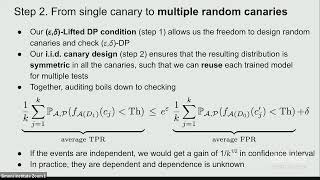
Fundamental Trade-Offs in FL-FA - Sparsity - DP - Communication Constraints
Explore trade-offs in federated learning, focusing on sparsity, differential privacy, and communication constraints. Gain insights into balancing these factors for effective machine learning.
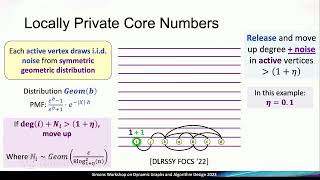
Practical Dynamic Graph Algorithms - Data Structures and Connections Between Models
Explore efficient data structures and techniques for dynamic graph algorithms across multiple computational models, focusing on k-core decomposition, densest subgraph, and triangle counting problems.
Federated Learning with Formal User-Level Differential Privacy Guarantees
Explore federated learning with differential privacy guarantees, covering key concepts, challenges, and algorithms like DP-SGD and DP-FTRL, with insights on privacy-utility trade-offs and future directions.
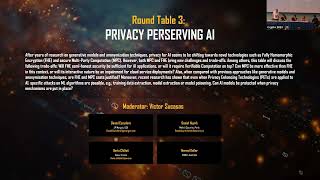
Privacy Preserving AI in Cryptography - Round Table Discussion
Explore privacy-preserving AI techniques in this roundtable discussion from the Glowing Hot Topics in Cryptography workshop, focusing on the intersection of cryptography and artificial intelligence.
Privacy-Preserving Machine Learning Workshop 2023 - Contributed Talks Session II
Explore cutting-edge research in privacy-preserving machine learning through expert presentations at the PPML 2023 workshop, covering innovative techniques and applications in the field.
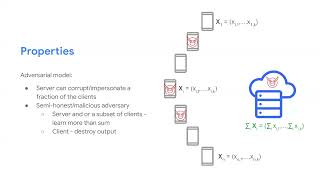
Privacy-Preserving Machine Learning - Invited and Contributed Talks
Explore privacy-preserving machine learning with expert Mariana Raykova and contributed talks from PPML 2023, covering cutting-edge research and advancements in secure AI and data protection.
Privacy-Preserving Machine Learning Workshop - Invited and Contributed Talks
Explore cutting-edge research in privacy-preserving machine learning with expert talks and contributions at PPML 2023, covering innovative techniques and advancements in the field.
Differentially Oblivious Database Joins - Overcoming the Worst-Case Curse of Fully Oblivious Algorithms
Explore innovative techniques for database joins that balance privacy and efficiency, overcoming limitations of fully oblivious algorithms in worst-case scenarios.
The Ethical Algorithm - Designing Socially Aware AI
Exploring ethical challenges in AI and machine learning, including data privacy, algorithmic bias, and decision-making transparency. Discusses recent research on socially responsible algorithm design.
The Art and Tech of Generating Secure and Authentic Synthetic Data
Explore techniques for creating secure synthetic data, including redaction, anonymization, and differential privacy, with practical examples and future developments.
Securing ML Workloads with Kubeflow and MLOps - Pwned By Statistics
Learn to secure machine learning workloads using Kubeflow and MLOps. Explore techniques like model extraction, hidden data attacks, and leakage detection to protect your ML pipelines and models.
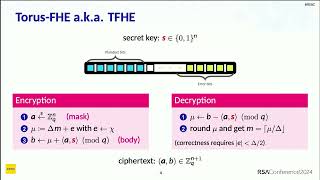
Homomorphic Encryption - TFHE Public-Key Encryption and Differential Privacy
Explore TFHE public-key encryption and differential privacy in approximate homomorphic encryption with experts from Zama and Royal Holloway, University of London.
Efficiently Computing Similarities to Private Datasets
Explore advanced techniques for computing similarities to private datasets, focusing on extroverted sublinear algorithms and their applications in data privacy.
Model Explanations with Differential Privacy
Explore techniques for generating privacy-preserving explanations of machine learning models, balancing transparency with data protection in AI systems.
When Machine Learning Isn't Private
Exploring privacy risks in machine learning models, focusing on data leakage and extraction techniques. Discusses challenges in prevention and potential solutions for researchers and practitioners.
How Anonymous Is My Anonymized Data?
Explores data anonymization challenges, focusing on relationships between fields and external information that can compromise privacy. Discusses risk assessment and strategies for protecting sensitive data.
Differential Privacy at Scale - Uber and Berkeley Collaboration - USENIX Enigma - 2018
Collaboration between Uber and Berkeley researchers on scaling differential privacy, resulting in open-source releases and practical solutions for privacy-preserving data analysis in real-world scenarios.
Chasing Your Long Tails - Differentially Private Prediction in Health Care Settings
Explore differential privacy in healthcare ML, addressing unique challenges, extreme tradeoffs, and fairness considerations for underrepresented groups in medical datasets.
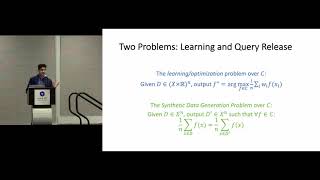
How to Use Heuristics for Differential Privacy
Learn about differential privacy heuristics, their properties, and applications in machine learning. Explore modular design, universal identification, and privacy analysis techniques.