CALM - Consistent Adaptive Local Marginal for Marginal Release under Local Differential Privacy
Explore constructing marginal tables with Local Differential Privacy, ensuring individual data protection without third-party reliance. Learn CALM protocol for consistent, adaptive local marginal release.
The Role of Interactivity in Local Differential Privacy
Explore the impact of interactivity on local differential privacy, examining its significance in data protection and privacy-preserving algorithms.
Locally Private Histograms in All Privacy Regimes
Explore frequency estimation in data analysis, focusing on local differential privacy. Learn about algorithms, error bounds, and the intriguing low-privacy regime in histogram computation.
On Robustness and Local Differential Privacy
Explore robustness and local differential privacy in mathematical statistics with Thomas Berrett's insightful conference talk at CIRM.
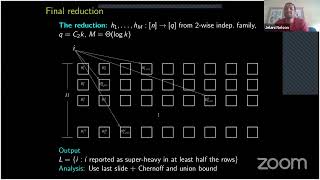
Jelani Nelson- Forty Years of Frequent Items
Explore forty years of frequent items algorithms, from classic approaches to modern techniques, including turnstile streaming, heavy hitters, and local differential privacy.
Heavy Hitter Estimation over Set-Valued Data with Local Differential Privacy
Explore local differential privacy for heavy hitter estimation on set-valued data. Learn about randomized response, RAPPOR, and the LDPMiner framework for privacy-preserving data analysis.
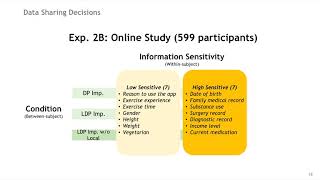
Towards Effective Differential Privacy Communication for Users' Data Sharing Decision and Comprehension
Exploring user comprehension and data sharing decisions in differential privacy, focusing on effective communication strategies for laypersons in health app settings.
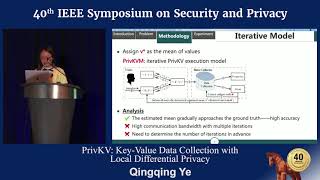
PrivKV - Key Value Data Collection with Local Differential Privacy
Explores local differential privacy for key-value data collection, proposing PrivKV, PrivKVM, and PrivKVM+ solutions to improve estimation accuracy while preserving user privacy in distributed data collection.
Locally Differentially Private Frequent Itemset Mining
Explore techniques for mining frequent itemsets while preserving user privacy through Local Differential Privacy. Learn about PSFO protocols and the SVIM method for improved efficiency and accuracy.
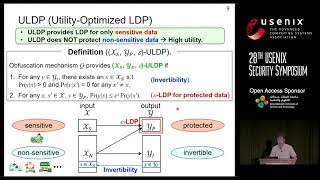
Utility-Optimized Local Differential Privacy Mechanisms for Distribution Estimation
Explores utility-optimized local differential privacy mechanisms for distribution estimation, enhancing data utility while maintaining privacy for sensitive information.
Manipulation Attacks in Local Differential Privacy
Explore manipulation attacks in local differential privacy, examining vulnerabilities and potential countermeasures in privacy-preserving data collection systems.
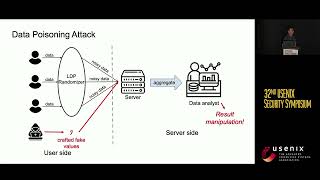
Fine-Grained Poisoning Attack to Local Differential Privacy Protocols for Mean and Variance Estimation
Explores a new fine-grained attack on local differential privacy protocols, allowing manipulation of mean and variance estimations. Discusses security-privacy consistency and proposes a defense method.
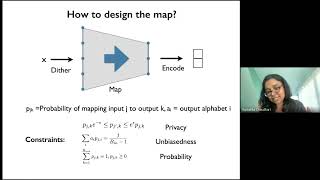
Privacy-Aware Compression for Federated Learning
Explore privacy-aware compression techniques for federated learning, addressing challenges and implementing local differential privacy mechanisms to enhance data protection in collaborative AI.
User-Level and Federated Local Differential Privacy in Statistical Inference
Explore fundamental statistical inference challenges in distributed data systems with differential privacy constraints across servers and users, focusing on privacy-preserving information transmission.

Black Hat Europe 2024
Black Hat Europe 2024