On Robustness and Local Differential Privacy
Explore robustness and local differential privacy in mathematical statistics with Thomas Berrett's insightful conference talk at CIRM.
Privacy: Definitions, Procedures, and Open Problems
Explore privacy definitions, procedures, and open problems in mathematical statistics with John Duchi's comprehensive conference talk.
Machine Unlearning and Privacy Implications - Differential Privacy for ML
Explore privacy implications of machine unlearning, including threat models, deletion inference, and experimental results in this Google TechTalk on differential privacy for ML.
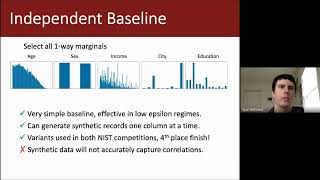
Marginal-based Methods for Differentially Private Synthetic Data - Differential Privacy for ML Series
Explore marginal-based methods for generating differentially private synthetic data, covering mechanisms, selection algorithms, and empirical findings.
Generating Synthetic Tabular Data that is Differentially Private
Explore approaches to applying differential privacy in generating synthetic tabular data, including measuring low-dimensional distributions and learning graphical model representations for enhanced data privacy.
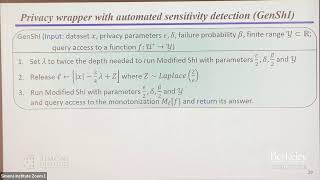
Privately Evaluating Untrusted Black-Box Functions
Explore tools for sharing sensitive data with untrusted analysts, focusing on differentially private algorithms and privacy wrappers for black-box functions on datasets.
Small Space Differentially Private Graph Algorithms in the Continual Release Model
Explore sublinear space differentially private graph algorithms for continual release, covering densest subgraphs, k-core decomposition, maximum matching, and vertex cover.
Deep Learning with Differential Privacy
Explore deep learning techniques for privacy-preserving machine learning, focusing on neural networks and differential privacy in crowdsourced, sensitive datasets.
Using Apache Spark and Differential Privacy for 2020 Census Data Protection
Explore how Apache Spark and differential privacy protect 2020 Census data, balancing accuracy and confidentiality. Learn about the innovative TopDown Algorithm and custom monitoring systems.
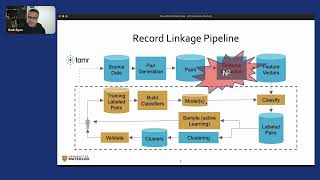
How ML-Powered Data Cleaning Streamlines the AI Pipeline
Explore ML-powered data cleaning techniques to streamline AI pipelines, automate labor-intensive tasks, and overcome impediments in data preparation for efficient data science workflows.

Compute Engine Testing with Synthetic Data Generation
Explore Meta's innovative testing framework using privacy-safe synthetic data for compute engines, enhancing regression detection, test coverage, and release cycles in data warehousing.
Data Augmentation MCMC for Bayesian Inference from Privatized Data
Explore data augmentation MCMC for Bayesian inference from privatized data, focusing on differential privacy challenges and solutions in statistical analysis.
Foundations II
Explore advanced cryptography concepts including derandomization, encryption schemes, differential privacy, and collective coin tossing for secure communication and data protection.
Certified Randomness from Quantum Supremacy
Explore quantum supremacy, certified randomness, and their implications in cryptography with Scott Aaronson's insightful presentation on cutting-edge quantum computing concepts.
Cryptographically Protected Database Search
Exploration of cryptographically protected database search systems, analyzing primitive operations, current implementations, potential attacks, and future directions for enhancing data security and functionality.
Trustworthy Machine Learning: Challenges and Frameworks
Exploring the security challenges in machine learning, this talk discusses strategies for building trustworthy AI systems by analyzing data influence, addressing vulnerabilities, and enhancing interpretability.
Privacy-Preserving Algorithms for Decentralised Collaborative Learning - Dr Aurélien Bellet
Explore privacy-preserving algorithms for decentralized collaborative learning, focusing on large-scale machine learning, distributed methods, and privacy protection in connected device data analysis.
Federated Heavy Hitters Discovery with Differential Privacy
Explore federated learning, differential privacy, and heavy hitters discovery in this talk by Peter Kairouz. Learn about multiparty computation, open research, and practical applications in data analysis.
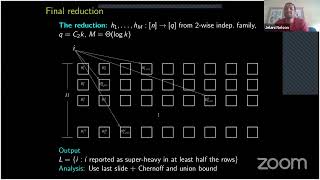
Jelani Nelson- Forty Years of Frequent Items
Explore forty years of frequent items algorithms, from classic approaches to modern techniques, including turnstile streaming, heavy hitters, and local differential privacy.
How to Allow Deep Learning on Your Data Without Revealing Your Data
Exploring secure deep learning on private data without revealing it, discussing InstaHide and TextHide methods, their applications in Federated Learning, and addressing potential security concerns.
Trustworthy Deep Learning
Explore robust, accurate, efficient, and private deep learning with theoretical guarantees, drawing insights from differential equations for trustworthy AI applications.