High-Assurance Cryptography in the Spectre Era
Explore cutting-edge cryptography techniques addressing Spectre vulnerabilities, focusing on constant-time implementations and speculative execution semantics for enhanced security.
Invisible Probe - Timing Attacks with PCIe Congestion Side-channel
Explore timing attacks using PCIe congestion side-channels, including challenges, contributions, experiments, and potential mitigations in this IEEE presentation.
Zero Knowledge for Everything and Everyone - Fast ZK Processor with Cached ORAM for ANSI C Programs
Explore fast ZK processors with cached ORAM for ANSI C programs, enhancing efficiency in zero-knowledge proofs and expanding their applications across various domains.
Diogenes: Lightweight Scalable RSA Modulus Generation with a Dishonest Majority
Explore lightweight RSA modulus generation with a dishonest majority, covering protocol design, secure multiplication, and zero-knowledge constraints for enhanced cryptographic security.
Lockable Signatures for Blockchains - Scriptless Scripts for All Signatures
Explore innovative blockchain signature techniques, including lockable signatures and scriptless scripts, to enhance payment channels and cross-currency transactions for improved security and efficiency.
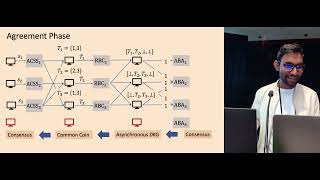
Practical Asynchronous Distributed Key Generation
Explore asynchronous distributed key generation, its applications, challenges, and performance in this technical presentation on cryptographic protocols and distributed systems.
Spiral- Fast, High-Rate Single-Server PIR via FHE Composition
Explore innovative PIR protocols using FHE composition, focusing on SPIRAL's efficiency and applications in high-rate, single-server scenarios.
What Cryptographic Library Developers Think About Timing Attacks
Explore cryptographic library developers' perspectives on timing attacks, their mitigation strategies, and the challenges in implementing secure cryptographic systems.
Optimized Honest-Majority MPC for Malicious Adversaries - Breaking the 1 Billion-Gate Per Second Barrier
Explore cutting-edge techniques for optimizing secure multiparty computation, achieving unprecedented speeds of over 1 billion gates per second in honest-majority scenarios with malicious adversaries.
On the Practicality of Cryptographically Enforcing Dynamic Access Control Policies in the Cloud
Explores the practical challenges of implementing cryptographic access control for cloud data, highlighting computational costs and bottlenecks in dynamic scenarios.
Downgrade Resilience in Key-Exchange Protocols
Explore downgrade attacks in key-exchange protocols, their causes, and strategies for achieving downgrade security. Learn about vulnerabilities and protective measures in widely-used protocols like TLS.
GraphSC: Parallel Secure Computation Made Easy
Parallel secure computation framework for efficient, oblivious execution of graph-based algorithms on large datasets, enabling practical big data analysis with minimal privacy leakage.
Simple High-Level Code for Cryptographic Arithmetic - With Proofs, Without Compromises
Innovative approach to implementing cryptographic arithmetic using high-level code with machine-checked proofs, achieving competitive performance across multiple CPU architectures and prime fields.
Formally Verified Cryptographic Web Applications in WebAssembly
Explore formal verification of cryptographic web apps in WebAssembly, focusing on compiling Low* to WebAssembly for compact, auditable code. Includes case studies on WHACL* and LibSignal*.
SoK - General Purpose Frameworks for Secure Multi-Party Computation
Explore secure multi-party computation frameworks, their capabilities, and challenges. Learn about high-level abstractions for executing MPC protocols on arbitrary functions across various systems.
Blind Certificate Authorities
Explore building blind certificate authorities for anonymous systems, focusing on binding email addresses to public keys without revealing identities. Introduces secure channel injection protocols and demonstrates practical implementation.
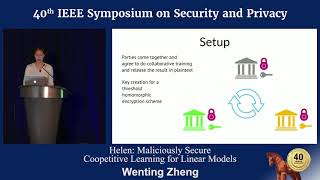
Helen - Maliciously Secure Coopetitive Learning for Linear Models
Explore secure collaborative machine learning with Helen, a system enabling multiple parties to train linear models without revealing sensitive data, addressing privacy concerns in competitive environments.
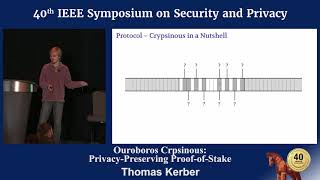
Ouroboros Crypsinous Privacy Preserving Proof of Stake
Explore privacy-preserving proof-of-stake blockchain protocol, focusing on adaptive security and novel cryptographic techniques for enhanced privacy in decentralized systems.
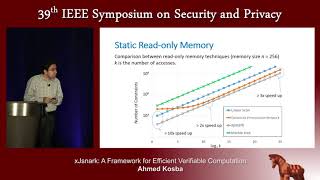
XJsnark - A Framework for Efficient Verifiable Computation
Explore efficient verifiable computation with xJsnark framework. Learn circuit-friendly algorithms, optimizations for integer arithmetic, and techniques to minimize redundant computations in cloud and cryptocurrency applications.
EverCrypt - A Fast, Verified, Cross-Platform Cryptographic Provider
Comprehensive, verified cryptographic provider offering high-performance functionalities with agility and multiplexing. Demonstrates effective composition of C and assembly, outperforming unverified implementations in various algorithms.
ZEXE - Enabling Decentralized Private Computation
Explore ZEXE, a system enabling private, efficient decentralized computation on ledgers. Learn about its innovative approach to transaction validation and privacy preservation in blockchain applications.