Obvious in Hindsight - From Side Channel Attacks to the Security Challenges Ahead
Explore side channel attacks and future security challenges with cryptography expert Paul Kocher in this insightful invited talk from Crypto and CHES 2016.

QcBits - Constant Time Small Key Code Based Cryptography
Explore constant-time, small-key code-based cryptography with QcBits, focusing on efficient implementation and security against side-channel attacks.
Software Implementation of Koblitz Curves Over Quadratic Fields
Explore efficient software implementation of Koblitz curves over quadratic fields, covering storage techniques and interleaving for enhanced performance.
Towards Easy Leakage Certification
Explore leakage certification techniques for cryptographic implementations, focusing on estimation errors and easy certification methods for enhanced security.
Vatican - Vetted, Authenticated CAN Bus
Explore secure CAN bus communication with vatiCAN, addressing challenges in automotive networks through innovative authentication and backward compatibility solutions.
A Practical Cryptanalysis of the Algebraic Eraser
Practical cryptanalysis of the Algebraic Eraser, exploring group theory and new approaches to break this cryptographic scheme.
Adaptive Versus Non Adaptive Strategies in the Quantum Setting with Applications
Explore quantum strategies, comparing adaptive and non-adaptive approaches, and their applications in cryptography and information theory.
A Subfield Lattice Attack on Overstretched NTRU Assumptions - Cryptanalysis of Some FHE and Graded Encryption Schemes
Explore cryptanalysis techniques for overstretched NTRU assumptions, focusing on subfield lattice attacks and their implications for FHE and Graded Encoding schemes.
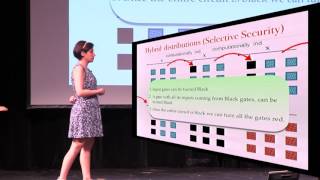
Adaptively Secure Garbled Circuits from One Way Functions
Explore adaptive security in garbled circuits, examining complexity, hybrid approaches, and encryption strategies for enhanced cryptographic protocols.
Adversary Dependent Lossy Trapdoor Function from Hardness of Factoring Semi Smooth RSA Subgroup Modu
Explores a novel cryptographic construction based on factoring semi-smooth RSA subgroup moduli, presenting an adversary-dependent lossy trapdoor function with potential applications in secure systems.
Crypto at Scale
Explore cryptography challenges at scale, including Heartbleed and Poodle vulnerabilities, with insights on security architecture and practical solutions for large-scale systems.
Annihilation Attacks for Multilinear Maps - Cryptanalysis of Indistinguishability Obfuscation over GG
Explore cryptanalysis techniques for multilinear maps and indistinguishability obfuscation, focusing on annihilation attacks and their implications for cryptographic security.
Another View of the Division Property
Explore an alternative perspective on the division property in cryptography, examining its implications and applications in modern encryption techniques.
Automatic Search of Meet in the Middle and Impossible Differential Attacks
Explore automated techniques for identifying meet-in-the-middle and impossible differential vulnerabilities in cryptographic systems, enhancing security analysis efficiency.
Backdoors in Pseudorandom Number Generators - Possibility and Impossibility Results
Explore pseudorandom number generators, their security, and potential backdoors. Learn about PRG construction, robustness, and optimization techniques for secure random number generation.
Big Key Symmetric Encryption - Resisting Key Exfiltration
Explore innovative techniques for symmetric encryption that resist key exfiltration, enhancing data security and protection against unauthorized access.
Bounded Indistinguishability and the Complexity of Recovering Secrets
Explore cryptographic concepts of bounded indistinguishability and secret recovery complexity, delving into advanced theoretical aspects of information security and computational theory.
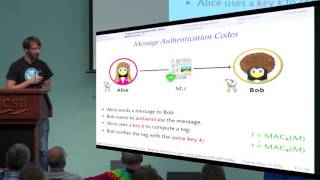
Breaking Symmetric Cryptosystems Using Quantum Period Finding
Explore quantum period finding's impact on symmetric cryptosystems, uncovering vulnerabilities and potential breakthroughs in cryptography.
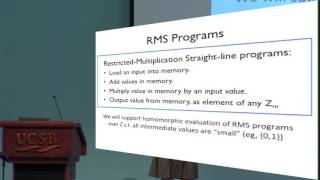
Breaking the Circuit Size Barrier for Secure Computation Under DDH
Explore secure computation techniques breaking circuit size barriers, including homomorphic encryption and secret sharing, with applications in branching programs and two-party computation.
Counter in Tweak Authenticated Encryption Modes for Tweakable Block Ciphers
Explore authenticated encryption modes for tweakable block ciphers, focusing on Counter in Tweak techniques and their applications in cryptography.
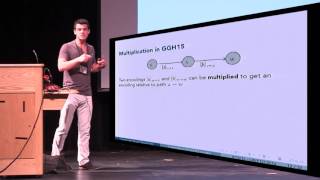
Cryptanalysis of GGH15 Multilinear Maps
Explore cryptanalysis techniques for GGH15 multilinear maps, examining vulnerabilities and potential attacks on this cryptographic primitive. Gain insights into advanced cryptographic analysis methods.