Thinking Outside the Sandbox - Violating Trust Boundaries in Uncommon Ways
Explore uncommon techniques for bypassing browser sandboxes, focusing on four successful Pwn2Own contest entries. Learn about innovative attack vectors and their implications for application security.
Injection Flaws - Stop Validating Your Input
Explore injection flaws and learn why input validation alone is insufficient for security. Discover effective strategies to protect against these vulnerabilities in web applications.
With BIGDATA Comes BIG Responsibility - Practical Exploiting of MDX Injections
Explore OLAP technology vulnerabilities in Business Intelligence systems, focusing on MDX-related attacks, code injection, and data retrieval vectors. Learn practical exploitation techniques for critical corporate data.
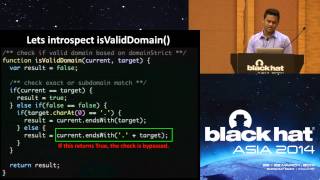
JS Suicide - Using JavaScript Security Features to Kill JS Security
Explore JavaScript security features and their potential vulnerabilities, uncovering how these protective measures can be exploited to compromise web application security.
Web Application Security
Explore web application security fundamentals, vulnerabilities, and best practices with industry experts Dennis Groves and Bill Pennington in this comprehensive conference talk.
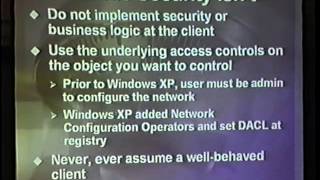
Writing Secure and Hack Resistant Code
Learn techniques for developing secure and hack-resistant code in Windows 2003, focusing on best practices to protect against common vulnerabilities and enhance overall system security.
Java Decompilation & Application Security
Explore Java decompilation techniques and their impact on application security, uncovering potential vulnerabilities and best practices for secure coding.
Injectso - Modifying and Spying on Running Processes Under Linux
Explore advanced techniques for modifying and monitoring active Linux processes, focusing on injection methods and real-time surveillance strategies.
.NET from the Hacker's Perspective - Part 2
Explore advanced .NET security vulnerabilities and exploitation techniques, focusing on real-world attack scenarios and defensive strategies for developers and security professionals.
Think Like a Hacker
Explore hacker mindsets and strategies to enhance system security. Learn practical steps for protecting data, improving authentication, and addressing vulnerabilities in your organization's digital infrastructure.

Discovering Risks in Systems Design - Chaos Engineering in Application & Cloud Security
Explore chaos engineering in application and cloud security, covering emerging patterns, tools, and practical exercises to enhance system resilience and strengthen DevSecOps culture.
The State of Application Security 2023 - Learnings from 4 Million Scanned Services - Unveiling the Power of Proactive Cybersecurity Investments
Unveiling key vulnerabilities from a global scan of 4 million web services, this talk explores prevalent cyber risks, offering insights on file leaks, DNS vulnerabilities, and cross-site scripting with real-world examples and demos.
Low-Level RASP - Protecting Applications Implemented in High-Level Programming Languages
Explore low-level RASP for enhanced application security across multiple high-level programming languages, offering improved defense capabilities compared to traditional WAF and HIPS solutions.
Unlocking Any Door in 21st Century - Immersion in Bio-Security
Explore biometric authentication vulnerabilities, AI/ML risks, and creative hacking techniques. Learn about data privacy threats and strategies to bypass liveness checks in modern security systems.
Precision Munitions for Denial of Service
Explore targeted DoS attacks using precision-crafted requests to cripple services while evading WAF countermeasures. Learn about an overlooked CVSS 7.5 vulnerability as a potent cyber weapon.
Software Security
Insightful discussion on the evolving role of security in software development, emphasizing the shift towards developer responsibility and strategies for making informed security decisions.
What is Linux Kernel Keystore and Why You Should Use It in Your Next Application
Explore Linux kernel keystore's secure credential management, integration with hardware security modules, and benefits for application development in cloud-native environments.
Playing Video Games One Frame at a Time
Explore how programmers can create tools to assist in playing video games, including code injection and system interactions, with examples in C++.
Concurrency Abstractions for Application Security
Explore how concurrency abstractions in Erlang's virtual machine can enhance application security, comparing benefits with statically typed languages and discussing challenges in modern networked applications.
The High Risk of Low Risk Applications
Explore the hidden dangers of seemingly low-risk applications and learn strategies to mitigate potential security threats in this insightful cybersecurity presentation.
Code Insecurity or Code in Security - Mano Paul
Explore code security vulnerabilities and defense strategies, covering non-repudiation, error handling, cryptography, unsafe functions, and privilege management in software development.