The 13 Best Golang Security Tips You'll Ever Hear
Practical advice and best practices for building secure applications in Go, covering essential security tips for developers working with Golang.

PHP WAF - Intercept and Monitor Application Attacks
Explore integrating WAF capabilities into PHP applications for enhanced security. Learn to intercept attacks, monitor user activity, and implement a skeleton security framework.
The Illusion of Control - Secrets Within Your Software Supply Chain
Uncover hidden risks in software supply chains. Learn how leading organizations boost productivity, reduce security debt, and accelerate innovation through improved visibility and control of component consumption.
Doing AppSec at Scale - DevOps + Agile + CI/CD == AppSec Pipelines
Scaling AppSec through DevOps, Agile, and CI/CD practices. Learn strategies to efficiently manage application security across large organizations using automation, orchestration, and ChatOps.
How to Influence a Developer to Write Secure Code in 10 Minutes
Discover effective strategies to quickly motivate developers to prioritize secure coding practices, enhancing overall software security in just 10 minutes.
You're Not Done Yet - Turning Securable Apps into Secure Installations using SCAP
Learn to transform securable applications into secure installations using SCAP. Explore techniques for enhancing cybersecurity and ensuring robust system configurations.
Why Do Developers Make Dangerous Software Errors
Explore why developers create risky software, the importance of secure coding practices, and strategies for implementing effective software assurance in modern technology development.
AppSec Inception - Exploiting Software Culture
Explore software security culture and its exploitation with insights from Aspect Security's CEO Jeff Williams in this thought-provoking talk on application security challenges.
How NOT to Implement Cryptography for the OWASP Top 10 Reloaded
Learn common cryptography implementation mistakes and best practices for securing applications against OWASP Top 10 vulnerabilities with expert Anthony J Stieber.
Application Security & User Experience
Explore the intersection of application security and user experience, focusing on balancing robust protection with seamless interactions in software design.
Six Key Metrics - A Look at the Future of AppSec
Explore six crucial metrics shaping the future of application security. Gain insights into emerging trends and strategies for enhancing your organization's AppSec practices.
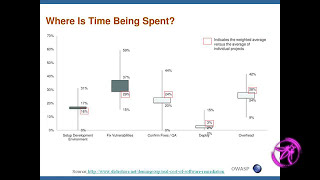
Application Security Debt and Application Interest Rates
Explore application security debt and interest rates with Chris Wysopal from Veracode. Learn strategies to manage and mitigate security risks in software development.
Security from Inception
Explore strategies for integrating security into application projects, focusing on trade-offs, priorities, and communication between developers and security teams.
Start Writing Security Tests Now
Learn methodologies and frameworks for automating security testing in your applications, enabling developers to address common vulnerabilities and collaborate more effectively with pentesters.
How to Secure Your Spring Apps with Keycloak
Comprehensive guide to integrating Keycloak for robust authentication in Spring applications, covering core concepts, OAuth/OpenID Connect flows, and centralized identity management.
Spring Security for N00bz - A Quick Introduction for the Terminally Insecure
Comprehensive introduction to Spring Security, covering defense-in-depth strategies and live coding demonstrations for securing applications using open-source tools.
A Top 10 List for Better AppSec - Hint - It's Not the OWASP Top Ten
Explore key AppSec strategies beyond OWASP Top 10, focusing on proactive controls and practical cheat sheets for enhanced application security implementation.
Kick Starting an Application Security Program
Learn strategies to initiate and develop an effective application security program, focusing on key elements and best practices for implementation.
Realizing Software Security Maturity - The Growing Pains and Gains
Explore software security maturity stages, from low to high, and learn strategies for building effective application security programs with practical insights and metrics.
Practical Tips for Defending Web Applications in the Age of DevOps
Practical tips for adapting application security to modern DevOps practices, covering static analysis, dynamic scanning, and security visibility for rapid development cycles.
Reflections on Trusting TrustZone
Explore TrustZone security, vulnerabilities, and exploitation techniques in ARM devices. Gain insights into real-world implications and see a live demonstration of bootloader unlocking.