Leveraging AI in Cybersecurity - Fighting Fire with Fire
Explore AI-driven strategies to fortify cloud workloads against evolving cyber threats, from development to runtime, ensuring comprehensive protection throughout the lifecycle.
Securing Kubernetes: Best Strategies for the Modern Era - Conf42 IM 2024
Explore best practices for securing Kubernetes clusters, covering control plane, node-level, application, and network security strategies. Gain insights into real-world incidents and essential tools for robust K8s protection.
Supply Chain Security: From Infrastructure to Application, Code to Cloud
Explore best practices for securing the entire software supply chain, from infrastructure to application, covering code, cloud, dependencies, and deployment.
DARCC - The 5 Layers of Modern App Security
Explore the DARCC layers of modern app security: Dependency, Access-Control, Runtime, Configuration, and Container. Learn best practices for securing your software supply chain and enforcing policies.
Runtime Security in the Cloud Native World
Explore runtime security in cloud-native environments, focusing on detecting and mitigating security breaches in production. Learn about essential tools and strategies for maintaining robust security measures.
How to Achieve Comprehensive Protection for Cloud Native Applications and Workloads
Learn comprehensive protection strategies for cloud-native applications, covering web security, runtime risks, and predictive models. Explore practical solutions and benefits through demos and real-world examples.
Security in the Cloud with Falco - Overview and Project Updates
Discover Falco, the Cloud-Native Runtime Security project for Kubernetes threat detection. Learn about recent developments, upcoming roadmap, and new features like ARM support, eBPF probe, and Cloud Security use cases.
Hypervisor-Based Integrity: Protecting Guest Kernels in Cloud Environments
Explore hypervisor-based integrity protection for guest kernels in cloud environments, focusing on threat models, runtime protection, and implementation challenges.
JavaScript Realms - The Blank Spot in Web Application Runtime Security
Explore JavaScript Realms and their impact on web application runtime security, uncovering potential vulnerabilities and mitigation strategies.
Security and Correctness in Wasmtime
Explore security measures in Wasmtime WebAssembly runtime, focusing on sandboxing, isolation, and implementation correctness to ensure safe execution of untrusted programs.
Sandboxing Your Sandbox: Leveraging Hypervisors for WebAssembly Security
Explore advanced techniques for securing Wasm applications using hypervisor-based sandboxing. Learn to address security challenges in multi-tenant environments and leverage hardware virtualization for robust application isolation.
Sandboxing Wasm Programs - Syscall Isolation Techniques for Edge Computing
Explore Wasm runtime sandboxing techniques, including SELinux, cgroups, and seccomp. Learn about Callander, a novel syscall sandboxing tool, to enhance security in edge computing platforms.
Bypassing Falco - How to Compromise a Cluster without Tripping the SOC
Explore techniques to bypass Falco's default ruleset, enabling stealthy cluster compromise. Learn 9 bypass classes for target enumeration, privilege escalation, and lateral movement without alerting security teams.
Extend Falco with Plugins - Trigger Alerts with Any Stream of Events
Learn to extend Falco's capabilities with plugins, enabling custom event streams and alerts. Explore architecture, plugin types, SDK usage, and real-world applications for enhanced cloud-native security monitoring.
PolicyReport CRD - Managing Admission Control, Runtime, and Scan Reports
Explore PolicyReport CRD for standardized Kubernetes policy management. Learn about adapters for various engines and discover Policy Reporter's integration capabilities.
Keep Calm and Containerd On - Migrating Kubernetes Clusters from Docker to Containerd
Explore Intuit's journey migrating 200+ Kubernetes clusters to containerd, addressing challenges in logging, SELinux, GPU support, and cluster addons. Learn valuable lessons for a smooth transition.
A Treasure Map of Hacking and Defending Kubernetes
Comprehensive guide to Kubernetes security: threat modeling, attack demonstrations, defense strategies, and advanced topics like workload identity and runtime hardening for robust cluster protection.
Falco to Pluginfinity and Beyond - Cloud-Native Runtime Security
Explore Falco's evolution as a cloud-native runtime security project, including its new plugin system for enhanced cloud security and threat detection in Kubernetes environments.
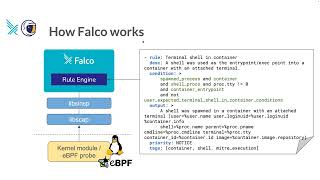
gVisor and Falco - Strengthening Kubernetes and Container Security with Visibility
Explore container sandboxing with gVisor and enhance security monitoring using Falco, improving Kubernetes protection without compromising visibility.
Foster Secure Innovation with Your Kubernetes Platform
Explore comprehensive security strategies for Kubernetes, covering infrastructure protection, supply chain security, and runtime safeguards in mission-critical cloud-native environments.
Using Falco and eBPF to Protect Your Applications
Explore Falco and eBPF for application protection. Learn about runtime security, syscalls, and Falco's architecture. Discover how to implement, connect, and contribute to this powerful security tool.