Proactive Application Security - Karthik Rangarajan
Explore proactive application security strategies, including bug fixing, developer collaboration, code review, centralized logging, and automated access control for enhanced software protection.
Common Sense Security Framework
Common sense approach to security framework implementation, focusing on simplicity and tailored solutions for businesses of all sizes. Covers key areas like applications, endpoints, networks, servers, data, and physical locations.
Developers Guide to Pen Testing - Hack Thyself First
Learn essential penetration testing techniques for developers to identify and address security vulnerabilities in your own applications, enhancing overall system protection.
The Benefits in Externalizing DMZ as a Service in the Cloud
Explore the benefits of cloud-based DMZ services, covering web architecture, security measures, and application firewalls. Learn about attack types and secure development practices.
Secure Test Driven Development - Brakeman - Gauntlet - OWASP and the Work Still to Be Done
Explore secure test-driven development using Brakeman and Gauntlet, discussing OWASP principles and future challenges in software security.
OSINT for AppSec Recon ng and Beyond - Tim Tomes
Explore OSINT techniques for AppSec reconnaissance using Recon-ng, covering data extraction, vulnerability scanning, and leveraging online resources for effective security assessments.
Bumper Massage - Punch and Counter Punch Part Deux - Web Applications
A short, under 1-hour program featuring videos from GrrCON 2015, focusing on web applications.
Building an Application Security Program
Strategies for establishing and expanding an effective application security program, including policy development, metrics, and alignment with software development lifecycle.
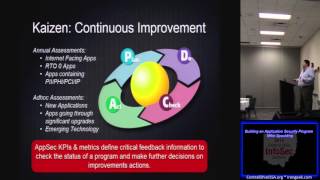
Building an Application Security Program
Aprenda a construir um programa de segurança de aplicações eficaz, abordando análise estática e dinâmica, verificação manual e melhoria contínua para reduzir riscos e alinhar-se ao ciclo de desenvolvimento.
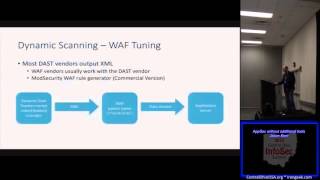
AppSec Without Additional Tools
Learn application security integration techniques, from requirements to operations, without additional tools. Explore best practices, dynamic and static scanning, and continuous integration for successful AppSec implementation.
The Node JS Highway Attacks Are at Full Throttle
Explore Node.js vulnerabilities and attack vectors, focusing on security challenges in the rapidly evolving JavaScript ecosystem and strategies for mitigation.
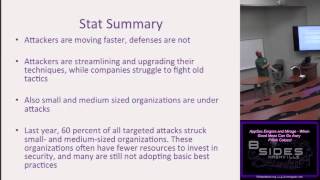
AppSec Enigma and Mirage - When Good Ideas Can Go Awry
Explore AppSec challenges, data breaches, and best practices. Learn from real-world examples and industry insights to enhance your application security knowledge and strategies.
Its Just a Flesh Wound
Learn about common application security vulnerabilities and best practices for prevention in this informative talk. Explore topics like credential protection, session management, and information leakage.
Evolving Your Office's Security Culture by Selective Breeding of Ideas and Practices
Evolve your office's security culture through selective breeding of ideas and practices. Learn strategies for improving awareness, implementing policies, and measuring effectiveness.
Process Ventriloquism
Explore process manipulation techniques for Windows, including API methods, library injection, hooking, and memory scraping. Learn to inject Python interpreters for advanced control.
Building Our Workforce
Strategies for building and nurturing a skilled cybersecurity workforce, focusing on recruitment, training, mentorship, and professional development in the information security field.
Recharging Penetration Testing to Maximize Value
Strategies to enhance penetration testing effectiveness, including improved scoping, collaboration, and reporting techniques for maximizing value and impact in information security.
Reality Checking Your AppSec Program
Explore strategies to critically assess and improve your AppSec program, focusing on compliance, maturity, education, and validation beyond traditional metrics and assumptions.
How to Implement Crypto Poorly
Explore common pitfalls in implementing cryptography, focusing on single sign-on systems and best practices for secure authentication in web applications.
What's in Your Top Ten - Intelligent Application Security Prioritization
Explore pragmatic threat modeling approaches for application security, focusing on architecture-driven methodologies and their integration into the software development lifecycle.
The Upside Down - Going from NetSec to AppSec
Explore the transition from network security to application security, covering challenges, pipeline analysis, and solutions for effective cybersecurity practices.