Mastering OSS Security Development with Linux Foundation Education
Develop secure open source software skills, from foundational to advanced, with expert-led training and certifications. Gain hands-on experience for real-world OSS security.
How to Hack OWASP Juice Shop - A Guided Walkthrough Showing All Solutions
Comprehensive guide to mastering OWASP Juice Shop's vulnerabilities, covering all challenges from basic to advanced levels with detailed solutions and explanations.
Stack Overflow: A Story of Two Security Tales - Enhancing Software Security
Exploring Stack Overflow's dual impact on software security: potential vulnerabilities and effective solutions. Highlights research findings and proposes design tweaks to enhance secure development practices.
Security Code Analysis is for Everyone - 2019
Learn proactive approaches to identify and fix software vulnerabilities using Security Code Analysis, addressing complex applications and diverse development environments.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
Vulnerable by Design - The Backdoor That Came Through the Front
Explore vulnerabilities in software design, historical backdoors, and their implications for security. Learn about notable cases and techniques for creating and detecting backdoors.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.
AppSec Challenges - Overcoming Framework Limitations and Building Robust Security
Exploring challenges in application security, analyzing framework limitations, and discussing robust approaches to improve security at scale while making it more manageable.
Eradicating Vulnerability Classes: Embracing Secure Defaults and Invariants
Explore innovative approaches to application security, focusing on secure defaults and invariants instead of traditional SAST methods to effectively eliminate vulnerability classes.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
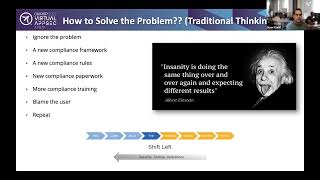
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
Security as Code: A DevSecOps Approach
Explore DevSecOps principles and practices for integrating security into the software development lifecycle, emphasizing automation and collaboration for robust application security.
OWASP WrongSecrets - We Have a Secret for Everyone
Explore common pitfalls in secret management and learn best practices for securing sensitive information in various environments, from local setups to cloud deployments.
OWASP Security Knowledge Framework - Project Overview and Best Practices
Explore OWASP Security Knowledge Framework with project lead Glenn Ten Cate, discussing goals, milestones, and best coding practices for this essential security tool.
Bringing Security Testing to Development: Enabling Developers as Security Experts
Discover strategies for integrating security testing into development processes, empowering developers to become security experts and enhance application safety.
Implementing a Supply Chain Approach to Build and Deploy Secure Applications - AppSecEU 2016
Explore implementing a supply chain approach to build and deploy secure software, focusing on trust, standardization, and automation in the software delivery pipeline.
Developing Secure Open Source Software - Mentorship Session
Explore best practices for developing secure open source software with expert guidance on risk mitigation, vulnerability management, and collaborative security measures.

Security Champions: Introducing Them in Your Organization
Discover how to implement Security Champions in your organization, enhancing developer readiness for security challenges and secure coding practices. Learn about supporting OWASP tools and guidance.
Find and Fix Software Security Problems - Preventing Security Mistakes
Explore effective strategies for identifying, fixing, and preventing software security issues. Learn how to prioritize and address vulnerabilities to enhance overall system security.
Ending Injection Vulnerabilities
Learn how programming languages can prevent injection vulnerabilities by distinguishing trusted developer strings from potentially attacker-controlled input, ensuring safer handling of user values in sensitive contexts.
Securing the Future: Challenges and Innovations in Application Security
Insightful keynote address exploring cutting-edge application security trends, challenges, and best practices in the rapidly evolving digital landscape.