Don't Worry, Be API - Addressing AppSec's Modern Challenge
Explore modern API security challenges and solutions, including OWASP API Security Top 10, authentication issues, and authorization vulnerabilities in this comprehensive overview.
How to Review Code for Vulnerabilities - OWASP Standard Classification
Learn effective strategies for identifying vulnerabilities through source code review, including key concepts, starting points, and automation techniques. Practice reviewing code samples to enhance your application security skills.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
OWASP Serverless Top 10 - Understanding Security Risks in Serverless Applications
Explore the top 10 security risks in serverless architectures, understanding vulnerabilities and best practices for securing cloud-native applications.
Automated Security Testing With OWASP Nettacker
Learn automated security testing techniques using OWASP Nettacker, a powerful open-source tool for vulnerability assessment and information gathering in web applications and networks.
Flipping the Script on Application Security
Explore innovative approaches to application security, challenging traditional methods and introducing fresh perspectives for more effective protection strategies.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
Worrisome Web Vulnerability Trends in the Race to Innovation
Explore concerning web vulnerability trends amid rapid innovation, examining their impact on security and discussing strategies for mitigation and protection.
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
Security as Code: A DevSecOps Approach
Explore DevSecOps principles and practices for integrating security into the software development lifecycle, emphasizing automation and collaboration for robust application security.
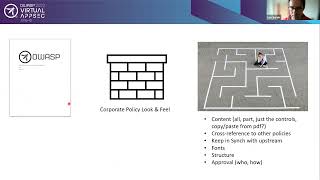
Making ASVS Truly Your Own
Explore strategies to customize and implement OWASP's Application Security Verification Standard (ASVS) effectively within your organization's unique security framework.
Preventing Subdomain Takeover with OWASP Domain Protect
Learn to prevent subdomain takeovers using OWASP Domain Protect. Enhance your application security knowledge with practical strategies and tools.
Philosophizing Security in a Mobile-First World
Explore security challenges and strategies in a mobile-centric world, examining philosophical approaches to safeguarding applications and data in the era of ubiquitous mobile devices.
OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Supply Chain Security with Dependency Track
Explore supply chain security using Dependency Track with experts Anandan, Bhargava, and Duster. Learn strategies to mitigate risks and enhance software security in this informative session.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
Reducing Permissions Management Time While Protecting Users
Learn strategies to streamline permissions management, enhance user protection, and optimize security processes in application development.