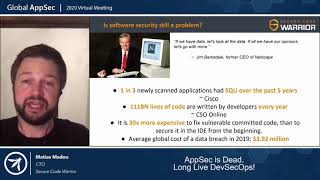
AppSec is Dead - Long Live DevSecOps
Explore the shift from AppSec to DevSecOps, focusing on creating secure code, working smarter, and implementing key pillars for effective security integration in software development.
OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
OWASP NL Chapter Meeting - SKF News
Learn about the latest developments in OWASP's Security Knowledge Framework (SKF) from experts Riccardo and Glenn ten Cate, enhancing your understanding of web application security best practices.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Understanding the API Attack Vector - How Attackers Exploit Application Communications
Explore attacker techniques for targeting API-driven applications, including code manipulation, mobile vulnerabilities, and advanced attacks. Learn strategies to secure apps in cloud-native environments.
Normalizing AppSec Issues for Contextual Risk-Based Prioritization at Enterprise Scale
Explore a new approach to Application Security that focuses on critical risks by incorporating contextual intelligence, improving efficiency and delivery in enterprise-scale programs.
Changed Responsibilities in Modern Development Practices
Explore how modern development practices like CI/CD and DevOps impact application security. Learn strategies for integrating security early in the development lifecycle and empowering developers with essential security skills.
Analyzing Google's SLSA Framework for Securing Software Supply Chains
Explore Google's SLSA framework for securing software supply chains, covering key areas, controls, and additional considerations beyond the framework's scope.
OWASP Software Assurance Maturity Model - SAMM
Explore OWASP's Software Assurance Maturity Model (SAMM), a framework for improving software security practices across organizations, presented by expert Bart De Win.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
Connecting the Dots: How Threat Intelligence Protects Applications
Explore Cyber Threat Intelligence integration in AppSec programs, automating data collection, and leveraging IoCs and TTPs to prevent and mitigate cyber attacks in today's digital business landscape.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Security Culture - Fostering Hackers for Application Security
Explore strategies to foster a security-focused culture among IT professionals, emphasizing knowledge sharing, communication, and developer engagement to enhance application security and overall cybersecurity awareness.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
Learn to Exploit TOCTOU Race Condition Vulnerabilities with OWASP TimeGap Theory
Explore TOCTOU race condition vulnerabilities and learn exploitation techniques using OWASP TimeGap Theory in this comprehensive cybersecurity session.