Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.
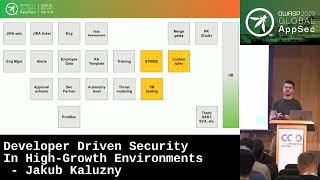
Developer Driven Security in High-Growth Environments
Explore strategies for implementing developer-driven security practices in rapidly expanding tech environments, focusing on scalable and efficient approaches.
How to Have Visibility and Security of a CI/CD Pipeline
Discover strategies for enhancing visibility and security in CI/CD pipelines, focusing on best practices and tools to safeguard your software development lifecycle.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
OWASP WrongSecrets - We Have a Secret for Everyone
Explore common pitfalls in secret management and learn best practices for securing sensitive information in various environments, from local setups to cloud deployments.
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
OWASP Dependency Check Project
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP's powerful open-source tool, enhancing your application's security and reducing potential risks.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
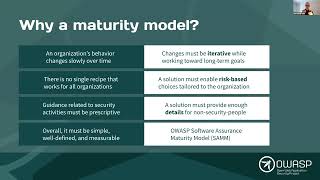
OWASP SAMM Project - Introduction to Software Assurance Maturity Model
Explore the OWASP SAMM framework for software assurance, learning key strategies to integrate security practices throughout the software development lifecycle.
OWASP Open Application Security Curriculum Project
Learn essential application security concepts and practices from OWASP's comprehensive curriculum, designed to enhance your skills in identifying and mitigating software vulnerabilities.
OWASP DefectDojo Project
Explore DefectDojo, an open-source vulnerability management tool. Learn its features, implementation, and how it streamlines security testing workflows for development teams.
Common Application Security Mistakes Enabling Automated Attacks
Explore common security flaws enabling automated attacks on applications, including retail fraud and account takeovers. Learn from real-world examples and discover effective prevention strategies.
How Security, Development, and Testing Can Work Together to Stop Recurring Vulnerabilities - OWASP Top 10
Explore strategies for integrating security, development, and testing to prevent recurring vulnerabilities in the OWASP Top 10, fostering collaboration and cultural change for secure software development.
Building Diversity into Application Security
Explore strategies for fostering diversity in application security with insights from industry experts on inclusive practices and overcoming barriers.
Post-DevOps: What Should We Shift-Left in Application Security?
Exploring post-DevOps challenges in AppSec, focusing on risk profiles, threat response architecture, and operational aspects to enhance security and quality in fast-paced development environments.
Scaling AppSec through Education
Strategies for scaling application security through developer education, addressing the imbalance between security teams and developers and emphasizing code review for early bug detection.
AppSec Champions Programs - Best Practices and Survey Results
Explore AppSec champions programs: research findings, best practices, and strategies for influencing developers to write secure code. Learn to implement and improve these programs in your organization.
Top Ten Proactive Controls for Secure Software Development
Explore essential software security controls for developers, covering authentication, access control, validation, and more. Learn proactive strategies to build robust, secure applications.
2013 AppSec Guide and CISO Survey - Making OWASP Visible to CISOs
Insights from OWASP's 2013 AppSec Guide and CISO Survey, focusing on application security governance, risk management, and investment strategies for Chief Information Security Officers.