Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
Abusing Windows Filtering Platform for Privilege Escalation - Undetected Attack Techniques
Discover an innovative Windows privilege escalation technique that exploits the Windows Filtering Platform, enabling stealthy system-level access through network traffic manipulation and kernel component abuse.
NTLM Authentication Vulnerabilities and Exploits - A Final Analysis
Dive into critical NTLM authentication vulnerabilities, exploring new bugs, bypass techniques, and security control gaps in Windows systems before Microsoft phases out this protocol.
HookChain: A New Perspective for Bypassing EDR Solutions
Discover a sophisticated EDR bypass technique combining IAT Hooking, dynamic SSN resolution, and indirect system calls to redirect Windows subsystem execution flow while remaining undetected by traditional security measures.
DriverJack: Turning NTFS and Emulated ROFs into an Infection
Discover advanced exploitation techniques targeting NTFS and emulated filesystem vulnerabilities, exploring novel attack vectors that bypass Windows security measures and maintain system persistence.
Defeating ATM Disk Encryption - Security Vulnerabilities in Vynamic Security Suite
Delve into critical ATM security vulnerabilities, focusing on Diebold Nixdorf's VSS encryption weaknesses, exploitation methods, and essential defense strategies for financial systems protection.
Windows Downdate: Downgrade Attacks Using Windows Updates
Discover how to exploit Windows Update vulnerabilities to craft downgrade attacks, bypass security features, and compromise system integrity - from kernel to virtualization stack.
Revealing the Antivirus Quarantined: Using PowerShell to Enable Analysis
Explore PowerShell techniques to analyze antivirus-quarantined files, enhancing your ability to investigate and understand potential security threats.
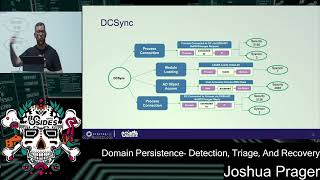
Domain Persistence - Detection, Triage, and Recovery
Explore Active Directory domain persistence techniques, focusing on detection, triage, and recovery strategies. Learn to identify attacks, reclaim control, and enhance Windows Security event auditing.
Decrypting the Directory - A Journey into Static Analysis of Active Directory NTDS
Explore static analysis techniques for Active Directory NTDS, uncovering security insights and potential vulnerabilities in this in-depth conference talk on IT security and network infrastructure.
10 Years of Windows Privilege Escalation with Potatoes
Explore a decade of Windows privilege escalation techniques using "Potatoes" in this IT security talk, covering key developments and implications for system administrators and security professionals.
The Registry Rundown - Windows Security Analysis
Explore Windows Registry intricacies, security implications, and forensic analysis techniques in this IT security conference talk by Van Bockhaven and Grim.
Windows EventLog Persistence Techniques for Red Team Operations
Explore Windows environment exploitation techniques, including bypassing constrained language, XML file abuse, and EventLog persistence, with a focus on red team operations and defense strategies.
DPAPI and DPAPI-NG - Decrypting All Users' Secrets and PFX Passwords
Explore groundbreaking DPAPI research, uncovering critical vulnerabilities in data protection. Learn about key discoveries, their implications, and gain hands-on experience with provided tools.
Deep Dive into Windows Defender - Smart App Control and ETW
Explore Windows Defender's Smart App Control and ETW features in this technical deep dive, uncovering advanced security mechanisms and their implications for IT professionals.
Windows 11 Security and Resiliency - OD811
Discover essential Windows 11 security features, deployment practices, and tools to protect your organization against modern cyberthreats while maintaining operational resilience.
On the Effectiveness of Control-Flow Integrity in Practice - A Systematic Overview
Explore the real-world effectiveness of Control-Flow Integrity protection across Android and Windows systems, revealing critical gaps between research advances and actual deployment in practice.