
Stable 26 RID Hijacking - Maintaining Access on Windows Machines
Explore RID hijacking techniques for maintaining persistent access on Windows systems, focusing on advanced methods and countermeasures.
Stable 25 SharPersist Windows Persistence Toolkit in C
Explore a Windows persistence toolkit in C# for maintaining access to compromised systems, featuring techniques and strategies for covert operations.
PPLdump Is Dead - Long Live PPLdump
Explore Windows Protected Process Light (PPL) mechanism, its vulnerabilities, and historical exploits. Learn about PPLdump, its impact on system security, and Microsoft's approach to PPL-related vulnerabilities.
Security in Cloud-Native
Explore cloud-native security approaches, focusing on data protection, infrastructure trustworthiness, and common vulnerabilities. Learn strategies for securing both Linux and Windows deployments in the cloud.
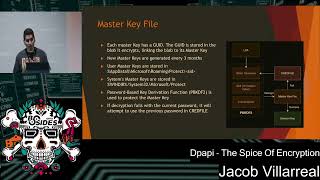
DPAPI - The Spice of Encryption
Explore Windows' Data Protection API, its encryption mechanisms, and exploitation techniques for credential dumping and domain persistence.
Better Bug Bounty Hunting, CTFs and Reverse Engineering - Cybertalk Episode 8
Insights on improving bug bounty skills, starting in pentesting, choosing laptops for security work, and comparing Android vs Windows reverse engineering techniques.
Abusing Mixed Vendor Kerberos Stacks - Exploiting Windows AD and Linux Authentication
Discover security vulnerabilities in mixed Kerberos environments and learn how to exploit weaknesses between Windows Active Directory and Linux/Unix systems for privilege escalation.
Malware and Hunting for Persistence - How Adversaries Exploit Windows
Discover how adversaries exploit Windows systems through malware and persistence techniques, enhancing your cybersecurity defense capabilities and threat detection skills.
CertifiedDCOM - The Privilege Escalation Journey to Domain Admin with DCOM
Uncover a critical DCOM vulnerability allowing remote privilege escalation to Domain Admin in Windows networks. Learn about DCOM internals and exploit techniques for Active Directory takeover.
Outlook Unleashing RCE Chaos: Exploiting CVE-2024-30103
Dive into the critical Outlook security vulnerabilities, exploring remote code execution exploits through COM objects, NTLM leaks, and essential mitigation strategies for enterprise protection.
Protecting Windows Credentials - An Excessive Guide for Security Professionals
Comprehensive guide for security professionals on safeguarding Windows credentials, covering architecture, isolation, exploit mitigation, and containment strategies for enhanced system protection.
Abusing Windows Hello Authentication Without Biometric Data
Delve into Windows Hello's security vulnerabilities and authentication mechanisms, exploring attack vectors and hardware protection bypasses for biometric authentication without physical compromise.
Insecure Remote Operations: Windows Living Off the Land Techniques - Session 8
Dive into Windows remote operations security, exploring protocols, APIs, and admin tools through real-world examples. Learn powerful techniques for both defensive and offensive security operations.
Windows Hello for Business Security Analysis and Authentication Protocol Deep Dive - Lecture 10
Explore Windows Hello for Business authentication internals, security vulnerabilities, and attack vectors in Azure AD environments, focusing on key provisioning and credential management.
Modern Stuxnet-Style Attacks Using Filesystem Vulnerabilities and NTFS Exploits
Explore modern cyber attack techniques inspired by Stuxnet, focusing on filesystem vulnerabilities, NTFS exploits, and advanced persistence methods while learning effective defense strategies.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.
Windows System Monitor (Sysmon) for Incident Investigation and Threat Response
Master Windows System Monitor (Sysmon) for incident investigation, learning to track program execution, registry writes, and DNS queries to effectively trace threat actor activities and enhance system security.
Protect Your Most Sensitive Users with Protected Users Group in Windows Server
Discover how Windows Server's Protected Users Group safeguards sensitive accounts, learn its attack-thwarting capabilities, and implement practical strategies for enhanced security in Active Directory environments.
Driving Your Own Vulnerability: How to Navigate the Road of BYOD Attacks
Explore Windows driver vulnerabilities and BYOD attack prevention through real-world case studies, understanding threat categories and security implications for effective system protection.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.