
IBM - Trusteer Rapport - Does IBM Intentionally Backdoor Machines?
Investigates potential security concerns with IBM/Trusteer Rapport software, examining its code execution speed, system access, and implications for user privacy and system integrity.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
Windows - Building What Matters Most for Your Business
Insider's view of top Windows features for secure hybrid work, including Windows 365, Intune, Defender, Teams, Loop, and Surface, presented by Microsoft's engineering leaders.
Detecting Access Token Manipulation
Demystifying Windows access token manipulation attacks and providing effective detection strategies for defensive practitioners in enterprise environments.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
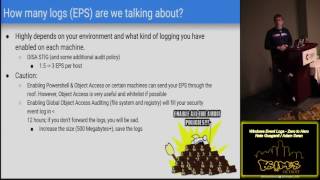
Windows Event Logs - Zero to Hero
Comprehensive guide to leveraging Windows Event Logs for security monitoring, from basic concepts to advanced techniques for threat detection and incident response.
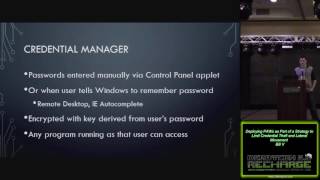
Deploying PAWs as Part of a Strategy to Limit Credential Theft and Lateral Movement
Explore strategies to limit credential theft and lateral movement using Privileged Access Workstations (PAWs), including deployment models, Active Directory setup, and network segmentation.

TeamTNT - Explosive Cryptomining
Explore TeamTNT's cryptojacking tactics targeting Linux servers, including their attack methods, credential theft, and evolution from Docker instances to Windows systems.
Building an Effective Intrusion Detection Program
Learn to build an effective intrusion detection program using affordable tools. Covers cloud apps, endpoints, network security monitoring, and crowdsourced incident response to catch breaches quickly.
ZEROing Trust - Do Zero Trust Approaches Deliver Real Security?
Analyze effectiveness of zero trust security across modern OS platforms, examining measurable properties to establish trust in various threat scenarios.
EBPF ELFs JMPing Through the Windows
Explore eBPF for Windows: capabilities, security model, design, and attack surface. Uncover vulnerabilities, witness fuzzing demos, and discuss exploitation challenges in Windows Protected Process.
Safeguarding Your Business Assets Through Understanding of the Win32API
Explore Win32API vulnerabilities and learn advanced techniques to protect business assets from potential security threats in Windows systems.
DKOM - Direct Kernel Object Manipulation
Explore advanced Windows kernel manipulation techniques, focusing on DKOM for stealthy system modifications and rootkit development.
Addressing Complete Security to Save Money
Explore comprehensive Windows security strategies to reduce costs and enhance protection in this insightful presentation on addressing vulnerabilities and implementing effective safeguards.
How Do I Detect Technique X in Windows - Applied Methodology to Definitively Answer This Question
Learn a systematic approach to detect specific techniques in Windows, enhancing your ability to identify and analyze potential security threats and vulnerabilities.
Hunting Windows Desktop Window Manager Bugs
Exploring Windows Desktop Window Manager vulnerabilities, focusing on DirectComposition UserSpace. Covers architecture, attack surfaces, and specific CVEs, offering insights into bug hunting techniques and security implications.
Windows Hello from the Other Side
Explore Windows Hello vulnerabilities and attack techniques in this IT security talk, covering biometric authentication weaknesses and potential exploits in Windows systems.
The Power of Coercion Techniques in Windows Environments
Explore coercion techniques in Windows environments, their impact on IT security, and strategies for defense against these powerful attack vectors.
Layers on Layers - Bypassing Security for Fun and Profit V2
Explore kernel vulnerabilities in Windows and their impact on security solutions. Learn how to bypass multiple layers of protection and discuss more robust defensive strategies.
Local Privilege Escalation in 2016
Explore techniques for local privilege escalation on Windows and Unix systems, learning how to elevate user privileges to gain full system access in various scenarios.
Suborner - Windows Bribery for Invisible Persistence
Discover a stealthy Windows persistence technique that creates invisible machine accounts, evades detection, and impersonates existing users. Learn about the Suborner Attack's implementation and effectiveness.