OWASP Flagship Projects - OWASP ModSecurity Core Rule Set
Explore OWASP ModSecurity Core Rule Set: web application firewall rules, paranoia levels, and project developments for enhanced security and threat protection.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.
AutoSpear - Towards Automatically Bypassing and Inspecting Web Application Firewalls
Explore techniques for automatically bypassing and inspecting web application firewalls, examining vulnerabilities in WAF-as-a-service solutions and cloud security services.
WAF Bypass In Depth
Explore advanced techniques for bypassing Web Application Firewalls (WAFs) and demonstrating the impact of cross-site scripting vulnerabilities, even in the presence of sophisticated security measures.
Web Application Firewalls - Analysis of Detection Logic
Explores detection logic in Web Application Firewalls, focusing on regular expressions. Analyzes security flaws in popular WAFs and introduces tools for identifying vulnerabilities in regex patterns.
Rock 'Em Sock 'Em Robots - Bot Swatting Like the Pros
Explore strategies for managing bot traffic, detecting malicious behavior, and improving data confidence in web systems. Learn to differentiate between beneficial and harmful bots.
Instrument Flight Rules - Navigating Cyber Security in a Cloud Landscape
Explore modern cybersecurity challenges in cloud environments, learn strategies for data protection beyond traditional perimeters, and discover tools designed for cloud security in this insightful presentation.

PHP WAF - Intercept and Monitor Application Attacks
Explore integrating WAF capabilities into PHP applications for enhanced security. Learn to intercept attacks, monitor user activity, and implement a skeleton security framework.
The Self Healing Cloud - Protecting Applications and Infrastructure with Automated Virtual Patching
Explore automated virtual patching for cloud security, protecting apps and infrastructure through innovative techniques like web application firewalls and network intrusion detection.
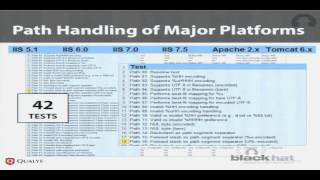
Confessions of a WAF Developer - Protocol-Level Evasion of Web App Firewalls
Explores protocol-level evasion techniques for bypassing web application firewalls, focusing on vulnerabilities in virtual patches and demonstrating real-world examples and countermeasures.
ModSecurity as Universal Cross-Platform Web Protection Tool
Explore ModSecurity's evolution into a cross-platform WAF, its early attack detection capabilities, and its use of OWASP Core Rule Set for protecting Apache, IIS, and nginx servers.
New Optimization and Obfuscation Techniques
Advanced SQL injection techniques for bypassing firewalls and intrusion detection systems, including optimization methods and the Leapfrog framework for testing security measures.
The State of Application Security 2023 - Learnings from 4 Million Scanned Services - Unveiling the Power of Proactive Cybersecurity Investments
Unveiling key vulnerabilities from a global scan of 4 million web services, this talk explores prevalent cyber risks, offering insights on file leaks, DNS vulnerabilities, and cross-site scripting with real-world examples and demos.
The Benefits in Externalizing DMZ as a Service in the Cloud
Explore the benefits of cloud-based DMZ services, covering web architecture, security measures, and application firewalls. Learn about attack types and secure development practices.
I Got 99 Problems but a WAF Ain't One
Explore web application firewall (WAF) challenges and solutions in this talk by Micah Brown, covering common issues and effective strategies for implementation and management.
From OWASP Top 10 to Secure Applications
Comprehensive overview of OWASP standards and practical security implementations for Spring applications, covering injection, access control, and various protection tools.
Bridging the Gap Between Research and Practice in Intelligently Bypassing WAF
Explore AI-driven techniques for bypassing web application firewalls, addressing practical challenges in payload diversity and difficulty balancing. Learn innovative approaches to enhance cybersecurity defenses.
Key Considerations for Designing Cloud DMZ
Explore key design considerations for cloud DMZ on AWS, comparing traditional and cloud-based approaches. Learn about self-healing architecture, resilience, and leveraging managed services for enhanced security and reduced complexity.
Automation and SecOps Integration in Google Cloud Armor
Enhance security delivery and visibility using Infrastructure as Code automation and SecOps integrations in Google Cloud Armor. Learn to expand policy reach and keep your organization safe.

AWS WAF and Web ACL Tutorial - Step-by-Step Guide
Learn to set up and manage AWS WAF: configure VPC, EC2 instances, load balancers, and create Web ACLs with custom rules for blocking and allowing HTTP requests.
The Art of Bypassing Web Application Firewalls - Live Demos
Explore hands-on techniques for bypassing modern web application firewalls. Learn to customize methods and payloads through practical labs, enhancing your skills in WAF evasion and web security.