Modern WAF Bypass Techniques on Large Attack Surfaces
Explore advanced WAF bypass techniques for large attack surfaces with insights from top security researcher Shubham Shah, focusing on complex vulnerabilities and security automation.
OWASP Coraza Web Application Firewalls Revisited
Explore OWASP Coraza's advanced features for securing web applications, including its architecture, rule language, and integration capabilities with popular web servers and frameworks.
When Not to Use a Web Application Firewall and Its Alternatives - Lecture
Explore when to avoid Web Application Firewalls (WAFs) and learn their limitations. Understand WAF architecture, common web threats, and alternative security approaches for effective application protection.
Mitigating Log4Shell and Similar Vulnerabilities Using Cloud Services
Explore how cloud services mitigate vulnerabilities like Log4Shell by blocking attacks, preventing data exfiltration, protecting sensitive information, and enabling forensic analysis in Java applications.
Reversing Engineering Web Applications for Security - Behavior Analysis and WAF Detection
Explore web application reverse engineering, behavior analysis, and WAF detection techniques. Learn to create effective countermeasures against complex attacks using whitelist protection and traffic analysis.
Building Cloud-Native Security for Apps and APIs with NGINX
Enhance NGINX with robust security features for apps and APIs. Learn practical methods for visibility, real-time protection, and mitigation of OWASP Top10 threats, bots, and data leakage in cloud environments.
Introducing the OWASP ModSecurity Core Rule Set 3.0 - AppSec EU 2017
Explore OWASP ModSecurity Core Rule Set 3.0: installation, key concepts, and handling false positives for effective web application firewall protection against common attacks.
Web Application Honeypot Threat Intelligence - Techniques and Implementation
Explore web application honeypots for threat intelligence, using ModSecurity and OWASP Core Rule Set to capture attacker activity and protect software against emerging threats.
What's New in CRS4 - An Update from the OWASP CRS Project
Explore the latest updates and enhancements in CRS4, the OWASP Core Rule Set project, with insights on improved web application security and threat mitigation strategies.
The Rise and Fall of ModSecurity and the OWASP Core Rule Set
Explore the evolution and impact of ModSecurity and OWASP Core Rule Set in web application security, examining their rise, challenges, and future prospects.
Ingress-Nginx and 2024 Plans - Roadmap and Future Developments
Explore ingress-nginx's 2024 roadmap, including modsecurity, potential LUA replacements, and challenges in decoupling control and data planes. Gain insights into future developments and strategies.
AWS Advanced Networking - Full Course - Part 1
Explore AWS advanced networking concepts, from VPC essentials to SSL/TLS with ACM. Master load balancers, security features, and efficient network architectures for cloud computing.
Web Application Firewall Workshop
Hands-on workshop exploring Web Application Firewall bypass techniques, including encoding, SQL injection, protocol switching, and syntax alternatives. Practical exercises with in-depth explanations for each method.
The Truth about Web Application Firewalls
Explore the realities of Web Application Firewalls with experts Sandro Gauci and Wendel Guglielmetti, uncovering insights and truths about their effectiveness and implementation in cybersecurity.
WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
Comparing WAF and RASP - Why?
Explore the differences and complementary roles of WAF and RASP in application security, understanding their strengths and limitations for comprehensive protection.
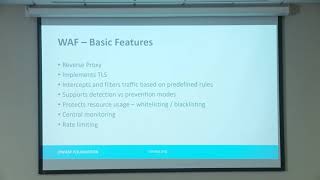
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
Core Rule Set for the Masses
Insights on fine-tuning ModSecurity Core Rule Set for large-scale deployments, reducing false positives, and optimizing web application firewall performance.
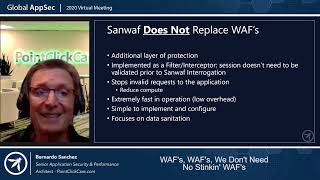
Extending WAFs at the Application Layer
Explore application-level security control with Sanwaf, an alternative to traditional WAFs. Learn its structure, datatypes, and implementation for enhanced web application protection.
Practical OWASP CRS in High Security Settings
Learn to implement OWASP Core Rule Set for high-security web applications, covering WAFs, ModSecurity, logging, whitelisting, and advanced protection techniques.