OWASP ModSecurity: Web Application Firewall Overview
Explore OWASP ModSecurity's features and implementation for enhancing web application security through this concise presentation by Ervin Hegedüs.
Core Rule Set for the Masses: Lessons from Taming ModSecurity Rules at Massive Scale - 2017
Insights on fine-tuning ModSecurity Core Rule Set at scale, reducing false positives, and optimizing web application firewall performance for large-scale deployments.
Getting New Actionable Insights by Analyzing Web Application Firewall Triggers
Explore advanced techniques for analyzing WAF triggers to generate actionable defenses, improve security controls, and gain insights into attacker techniques using real-world case studies.

Nginx ModSecurity Tutorial - Nginx WAF
Learn to secure Nginx with ModSecurity, an open-source web application firewall. Explore real-time request inspection, protection against XSS and SQL injection attacks, and active monitoring for enhanced web server security.

Apache2 ModSecurity Tutorial - Apache2 WAF
Learn to secure Apache2 with ModSecurity, an open-source web application firewall. Explore real-time request inspection, prevention of common attacks, and active monitoring for enhanced web server protection.
Introducing the OWASP ModSecurity Core Rule Set 3.0 - AppSec EU 2017
Explore OWASP ModSecurity Core Rule Set 3.0: installation, key concepts, and handling false positives for effective web application firewall protection against common attacks.
Web Application Honeypot Threat Intelligence - Techniques and Implementation
Explore web application honeypots for threat intelligence, using ModSecurity and OWASP Core Rule Set to capture attacker activity and protect software against emerging threats.
The Rise and Fall of ModSecurity and the OWASP Core Rule Set
Explore the evolution and impact of ModSecurity and OWASP Core Rule Set in web application security, examining their rise, challenges, and future prospects.
Ingress-Nginx and 2024 Plans - Roadmap and Future Developments
Explore ingress-nginx's 2024 roadmap, including modsecurity, potential LUA replacements, and challenges in decoupling control and data planes. Gain insights into future developments and strategies.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
Core Rule Set for the Masses
Insights on fine-tuning ModSecurity Core Rule Set for large-scale deployments, reducing false positives, and optimizing web application firewall performance.
Practical OWASP CRS in High Security Settings
Learn to implement OWASP Core Rule Set for high-security web applications, covering WAFs, ModSecurity, logging, whitelisting, and advanced protection techniques.
OWASP Flagship Projects - OWASP ModSecurity Core Rule Set
Explore OWASP ModSecurity Core Rule Set: web application firewall rules, paranoia levels, and project developments for enhanced security and threat protection.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.
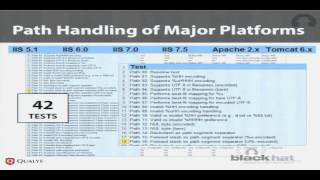
Confessions of a WAF Developer - Protocol-Level Evasion of Web App Firewalls
Explores protocol-level evasion techniques for bypassing web application firewalls, focusing on vulnerabilities in virtual patches and demonstrating real-world examples and countermeasures.
ModSecurity as Universal Cross-Platform Web Protection Tool
Explore ModSecurity's evolution into a cross-platform WAF, its early attack detection capabilities, and its use of OWASP Core Rule Set for protecting Apache, IIS, and nginx servers.