EDR 솔루션 기반 Managed Detection and Response 서비스 소개
Discover how MDR services enhance security threat detection and response through EDR solutions, featuring implementation cases and expert insights for efficient security management.
Elevate Cloud Threat Hunting with AI
Explore AI-powered cloud threat hunting with Kestrel as a Service, enhancing detection speed and efficiency through reusable hunting flows and predictive AI model plugins.
Cyber Security vs. Statistics - Fighting False Positives to Automate Your Security Operations
Strategies for automating security operations by correlating detections and leveraging statistical methods to reduce false positives and enhance incident response effectiveness.
Unlocking Security Investigations with Cribl Search
Master advanced security analytics and threat hunting using Cribl Search's powerful capabilities for cloud data investigation, statistical analysis, and data federation - all without vendor-specific storage requirements.
Threat Hunting Space and Digital Energy with Physics - Session 5
Explore innovative physics-based approaches to threat hunting in ICS/SCADA networks, focusing on IoMT and IoST monitoring techniques for detecting complex adversarial activities.
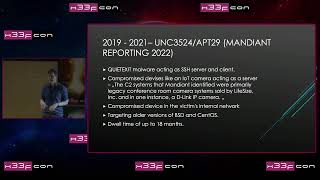
Addressing Tactics Related to Edge Device Compromise - Security Detection and Defense
Explore advanced threat hunting techniques and defense strategies against edge device compromises, focusing on detection methods, forensic analysis, and proactive security measures for network infrastructure.

Busting Red Team Trends with Style - Building a Custom ETW-Based Sysmon Replacement
Dive into advanced threat hunting with a custom ETW-based Sysmon replacement, exploring enhanced telemetry capabilities for detecting sophisticated red team techniques and threat actor fingerprinting.
Cloud Console Cartographer - Mapping Cloud Events for Security Analysis
Discover how to efficiently map and analyze cloud console activities with an open-source framework that simplifies the complex task of correlating hundreds of CloudTrail events to specific user actions.
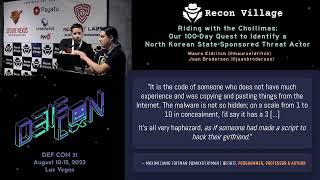
Identifying North Korean State-Sponsored Threat Actors Through Malware Analysis and OSINT
Uncover the journey of identifying a North Korean state-sponsored threat actor through malware analysis, OSINT investigation, and interviews with intelligence agencies and security forces.
Addressing InfoSec Requirements with Network Security Using Ansible
Automate network security tasks using Ansible, from segmentation to threat hunting, with real-world examples for IT operations and network administration.
Confused Learning: Supply Chain Attacks Through Machine Learning Models
Explore novel ML model vulnerabilities, including malware distribution and data exfiltration. Learn to create, distribute, and analyze ML malware, with insights on threat hunting and mitigation strategies.
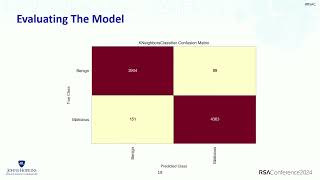
Threat Hunting with Python and Pandas - Data Science Techniques for Cybersecurity Analysis
Explore data science techniques for efficient threat hunting using Python, Pandas, and Scikit-Learn. Gain insights into applying these tools for enhanced cybersecurity analysis and operations.
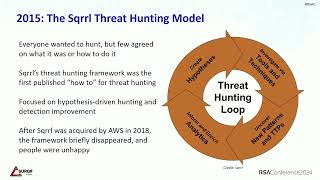
Threat Hunting Evolution: From Sqrrl Cycle to PEAK Framework
Discover how the PEAK framework revolutionizes threat hunting, addressing past mistakes and incorporating a decade of lessons to enhance cybersecurity programs beyond traditional incident detection.
Cloud Security Strategies: Threat Hunting, Adoption, and Incident Response - Part 2
Explore cloud security strategies, from threat hunting techniques to effective adoption frameworks and rapid response. Learn from industry experts about tools, skills, and best practices for securing cloud environments.
Begin Your Journey into DFIR, Blue Team, Malware and Threat Hunting
Explore digital forensics, blue team strategies, malware analysis, and threat hunting techniques with expert guidance for cybersecurity professionals and enthusiasts.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2024
Black Hat Europe 2024