Optimizing Your Azure Sentinel Platform with CyberProof
Enhance Azure Sentinel's threat detection capabilities with CyberProof's expert insights on cloud security, cost optimization, and advanced SOC management techniques.
Hunt Or Be Hunted
Explore advanced threat hunting techniques, datasets, and analytical approaches for effective cybersecurity. Learn to detect compromises missed by traditional methods and improve defensive strategies.
Advanced Internet Dataset Combinations for Threat Hunting and Attack Prediction
Explore advanced techniques for threat hunting and attack prediction using innovative Internet dataset combinations, moving beyond traditional methods for enhanced cybersecurity.
Fantastic Red-Team Attacks and How to Find Them
Explore prevalent gaps in organizational defenses through Atomic Red Team testing. Learn to identify and analyze complex attack patterns using Event Query Language and data analysis techniques.
Running a Security Operations Center - Challenges, Solutions and Key Learnings
Explore challenges and solutions in operationalizing a Security Operations Center, covering threat hunting, behavioral analytics, and rapid product deployment for enhanced cybersecurity.
A Process is No One - Hunting for Token Manipulation
Learn to generate hunt hypotheses for effective threat hunting, focusing on token manipulation techniques and targeted data collection for improved cybersecurity analysis.
Hunt and Gather - Developing Effective Threat Hunting Techniques
Explore innovative threat hunting techniques to stay ahead of hackers. Learn to plan, develop, and execute effective strategies for proactive cybersecurity and advanced threat detection.
Process is No One Hunting for Token Manipulation
Learn hypothesis-driven hunting techniques for detecting access token manipulation in Windows authentication, with practical case studies and demonstrations.
Threat Hunting - Defining the Process While Circumventing Corporate Obstacles
Learn effective threat hunting techniques, overcoming corporate challenges, and implementing data-driven methodologies for enhanced cybersecurity in this comprehensive presentation.
Detecting WMI Exploitation
Learn techniques to detect and prevent WMI exploitation, covering tools, processes, and best practices for enhanced Windows security and threat hunting.
SOC Automation - Enterprise Blueprinting and Hunting Using Open-Source Tools
Enhance SOC visibility and threat hunting using open-source tools. Learn network blueprinting, automation techniques, and advanced data analysis for effective cybersecurity operations.
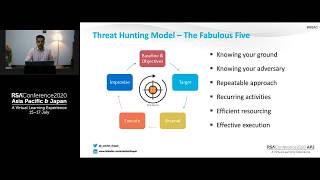
Threat Hunting - Demystified
Demystifies threat hunting as a cyber-defense strategy, exploring its implementation, phases, and best practices to effectively combat unknown threats in cybersecurity.
ICS SCADA Threat Hunting
Explore ICS SCADA threat hunting techniques, including generating hypotheses, leveraging threat intelligence, and analyzing real-world case studies to enhance cybersecurity in industrial control systems.
Threat Hunting in Active Directory Environment
Explore advanced threat hunting techniques in Active Directory, focusing on attacker persistence methods, privilege escalation, and covert system control. Learn to detect and mitigate sophisticated APT threats.
The Hunt for Major League IoT-ICS Threats - A Deep Dive into IoT Threat Terrain
Explore IoT security threats, automated threat hunting techniques, and advanced analysis methods to protect against malicious actions targeting millions of connected devices.
Common Flaws in ICS Network Protocols
Análisis de vulnerabilidades comunes en protocolos de red ICS, incluyendo públicos y privados. Demuestra ataques potenciales como inyección de comandos y sniffing de tráfico sin cifrado en infraestructuras críticas.
Threat Hunting - Using MITRE ATT&CK Against Carbanak Malware
Explore threat hunting using MITRE ATT&CK framework against Carbanak malware, covering tactics, techniques, and procedures for effective cybersecurity defense and mitigation strategies.
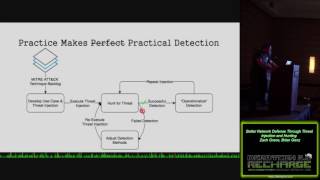
Better Network Defense Through Threat Injection and Hunting
Enhance network security through threat injection and hunting techniques, improving defense strategies and incident response capabilities.
Detection as Code - The Engineering-Focused Future of Detection and Response
Explore engineering-focused principles for building scalable threat detection programs, moving beyond traditional SOC models to create more effective and efficient security responses.
Threat Hunting - From Bodging to Efficiency in 7 Steps
Learn efficient threat hunting techniques in 7 steps, from basic concepts to advanced strategies. Ideal for aspiring hunters and professionals looking to enhance their cybersecurity skills.
Hunting Threats in Your Enterprise
Explore advanced threat hunting techniques and strategies for enterprise security, focusing on proactive detection and mitigation of cyber threats in complex environments.