Using Geopolitical Conflicts for Threat Hunting - How Global Awareness Can Enable New Surveillanceware Discoveries
Explore how global geopolitical awareness enhances threat hunting, enabling the discovery of new surveillanceware and nation-state malware in mobile security intelligence.
xRAT - Monitoring Chinese Interests Abroad With Mobile Surveillance-ware
Explore mobile surveillance-ware xRAT, used for monitoring Chinese interests abroad. Learn about threat detection, reverse engineering, and emerging mobile security challenges.
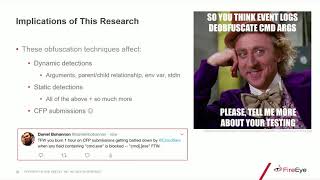
Invoke-DOSfuscation - Techniques for CMD Obfuscation
Explore advanced CMD obfuscation techniques used by threat actors, including string manipulation and encoding methods. Learn to create and detect complex obfuscated payloads using the Invoke-DOSfuscation framework.
Mining Disputed Territories - Studying Attacker Signatures
Explore attacker dynamics and signatures in cyber conflicts, leveraging insights for proactive defense and enhanced situational awareness in the cybersecurity landscape.
Hunting Android Malware with Importance Of Yara
Explore Android malware hunting using YARA framework. Learn techniques to identify and track malicious apps, even without direct access, and discover methods for detecting similar variants in the wild.
Hunting Them All
Explore advanced threat hunting techniques and strategies to proactively detect and mitigate cyber threats in complex network environments.
Offensive Hunting - Using Blue Team Techniques in Red Team Ops
Explore offensive hunting techniques combining red and blue team approaches. Learn to leverage data from various sources during extensive red teaming operations for more effective penetration testing.
Blinding Endpoint Security Solutions - WMI Attack Vectors
Explore new WMI attack vectors that disable EDR/AV/SIEM solutions. Learn about WmiCheck, a tool for detecting OS attacks. Discuss WMI architecture weaknesses and reliable event collection methods.
The Game of Cyber Threat Hunting - The Return of the Fun
Discover the excitement of cyber threat hunting through new approaches and a live demo, refocusing on its creative nature and eureka moments.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.
My Botnet Always Beats Yours - A Honeypot to Massive Bot Fight Scenes
Explore the fascinating world of IoT botnets through threat hunting stories, uncovering dramatic fight scenes between botnet herders and their evolving tactics in the dark web.
Practical Threat Hunting With Machine Learning
Explore practical applications of machine learning in threat hunting and detection, featuring case studies of high-value detections from two years of research and implementation.

Threat Hunting Using 16th-Century Math and Sesame Street
Discover innovative threat hunting techniques using mathematical principles and data analysis to uncover unusual machine behaviors in large-scale environments, transcending specific attack patterns.
Understanding the Discipline to Optimize Cyber Defense Collaboration
Explore the Cyber Threat Intelligence Analyst role, its competencies, and how it intersects with other cybersecurity disciplines to enhance collaboration and organizational security posture.
Powershell-Fu - Hunting on the Endpoint
Learn advanced PowerShell techniques for endpoint threat hunting, including methodologies, tools, and analysis modules for detecting and investigating malware and suspicious activities.
Threat Hunting in the Cloud
Explore cloud security challenges, attacker strategies, and effective threat hunting techniques in AWS and Azure environments. Learn to protect against and detect sophisticated cloud-based attacks.
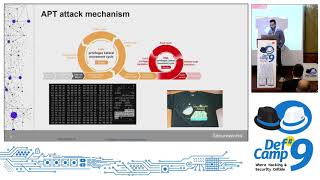
Catch Me If You Can – Finding APTs in Your Network - DefCamp - 2018
Explore advanced persistent threats (APTs), their attack mechanisms, and detection strategies. Learn threat hunting techniques to uncover hidden network vulnerabilities and enhance cybersecurity defenses.
Threat Hunting - From Platitudes to Practical Application - DefCamp - 2018
Practical guide to threat hunting, covering mindset, execution, and key considerations for cybersecurity professionals. Insights from DefCamp 2018 on enhancing defensive strategies.
Sigma - Generic Signatures for Log Events
Explore generic signatures for log events with Sigma, a YAML-based format for sharing and converting log signatures across different SIEM systems and query languages.
Cloud SIEM - What Happened and What's Next?
Explore cloud SIEM's impact on cybersecurity, from real-time threat detection to AI-driven responses. Learn how this technology reshapes security teams, risk management, and the future of threat hunting.
Signatures Are Dead - Long Live Resilient Signatures
Insights on creating resilient, high-fidelity threat detections that withstand evasion attempts, with practical examples from real-world attacks and methodologies for effective detection development.