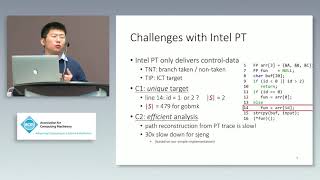
Enforcing Unique Code Target Property for Control-Flow Integrity
Explore control-flow integrity enhancement through unique code target property, addressing challenges in Intel PT implementation, security enforcement, and efficiency optimization.
Secure by Design: Insights and Pitfalls
Explore secure software design principles, their benefits, and potential pitfalls. Learn from real-world examples and gain insights on crafting more secure code through thoughtful design choices.
Side-Channel Attacks
Explore side-channel attacks, including Spectre, timing attacks, and countermeasures. Learn about developer knowledge, resistance techniques, and future directions in cybersecurity.
CeH Unit 1 - Business Aspects of Penetration Testing
Explore business aspects of penetration testing, including key terms, threats, data protection, and security procedures. Learn about ethical hacking and its role in cybersecurity.
Microsoft Vulnerability Research: How to Be a Finder as a Vendor - Notacon 11
Explore Microsoft's approach to vulnerability research, focusing on third-party findings, reporting processes, and lessons learned from case studies. Gain insights into effective vulnerability management.
Succeeding with Enterprise Software Security Key Performance Indicators
Learn to implement and measure effective enterprise software security KPIs. Discover strategies for aligning security goals with organizational objectives and improving development processes.
Protect Yourself from Malicious Dependencies with One Cool Trick
Learn strategies to safeguard your projects from harmful dependencies. Discover effective techniques for identifying and mitigating risks in your software supply chain.
Cybersecurity Challenges and Community-Based Risk Management
Explore cybersecurity challenges, risk management, and global tech trends with insights on patents, licensing, and community-based approaches to digital security.
Policy Compliance with Sigstore - From Signing Software to Validating the Whole Software Supply Chain
Explore sigstore for software signing and verification, and learn how to implement policy compliance in cloud-native software build and deployment processes using automation and tools.
Finding Multiple Bug Effects for More Precise Exploitability Estimation
Explore advanced techniques for estimating software vulnerabilities and enhancing exploit detection through multi-effect bug analysis and precise exploitability assessment.
Struts2 Vulnerability Workshop - Securing Applications Against Supply Chain Attacks
Explore software supply chain attacks, open source vulnerabilities, and security measures in modern development practices through hands-on exercises and real-world examples.
Vulnerable by Design - The Backdoor That Came Through the Front
Explore vulnerabilities in software design, historical backdoors, and their implications for security. Learn about notable cases and techniques for creating and detecting backdoors.
Large Scale Application Security
Explore large-scale application security strategies and best practices with insights from industry expert Charlie Eriksen at BsidesRI 2013.
The Goodness is Baked In - Baking Assurance into Software
Explore software assurance techniques to enhance security from the development stage, focusing on baking in goodness for robust and reliable applications.
Baking in Security - Lecture 1.2.5
Explore essential security practices for software development, emphasizing the importance of integrating security measures from the start of the development process.
Software Security Insights: A Conversation with Window Snyder - Intel's Chief Software Security Officer
Window Snyder discusses security challenges in open source and commercial software, hacking tactics, and strategies for improving application security, emphasizing the importance of security skills and addressing fear and shame.

Keeping Up with CVEs - Security Response Management Best Practices
Explore security update challenges, best practices, and tools for managing vulnerabilities in released products. Learn strategies to efficiently handle CVEs and maintain software security.
Exploiting Hardware Glitches and Side Channels in Perfect Software
Uncover vulnerabilities in flawless software through hardware glitches and side-channel attacks. Learn advanced exploitation techniques for enhancing cybersecurity defenses.
Secure Agile Development According to SAMM
Learn to integrate security into Agile development using SAMM principles. Explore challenges, practical solutions, and a hygiene approach for effective secure software development.
OWASP SAMM2 - Your Dynamic Software Security Journey
Explore OWASP SAMM2's dynamic approach to software security, enhancing your development practices and strengthening application defenses throughout the lifecycle.
Effective Usage Analysis: The Shortest Path Between Developer and Accelerated Product Releases
Discover how effective usage analysis prioritizes vulnerabilities, enabling developers to focus on exploitable risks, streamline remediation, and accelerate product delivery.