Weakest in the Herd - Securing End-of-Life Software
Explore strategies for identifying, assessing, and securing end-of-life software, including risk factors, potential threats, and mitigation techniques to enhance overall system security.
The Unabridged History of Application Security - Keynote
Comprehensive overview of application security's evolution, highlighting industry improvements and OWASP's global impact. Offers optimistic perspective on progress and future challenges in software security.
Embedding GDPR into the Software Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, threat modeling, and breach notification processes.
Dangerous Optimizations and the Loss of Causality in C and C++ Programming
Explore compiler optimizations in C/C++ that can lead to software vulnerabilities. Learn about mitigation strategies and the importance of maintaining causality in code.
Embedding GDPR Into the Secure Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, and breach notification processes.
When Bandit Strikes - Defending Your Python Code
Learn to defend Python code against security threats with insights from experts Will Bengtson and Travis McPeak. Discover proactive strategies and best practices for enhancing your application's security posture.
Scaling a Software Security Initiative - Lessons from BSIMM
Insights on scaling software security initiatives from BSIMM, covering best practices, challenges, and strategies for implementing robust security measures across large organizations.
Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
How to Review Code for Vulnerabilities - OWASP Standard Classification
Learn effective strategies for identifying vulnerabilities through source code review, including key concepts, starting points, and automation techniques. Practice reviewing code samples to enhance your application security skills.
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
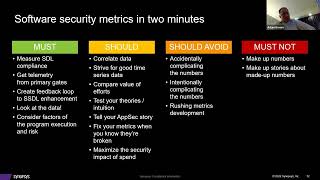
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
Reducing Software Vulnerability at a Global Scale
Explore strategies for reducing software vulnerabilities on a global scale, leveraging collective efforts of millions to enhance cybersecurity and protect digital ecosystems.
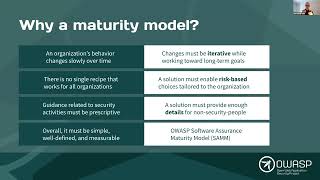
OWASP SAMM Project - Introduction to Software Assurance Maturity Model
Explore the OWASP SAMM framework for software assurance, learning key strategies to integrate security practices throughout the software development lifecycle.
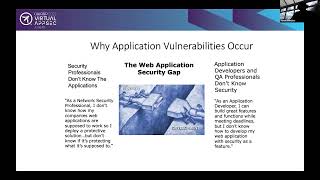
OWASP Open Application Security Curriculum Project
Learn essential application security concepts and practices from OWASP's comprehensive curriculum, designed to enhance your skills in identifying and mitigating software vulnerabilities.
Scaling AppSec through Education
Strategies for scaling application security through developer education, addressing the imbalance between security teams and developers and emphasizing code review for early bug detection.
The Cavalry Is Us: Protecting the Public Good in the Internet of Things Era
Exploring cybersecurity challenges in the Internet of Things era and the need for collective action to protect public interests and safety in an increasingly connected world.
Securing the Software Supply Chain with TUF and Docker - Protecting Against Distribution Attacks
Explore secure software updates with TUF framework, focusing on key revocation, mitigating attacks, and integrating with Docker's Notary for enhanced software supply chain security.
Talking TUF: Securing Software Distribution
Explore The Update Framework (TUF) for securing software update systems. Learn how to integrate this flexible security framework to protect against vulnerabilities and enhance software distribution safety.
Software Security Metrics - Developing Key Indicators for Executives
Techniques for effective communication with executives about software security, focusing on developing meaningful metrics to demonstrate progress and maturity in security capabilities.