Phantom Dependencies in AI and ML Projects - Managing Hidden Software Dependencies
Discover how phantom dependencies impact AI/ML projects and learn effective strategies for identifying, managing, and securing these hidden software dependencies in your applications.
The Current State of Software Bill of Materials (SBOMs) for End Users
Explore the challenges and opportunities of Software Bill of Materials (SBOMs), examining current implementation issues, regulatory requirements, and emerging solutions through OpenSSF projects like Protobom and bomctl.
Generating Software Bill of Materials Through Hardware Hacking - A Case Study of Bob the Minion Router
Dive into hardware hacking techniques for extracting firmware and generating Software Bill of Materials (SBOM) from a WiFi router, exploring vulnerability discovery through practical disassembly methods.
Eclipse Open VSX and Open VSX Registry - A Strategic Overview
Discover how Eclipse Open VSX and its registry serve as a marketplace solution, exploring Ericsson's strategy for decentralized deployment, security governance, and community-driven development initiatives.
Application of the Upcoming SPDX Safety Profile
Explore the SPDX Safety Profile for managing safety-critical projects, enhancing traceability, and maintaining documentation consistency across various tools and lifecycles.
SBOMs Go Global: Current State and Emerging Trends
Explore the global impact and emerging trends of Software Bill of Materials (SBOMs) with insights from industry expert Kate Stewart.
SBOM: The Inescapable Way of Tracking Dependencies
Explore SBOM's role in preventing cyber-attacks, its formats, and implementation across the software development lifecycle. Learn to generate, manage, and monitor SBOMs for enhanced security.
Activities in Japan and 10 Streams of OSS Security Mobilization Plan
Explore Japan's OSS security activities, SBOM adoption challenges, and potential certification uses in cloud services. Gain insights into unique industry perspectives and future preparedness.
Hardening the DevOps Pipeline with New Open-Source Security Tooling
Explore 5 phases of DevOps pipeline security using open-source tools. Learn about code signing, repo scanning, image SBOMs, OCI registries, pipeline audits, and evidence catalogs to enhance cybersecurity.
SBOMs Everywhere - Work in Progress and Challenges Ahead
Explore the progress and challenges of Software Bill of Materials (SBOMs) implementation across industries with insights from a leading expert in dependable embedded systems.
SBOM Everywhere - Understanding Software Bill of Materials
Explore the importance of Software Bill of Materials (SBOM) in securing open source supply chains and learn about its widespread implementation.
What's New in the World of SBOMs?
Explore recent developments in Software Bill of Materials (SBOMs) with industry experts, discussing advancements, challenges, and best practices in software supply chain security.
From Complexity to Clarity: Addressing Challenges in AI BOMs for Compliance
Explore strategies for implementing AI Software Bill of Materials (SPDX 3.0) to navigate compliance challenges and create accurate, machine-readable documentation for AI systems.
SBOM Implementation Reality: From Crawl to Walk - SPDX Lite Profile for the First Step
Discover how to create Software Bill of Materials (SBOMs) efficiently using SPDX Lite profile, featuring practical JSON examples and implementation strategies for meeting regulatory requirements in software supply chains.
A Practical Guide to Using International Standards for Open Source Procurement
Discover how to leverage international standards for effective open source procurement, focusing on license compliance, security assurance, and SBOM to enhance supply chain management.
The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.
SBOM Management with SW360 - Cross-Industry Perspectives and Best Practices
Discover how SW360 enables effective software component management through real-world implementations at Siemens and Toshiba, including SBOM integration and customization strategies for diverse organizational needs.
SBOM Implementation Reality - The SPDX Lite Profile for First Step
Explore SPDX Lite profile for creating lightweight SBOMs. Learn practical steps to implement Software Bill of Materials using simplified SPDX 3.0 specifications, addressing regulations and requirements.
Keeping Your Kubernetes Cluster Secure
Discover open-source tools for securing Kubernetes clusters at multiple levels, from hardening nodes to monitoring container behavior and enforcing policies.
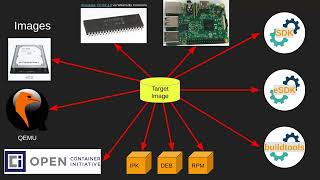
Software Bill of Materials (SBoM) and Supply Chain with the Yocto Project - Generating and Using SBoMs
Explore Software Bill of Materials generation, usage, and future in Yocto Project, emphasizing supply chain security and reproducible builds.
Software Bill of Materials in DevOps, DevSecOps, and Value Stream Management
Explore the evolving concept of Software Bill of Materials in DevOps and DevSecOps, discussing its expanded scope, security implications, and modern purposes.