How the Argo Project Transitioned From Security Aware to Security First
Discover how the Argo project enhanced its security strategy, implementing best practices, formalizing processes, and leveraging community resources to transition from security-aware to security-first.
SBOM X-Ray Superpowers: Making Better SBOMs and Using SBOMs
Explore innovative techniques for enhancing SBOM accuracy and completeness using SBOM discovery, look-up, and transparency logs. Learn to leverage these methods to improve software security and vulnerability response.
Our Own "Jungle" of the Commercial Software Supply Chain
Explore the complexities of commercial software supply chains, focusing on SBOMs, quality ingredients, and upstream investments to enhance security and efficiency in software development.
Dependency-Track: Intelligent Software Composition Analysis Platform
Explore Dependency-Track, an intelligent SCA platform for identifying and reducing risks from third-party components. Learn about its bill-of-material approach and automation options for continuous component analysis.
Cloud Native Application Security Governance Based on SBOM
Explore cloud-native app security governance using Software Bill of Materials (SBOM) for enhanced protection and compliance in modern software development.
Managing Containerized Software on Edge Computers with Open Horizon
Explore Open Horizon's architecture for managing containerized software on edge devices, addressing challenges and showcasing real-world applications.
Managing Application Level SBOMs with Ortelius
Explore application-level Software Bill of Materials (SBOMs) management using Ortelius, enhancing software supply chain security and transparency in modern development practices.
Generating Software Bill of Materials - Mentorship Session
Learn to generate Software Bill of Materials (SBOM) for efficient analysis of software supply chain, covering available options and open source tools for SBOM creation and usage.
Assessing Project Risk Using CHAOSS Metrics
Learn to assess open source project risks using CHAOSS metrics, covering security, code quality, licensing, transparency, and sustainability. Gain insights into measuring project health and performance.
From SBOMs to IBOMs - Know What's Happening in Your Clusters
Explore the importance of Infrastructure Bill of Materials (IBOM) in cloud-native environments, its role in security, and how to leverage it for cost optimization and reducing attack surfaces.
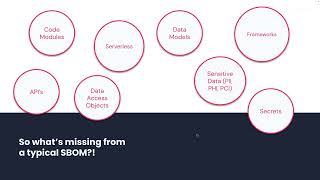
Why You Need an XBOM - The Extended Software Bill of Materials
Explore the extended Software Bill of Materials (XBOM) concept, its importance in software development, and the benefits of adopting this approach for enhanced security and transparency.
SW360 SBOM - Managing Vulnerability Information, SPDX Documents and Dependency Networks
Explore SW360's features for managing software components, including vulnerability tracking, SPDX document handling, and dependency network visualization for enhanced license compliance and security.
How to Benefit from SBOM in Metaverse Applications
Explore the process of creating a Software Bill of Materials (SBOM) for Metaverse technologies, including component identification, relationship definition, and visual representation.
Our Journey to Open Source - From a Conservative Japanese Company
Explore Hitachi Solutions' journey from a conservative Japanese company to launching their first open-source project, "Editor for SBOM," overcoming cultural barriers and embracing innovation.
Utilizing Package-URLs for SBOM Management and Vulnerability Tracking
Explore SBOM management, Software Composition Analysis, and vulnerability tracking using Package-URLs and VulnerableCode for effective open-source component handling and policy compliance.
SBOM for Cloud Services - Challenges and Applications
Explore the concept of Software Bill of Materials for cloud services, its challenges, and potential applications in enhancing security and transparency in cloud computing.
Trusting Your Open-Source Software Supplier
Explore open-source software security challenges in the public sector, covering policy compliance, SBOM directives, and evolving threat landscapes to enhance your software supply chain protection.
SPDX 3.0 Overview - Introduction to Software Package Data Exchange
Explore the latest updates and enhancements in SPDX 3.0, the open standard for software bill of materials, and learn how it improves software supply chain transparency and security.
Container Image Workflows at Scale with Buildpacks
Explore Buildpacks for transforming source applications into cloud-ready images, enabling efficient deployment and management of container workflows at scale across various use cases.
Dark Matters: The Security Abyss of Distroless Containers
Explore hidden vulnerabilities in distroless containers, their security challenges, and potential solutions like SBOM and Chisel for creating secure, stable, and ultra-small Ubuntu containers.
Building Supply Chain Policies with Gatekeeper and Ratify
Learn to enhance Kubernetes security using Gatekeeper and Ratify for supply chain policy enforcement. Explore admission controllers, CRD-based policies, and external data verification for robust cluster protection.