Demystifying SBOMs: Strengthening Cybersecurity Defenses
Explore Software Bill of Materials (SBOMs) as a crucial tool for enhancing cybersecurity, identifying vulnerabilities, and managing software supply chain risks in organizations.
Securing the Software Supply Chain - SBOMs and Their Impact
Explore software supply chain security, SBOMs, and their impact on open source. Learn about transparency challenges and the potential effects of the Cyber Resilience Act.
Introducing OpenChain Japan Community's SBOM Initiatives
Explore Japan's SBOM initiatives, SPDX 3.0 contributions, and future outlook. Gain insights on software supply chain security, practical SBOM adoption, and global implications for stakeholders.
The Evolution of SBOMs in AlmaLinux
Explore AlmaLinux's SBOM generation process, its evolution to meet NTIA requirements, and the implications for RPM-based Linux distributions. Learn about challenges and solutions in software supply chain security.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
Beyond the Code - SBOM and Supply Chain Security
Explore supply chain security, focusing on Software Bill of Materials (SBOM) and its role in enhancing software transparency and risk management in modern development practices.
Fresh SLSA and GUAC - Understanding Open Source Package Risks and Transparency
Explore open source package risks, transparency, and tools like GUAC, SLSA, and SBOMs to enhance software supply chain security and make informed decisions on dependencies.
DHS Supporting Critical Infrastructure Through Open-Source Software Prevalence Effort
Explore DHS's innovative methodology for identifying and assessing OSS in IT/OT devices, enhancing critical infrastructure cybersecurity through comprehensive vulnerability scoring and risk management.
Supply Chain Security with KubeClarity: Introduction and Implementation
Explore supply chain security fundamentals, historical attacks, and KubeClarity tool. Learn about SBOMs, their benefits, and see KubeClarity in action for enhanced software security.
Securing Python Projects Supply Chain
Explore best practices and tools for securing Python projects' supply chain, from development to distribution. Learn about cryptographic signatures, SBOMs, and SLSA attestations.
Tackling Software Supply Chain Security as an Organization - Episode 128
Explore organizational approaches to software supply chain security with experts discussing solutions, initiatives, and best practices for managing risks and improving visibility.
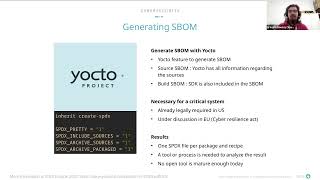
Generating SPDX Software Bill of Materials with Yocto Project
Generate SPDX Software Bill of Materials with Yocto Project. Learn practical details, usage of "create-spdx" class, and control variables for customized SPDX output.
The LF Energy Seapath Project: Yocto Applications in Power Grid Automation
Explore SEAPATH, an open-source platform for power grid substation automation. Learn about its development, transition to virtualization, and the role of Yocto in cybersecurity, SBOM, CI/CD, and licensing.
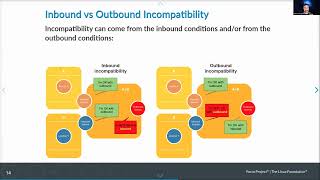
OSPO-Ready Yocto Projects - The Data You Didn't Know You Had
Explore OSPO-ready Yocto Projects using graph databases for enhanced compliance checks, SBOM generation, and IP litigation support. Learn to leverage file-level data for automated analysis.
Security Posture Assessment and Improvements for Open Source Projects
Explore essential security practices for open source projects, including fuzzing, SBOM, and SSDLC. Learn to assess vulnerabilities and maintain robust security postures through real-world examples.
Becoming a Link in Securing the Software Supply Chain
Explore open source security fundamentals, challenges, and opportunities. Learn how to contribute to existing communities and play a role in securing the software supply chain ecosystem.
Defining the Limits of Risk in Open Source Supply Chains
Explore community-metrics-related risks in open source projects, focusing on sustainability and potential threats beyond source code, to enhance supply chain security discussions.
Generating Software Bill of Materials (SBOM) Using AWS Inspector
Learn how to generate and utilize Software Bill of Materials (SBOM) through AWS Inspector, covering both console and CLI approaches for effective software component tracking.
Understanding Risk: Supply Chain Transparency and SBOM
Gain insights into supply chain transparency and SBOM implementation strategies for better risk management and security in IoT ecosystems.
Understanding and Implementing Software Bill of Materials (SBOM) for Secure Development
Discover how Software Bill of Materials (SBOM) enhances software security by providing transparency into dependencies, ingredients, and supply chains, with practical examples from Eclipse Temurin.
Secure Software Factory - Adding SBOM and Code Signing to Security Checks
Enhance your security checks with SBOM and code signing in a secure software factory, improving software supply chain integrity and compliance.