Leverage Kubernetes SPDX Tools to Create Your SBOM
Explore Kubernetes SPDX tools for efficient SBOM creation, organization, and management. Learn to leverage SPDX features and understand future directions in software bill of materials.
License Compliance and Security Management for Embedded Systems
Explore license compliance and security management for embedded systems, focusing on SBOM implementation, SPDX file generation, and effective problem-solving tools.
Supply Chain Attacks: The New Reality
Explore software supply chain vulnerabilities, threats, and best practices for securing your ecosystem in this comprehensive overview of modern cybersecurity challenges.
Building a Secure Future: Lessons from Past and Present Information Security Challenges
Explore the future of information security, examining past lessons, current challenges, and emerging technologies like quantum cryptography to build a more secure digital world.
Software Bill of Materials (S-BoM) - Reducing Risk in Third-Party Components
Explore best practices for managing third-party component risks using software bill-of-materials (S-BoM). Learn to create S-BoMs, identify vulnerabilities, and automate security responses in polyglot environments.
SBOM SmackDown - Conquering Software Supply Chain Risks with OWASP CycloneDX
Explore Software Bill of Materials (SBOM) and learn how OWASP CycloneDX standard enhances software supply chain transparency, enabling better risk-based decisions and compliance with government mandates.
OWASP CycloneDX - Software Bill of Materials Standard
Explore OWASP CycloneDX, a lightweight software bill of materials (SBOM) standard, with experts Steve Springett and Patrick Dwyer. Learn about its features, applications, and importance in modern software development.
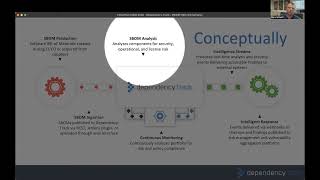
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
Realtime Systems, RISC-V Vector Processing, Open Source in Europe, and Software Transparency - Keynotes Day 3
Explore cutting-edge topics in open source technology with expert keynotes on realtime systems, RISC-V processors, strategic challenges, and software transparency.
Auto Generate SBOMs for Open Source Projects in Any Language and Platform
Learn to automatically generate Software Bill of Materials (SBOMs) for open source projects, enhancing security and compliance across languages and platforms.
Generating a SPDX SBOM for Your Code in CI Using ORT
Learn to generate SPDX Software Bill of Materials (SBOM) for your code in continuous integration using the OSS Review Toolkit (ORT), enhancing software transparency and security.
What's in a Name - Vulnerabilities, SBOMs, and the Challenge of Software Identity
Explore software identity challenges in supply chain security, examining existing naming standards, potential risks, and collaborative solutions for effective vulnerability management.
State of SBOM Tools - Improving Software Supply Chain Security
Explore the current state of SBOM tools, discussing improvements, standards support, interoperability, and accuracy to enhance software supply chain security.
A Different Kind of S3 - First Line Security of the Supply Chain
Explore three core areas for securing the software supply chain: Software Bill of Materials (SBOM), Signing, and Slimming. Learn practical methods to enhance first-line security controls and minimize attack surfaces.
Japan's Critical Infrastructure - Open Source Evolution in Software Development
Japan's critical infrastructure evolution: Open source trends, security considerations, and Linux Foundation projects enhancing dependability, transparency, and reproducibility for future software needs.
Realities of SBOM - What Is Under the Hood of Software Bill of Materials
Explore the complexities of Software Bill of Materials (SBOM) beyond dependency files, including interdependencies, integrity, and vulnerability monitoring across the software development lifecycle.
Understanding the Role of Software Bill of Materials in Cybersecurity Readiness
Explore the importance of Software Bill of Materials (SBOMs) in cybersecurity, including adoption challenges, implementation benefits, and strategies for improving production and consumption rates.
Securing the Software Supply Chain: From Threats to Best Practices
Comprehensive overview of software supply chain security, covering history, threats, initiatives, challenges, and best practices. Experts discuss key issues and solutions for organizations.
SBOMs for Embedded Systems - What's Working, What's Not
Explore challenges and successes in implementing Software Bill of Materials (SBOMs) for embedded systems, discussing regulatory impacts, generation methods, and practical applications.
Corporate Use of Embedded Linux
Explore corporate challenges and strategies for embedded Linux, including upstream drivers, compliance, and testing, with insights from Sony Corporation.