Better SIEM Notifications - Making Your SIEM Situationally Aware
Enhance SIEM effectiveness by implementing situational awareness techniques, improving notification accuracy, and leveraging additional data sources for better threat detection and response.
This Is Not Your Grandfather's SIEM
Explore modern CSOC analytic platforms, their design considerations, and evolving approaches to security event monitoring, analysis, and response in complex cybersecurity environments.
Splunking the Clouds - Finding the Needle in AWS & Azure
Explore cloud security techniques for AWS and Azure, focusing on identifying and addressing potential vulnerabilities using Splunk's powerful data analysis capabilities.
SIEM There, Done That - Rising Up in the SecOps Revolution
Explore the future of cybersecurity through automation and intelligence, moving beyond traditional SIEM solutions to address modern SecOps challenges and usher in a new era of protection.
The Excellent Adventure of XDR – Where is it Going?
Explore the evolving world of extended detection and response (XDR), its potential as a SIEM alternative, and how it enhances security analysts' efficiency in threat detection and response.
Kafka on Kubernetes - From Evaluation to Production at Intuit
Explore Intuit's journey of running Kafka on Kubernetes in AWS, covering evaluation, testing, configuration, and integration with monitoring tools. Learn about challenges faced and solutions implemented.
Evil Empire - SIEM FTW
Explore SIEM technology's role in cybersecurity with insights on implementation, benefits, and best practices for effective threat detection and incident response.
Honeypots for Active Defense - A Practical Guide to Deploying Honeynets Within the Enterprise
Practical guide to deploying honeynets for active defense within enterprises, covering various honeypot types, use cases, and monitoring techniques for enhanced threat intelligence.
Lessons Learned from Building and Running MHN - the World's Largest Crowdsourced Honeynet
Explore insights from managing the world's largest crowdsourced honeynet, covering architecture, community growth, and global attack patterns in cybersecurity.
Deploying Honeypots to Gather Actionable Threat Intelligence
Explore deploying high-interaction honeypots for gathering actionable threat intelligence, including setup considerations, virtualization challenges, and cloud implementation strategies.
SIEM Supersized
Explore advanced SIEM techniques and strategies for enhancing cybersecurity monitoring and threat detection in enterprise environments.
Garbage in Garbage Out - Generating Useful Log Data in Complex Environments
Explore effective log data generation in complex environments, focusing on meaningful data, thresholds, and log management systems for improved security and analysis.
So You've Inherited a Security Department - Now What
Learn essential strategies for managing an inherited security department, covering OSINT tools, best practices, and key areas like compliance, user education, and vulnerability scanning.
Weaponizing Splunk - Using Blue Teams for Evil
Explore how attackers can exploit Splunk for malicious purposes, including data extraction and command control, in this eye-opening cybersecurity presentation.
To SIEM or Not to SIEM - An Overview
Explore the pros and cons of Security Information and Event Management (SIEM) systems, their implementation challenges, and alternatives for effective cybersecurity monitoring.
Security Instrumentation - Be the Hero Getting Value from Security
Explore security instrumentation techniques to enhance organizational defenses, measure effectiveness, and demonstrate value in cybersecurity investments.
2018 SIEM Trends - What is My Mean Time to Value
Explore SIEM trends, from traditional approaches to next-gen solutions incorporating cloud, data science, and advanced analytics. Gain insights on future developments in security information and event management.
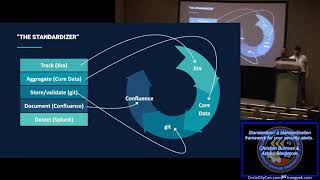
Standardizer - A Standardization Framework for Your Security Alerts
Learn about Standardizer, a framework for security alert standardization, covering metadata, core data, transformations, and application processes.
Finding the Issues in Microservices Applications
Discover techniques for identifying and resolving issues in complex microservices architectures using rich observability data, real-time analytics, and advanced monitoring tools.
Annotating Log Data for Machine Learning
Explore an NLP-based log analysis system for automated error triage and fault categorization, streamlining root cause analysis in complex log data.
SIEM with Elastic - Security Insights and DevOps Freedom in Cloud Services
Discover how to implement unified SIEM solutions using Elasticsearch, balancing centralized security management with DevOps team autonomy in cloud environments.