Build Yourself a SNMP Replacement - And Make SSH Pay for It
Wireless-Netzwerkmanagement ohne SNMP: Python und SSH für effektives Monitoring. Umgehung von Hardware-Einschränkungen und Integration von Splunk und Observium.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.
A Serverless SIEM - Detecting All Baddies
Explore a serverless SIEM for efficient threat detection, covering log ingestion, analysis, notifications, and automations in cloud-native environments.
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
How to Exploit Cloud Adoption for Making Your IT More Secure and Convenient for End Users - DefCamp #10
Explore cloud adoption strategies to enhance IT security and user convenience, covering encryption, identity protection, and real-life implementation scenarios.
Threat Intelligence! DIY! - DefCamp - 2016
Aprenda a implementar inteligência de ameaças DIY usando Splunk. Descubra técnicas práticas para configurar, pesquisar e criar dashboards para melhorar sua segurança da informação.
Sigma - Generic Signatures for Log Events
Explore generic signatures for log events with Sigma, a YAML-based format for sharing and converting log signatures across different SIEM systems and query languages.
Cloud SIEM - What Happened and What's Next?
Explore cloud SIEM's impact on cybersecurity, from real-time threat detection to AI-driven responses. Learn how this technology reshapes security teams, risk management, and the future of threat hunting.
Secure, Monitor and Govern Server Workloads Across Hybrid Multicloud and Azure
Centrally secure, manage, and govern server workloads across hybrid multicloud environments using Azure services. Learn about Azure Arc, Defender for Cloud, Sentinel, Monitor, and Automanage for comprehensive infrastructure management.
Optimizing Your Azure Sentinel Platform with CyberProof
Enhance Azure Sentinel's threat detection capabilities with CyberProof's expert insights on cloud security, cost optimization, and advanced SOC management techniques.
Defending Against OT - ICS Threats with an OT-Enabled SOC
Learn to defend against OT/ICS threats by building an OT-enabled SOC. Explore attacker techniques, defense challenges, and key requirements for protecting critical infrastructure and industrial systems.
Protect Everything with End-to-End Security
Discover Microsoft's integrated security approach, protecting against cyber threats in the hybrid work era. Learn about new products safeguarding endpoints, cloud, and privacy across organizations.
Building the Super-Dynamic Demo Center
Modernize field sales engineering demos using Docker and CI pipeline for efficiency, flexibility, and new use cases. Transition from manual DevOps to Docker Service-based demo center with Swarm Mode and Splunk analytics.
How a Large Media Company Uses Splunk for Analytics-Driven Container Performance and Logging
Discover how BILD GmbH leverages Splunk for container performance monitoring, logging, and troubleshooting in their news portal infrastructure, offering insights for developers and operations teams.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.
Cloud-Powered Compromise Blast Analysis - In the Trenches with Microsoft IT
Discover advanced methods for identity compromise detection using cloud logs, SIEMs, and telemetry. Learn from Microsoft's experience in protecting millions of authentications.
Cloud Threat Hunting
Proactive cloud threat detection techniques, including honeyclouds, integrated monitoring, and AI-driven behavioral analysis for mitigating orchestration attacks and cross-tenant threats.
To Catch a Penetration Tester - Top SIEM Use Cases
Discover top SIEM use cases for detecting penetration testers, including password spraying, antivirus alerts, and unusual account activities. Learn to enhance your organization's security monitoring capabilities.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.
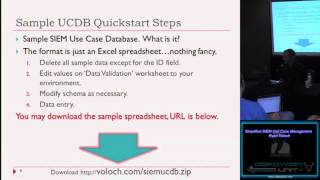
Simplified SIEM Use Case Management
Learn to manage SIEM use cases effectively with a database approach, improving security monitoring and incident response capabilities in your organization.
Can You Roll Your Own SIEM
Explore building a custom cloud-native SIEM solution, discussing considerations, requirements, and benefits compared to vendor options. Learn about cost savings and improved capabilities.