Building a Minimal Security Onion VM with sosetup-minimal
Learn to set up a minimal Security Onion virtual machine with dual NICs, focusing on Evaluation Mode installation and basic configuration for network security monitoring.
Security Logging Use Cases: Building an Open-Source SIEM
Explore building an open-source SIEM using Fluentd and Fluent Bit. Learn about data collection, enrichment, correlation, and real-world security infrastructure examples for effective threat detection and analysis.
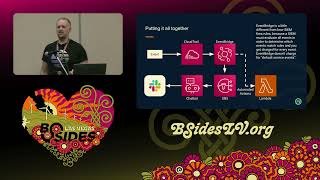
Big SIEM Energy at Micro-SIEM Cost - Building Custom Security Monitoring in AWS
Learn to build a cost-effective micro-SIEM for AWS using EventBridge, CloudTrail, SNS, and ChatBot. Discover how to tailor security monitoring to your specific needs and budget constraints.
Automated Incident Response - Streamlining Processes and Enhancing Efficiency
Explore innovative Slack-based tools for streamlining incident response processes, reducing overhead, and enhancing efficiency through automation and integration with critical cloud-based systems.
Forwarding Snort Logs to Splunk
Learn to forward Snort logs to Splunk for powerful data analysis and monitoring. Explore Splunk's web interface to search, analyze, and visualize machine-generated data, enhancing your cybersecurity capabilities.
Installing and Configuring Wazuh for SIEM - Blue Team Operations
Learn to set up Wazuh SIEM for detecting intrusions, attacks, and malicious activity. Covers installation and agent configuration on Windows and Linux for effective security data management.
The Always-On Purple Team: Automated CI/CD for Detection Engineering
Innovative architecture for automated detection engineering CI/CD pipeline, merging SOC technologies, SIEM/XDR, SOAR, BAS, and ChatGPT. Includes live demo of creating, testing, and deploying detection analytics.
Unifying XDR and SIEM: A New Era in Security Operations
Explore innovations in AI, attack disruption, threat intelligence, and cloud security to enhance threat detection and response, boosting productivity for security teams.
Microsoft Sentinel - A Modern Approach to Security Operations
Explore Microsoft Sentinel's AI-powered security operations, featuring live demonstrations of SOC optimization, threat investigation, and advanced response capabilities for modern cybersecurity challenges.

SOC Analyst: Top Interview Questions and Answers for Security Operations Center - 2024
Master SOC analyst interview skills with scenario-based prep on threat detection, incident response, and vulnerability management. Gain practical insights to excel in security operations and stand out to potential employers.
Infrastructure as Code, Automation, and Testing in Detection Engineering
Explore detection-as-code for security teams: automate, test, and deploy robust detection systems using Azure DevOps, Microsoft Sentinel, and Defender suite. Improve effectiveness and maintain control across environments.
Building a Secure and Scalable Cybersecurity Lakehouse - Rivian's Approach
Rivian's innovative cybersecurity lakehouse enables real-time, cross-team detections, automating response management. This scalable solution reduced implementation time and increased coverage, outperforming proprietary SIEM systems.

Splunk: Cloud-Native Infrastructure Monitoring at Scale
Gain end-to-end visibility into infrastructure and application performance with Splunk's cloud-native monitoring platform. Deploy easily, detect issues proactively, and leverage ML for insights.

Introduction to Splunk - Big Data Platform for Cybersecurity and Observability
Learn to leverage Splunk's big data platform for cybersecurity, observability, and network operations, empowering large organizations with essential data-driven capabilities.
Cyber & Data - What is Data?
Explore data types, formats, and structures in cybersecurity. Learn parsing, encoding, compression, and file analysis techniques for effective data handling and security.

ETL Observability: Azure to Snowflake - Monitoring with Splunk and Power BI
Explore ETL monitoring from Azure to Snowflake using ADF, Splunk, and Power BI. Learn data lineage and observability techniques for efficient pipeline management.
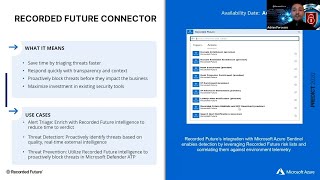
Leverage Recorded Future Playbooks to Automatically Integrate Threat Intelligence with Microsoft Azure
Automate threat intelligence integration in Microsoft Azure using Recorded Future Playbooks for enhanced detection, enrichment, and prevention in Sentinel and Defender ATP.
Mapping Motives: Analysis of 2,000 Enterprise Cloud Detections - Strengthening Multi-Cloud SOC
Analysis of 2,000 cloud detections reveals enterprise control patterns, gaps, and attacker motives. Learn to strengthen multi-cloud security operations with actionable insights and MITRE ATT&CK framework application.
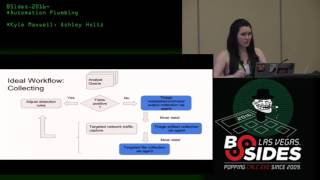
Automation Plumbing
Explore efficient automation workflows for cybersecurity, covering detection, aggregation, processing, and plumbing solutions using tools like Python, Elastic Search, Splunk, and Log Stash.
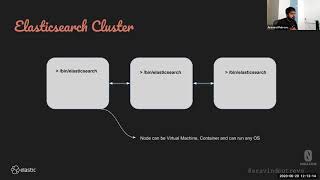
Building a Security Platform with Elastic Stack - Part 1
Learn to build a security platform using Elastic Stack. Explore basic components, data ingestion tools, data management, and cluster security. Gain insights from an experienced developer on leveraging SIEM for effective security monitoring.

Who Watches the Watchmen - Adventures in Red Team Infrastructure Herding and Blue Team OPSEC Failures
Explore red team infrastructure management and blue team OPSEC failures. Learn about RedELK, a tool for controlling operations and detecting blue team activities during multi-month engagements.