Hell-0 World - Hacking IoT Weather Stations
Uncover IoT vulnerabilities in Tuya-based devices, focusing on weather stations. Learn to manipulate device operations through firmware extraction and reverse engineering techniques.
The Dark Side of TheMoon - Uncovering Botnets and Criminal Proxy Networks
Uncover the resurrection of "TheMoon" botnet and its connection to "Faceless," a growing criminal proxy network. Learn about botnet mechanics, proxy dangers, and router vulnerabilities.
The B-Side of Ransomware - Exploring Lesser-Known Threats
Explore lesser-known ransomware attacks, their tactics, and why they failed to gain notoriety. Gain insights into the evolving threat landscape and enhance cybersecurity preparedness against diverse potential attacks.
Finding and Exploiting Critical Vulnerabilities in RPC Services - NorthSec 2023
Comprehensive walkthrough of finding, exploiting, and reporting critical vulnerabilities in an RPC service, covering reverse engineering, authentication bypass, and coordinated disclosure.
Hacking Arcade Cashless Systems: Vulnerabilities and Exploits
Explore vulnerabilities in global arcade cashless systems, covering API security, access control, and NFC. Learn how to exploit weaknesses for potential free play in amusement parks worldwide.
Practical Steps to False Positive Reduction and Benign File Analysis
Learn efficient techniques for identifying false positives and analyzing clean files in malware analysis. Gain actionable tips from real-world examples to enhance your workflow and save time and resources.
PE File Format Basics for Malware Analysis and Reverse Engineering - MM#08
Explore PE file format essentials for malware analysis using tools like Detect-It-Easy, PEStudio, and Malcat. Learn to interpret tool outputs and understand file structure for effective triage analysis.
Apple CarPlay - What's Under the Hood
Explore Apple CarPlay's inner workings, security implications, and potential vulnerabilities in this IT security conference talk by Hannah Nöttgen at TROOPERS24 in Heidelberg.
Hacking Arcades for Fun - Insert Coin
Explore arcade game vulnerabilities and hacking techniques in this engaging talk on security flaws in gaming systems, offering insights for both enthusiasts and security professionals.
The AddressOfEntryPoint and Tips for Finding Main in PE Files
Explore the AddressOfEntryPoint field in PE files, its relation to the main function, and techniques for locating it. Learn about PE file structure and entry point analysis.
TLS Callbacks in PE Files - Detection and Analysis
Explore TLS callbacks in PE files, their use in malware, and detection methods. Learn to identify and analyze these anti-debugging techniques using various tools and Yara rules.
Finding Digital Certificates in PE File Format
Learn to identify and extract digital signatures in PE files using the DATA_DIRECTORY structure, RVAs, and tools like Malcat for enhanced cybersecurity and malware analysis skills.
Nokia TCSM2: Bank of TRAUs with E1 Interfaces - Part 1 - Initial Hardware Examination
Explore Nokia TCSM2 hardware: in-depth examination of TRAU bank with E1 interfaces, focusing on initial hardware inspection and analysis.
Performing Basic Triage Analysis and Unpacking with x64dbg - Ransomware Analysis - Part 2
Perform basic triage analysis on ransomware binaries, compare obfuscated and unobfuscated versions, and learn to unpack using x64dbg and Scylla for effective malware analysis.
Tips From a Hacker on License Checking
Explore techniques used by crackers and learn how to design more secure license checking schemes for audio software, improving protection against piracy.
Defense Through Offense: Microcontroller Security in Meta's First Generation of Smart Glasses
Explore microcontroller security in Meta's smart glasses, focusing on defense strategies through offensive techniques and real-world applications.
ACE up the Sleeve: Hacking into Apple's New USB-C Controller
Explore Apple's USB-C controller vulnerabilities and hacking techniques with expert Thomas Roth in this cutting-edge cybersecurity presentation.
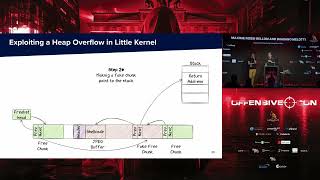
Attacking the Samsung Galaxy A Boot Chain
Explore Samsung Galaxy A* boot chain vulnerabilities and attack techniques for enhanced mobile security understanding.
Booting with Caution: Dissecting Secure Boot's Third-Party Attack Surface
Dissect Secure Boot's third-party attack surface, exploring vulnerabilities and potential exploits in boot processes.
Open Sesame: Stack Smashing Your Way into Opening Doors
Explore stack smashing techniques to bypass security measures in electronic door locks, uncovering vulnerabilities and potential exploits in physical access control systems.
Building Your Code Safe: Applying DevSecOps Culture with Open Source Tools
Aprenda a usar ferramentas SAST de código aberto para análise estática, identificando vulnerabilidades em várias linguagens durante o desenvolvimento e obtendo uma visão gerencial das falhas de segurança.