Reverse Engineering MicroPython Frozen Modules
Dive into advanced techniques for identifying and reverse engineering frozen MicroPython modules in firmware using Ghidra, focusing on bytecode analysis and module reconstruction methods.
Detecting Persistent Threats on Draytek Devices - Security Assessment and Mitigation Tools
Discover how to detect and mitigate persistent threats on Draytek devices through firmware analysis, reverse engineering, and custom security module development for enhanced network protection.
Understanding File Type Identifiers and Scanners
Dive into file type identification techniques and scanning mechanisms, exploring how different systems detect and process various file formats for enhanced digital forensics and security.
Creating Trampolines and Re-Obfuscating Function Pointers in Runtime Linking - Part 7
Delve into advanced runtime linking techniques, focusing on trampoline creation, function pointer resolution, and memory debugging in reverse engineering and malware analysis.
Building a IIe-compatible Computer with the Mega-II Chip - KansasFest 2022
Explore the creation of an Apple IIe-compatible computer using the Mega-II ASIC chip from the Apple IIGS. Learn about hardware challenges, differences from the original IIe, and see a demo of the Mega IIe in action.
Playing Video Games One Frame at a Time
Explore game automation techniques using C++, from built-in tool support to code injection. Learn to enhance gameplay and overcome challenges through programming.
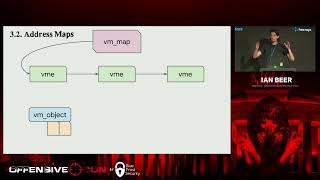
MacDirtyCow: Auditing and Exploiting XNU Virtual Memory
Explore XNU virtual memory auditing and exploitation techniques, focusing on the MacDirtyCow vulnerability in Apple's operating systems.
Open Source Components in Cloud Services: A Deep Dive into Managed Offerings
Explore the open-source components in managed cloud services, focusing on Red Hat's offerings and the tools used to manage OpenShift clusters at scale.
Shared Libraries in Windows and Linux - Linking and Loading Deep Dive
Dive deep into linking and loading operations, exploring binary structures, static vs dynamic linkage, and Linux vs Windows differences. Gain clarity on opaque linker error messages.

Key Takeaways from 5 Years of Developing and Maintaining Open Source Projects for iOS Device Automation
Explore reverse engineering, open-source development, and iOS automation using Go. Learn about community building, motivation, and overcoming technical challenges in long-term projects.
Reverse Engineering Python Binaries - There and Back Again
Uncover Python bytecode secrets: Learn to interpret and decompile .pyc files, explore challenges in automated decompilation, and gain insights into recovering source code from bytecode.
WatchWitch - Hacking the Apple Watch
Explore Apple Watch vulnerabilities and hacking techniques in this IT security conference talk. Gain insights into potential exploits and security considerations for wearable technology.
Printer Hacking Adventures - Exploiting Network Vulnerabilities
Explore printer vulnerabilities and exploit chains for Canon and Lexmark models. Learn about firmware analysis, debugging closed systems, and network security implications of office printers.
Malware Hunting in Cloud Environments - Effects and Techniques
Explore malware risks in cloud environments, focusing on PDF exploits, binary sessions, and attacker techniques. Learn to identify and mitigate threats for improved cloud security.
Run Next.js Without Vercel - Supporting Complex Features on Other Platforms
Discover how to deploy Next.js on platforms beyond Vercel, as Rob Stanford shares insights on reverse engineering and implementing complex features for Netlify support.

Breaking "DRM" in Polish Trains - Reverse Engineering Train Control Systems
Odkrywanie tajemnic systemu zabezpieczeń w polskich pociągach poprzez inżynierię wsteczną. Analiza podejrzanej usterki i demistyfikacja rzekomego "DRM" w nowoczesnych zespołach trakcyjnych.
Exposing and Exploiting AACSv2 UHD DRM - Full AACSess
Exposing vulnerabilities in AACSv2 DRM for UHD Blu-ray, including side-channel attacks on Intel SGX, leading to the first full compromise and unofficial playback of UHD-BD discs.
Hi-Intensity Deconstruction: Chronicles of a Cryptographic Heist
Delve into groundbreaking research revealing security vulnerabilities in HID's iCLASS SE platform, exploring reverse engineering techniques and critical mitigation strategies for electronic access control systems.
Unlocking Hardware Security - Red Team, Blue Team, and Trojan Tales
Explore hardware Trojan detection in ICs through a Red Team vs. Blue Team case study. Learn about imaging techniques, algorithm efficiency, and the impact of technology scaling on security.
Playing Video Games One Frame at a Time
Explore tool-assisted gaming techniques using C++, from supported mods to code injection, enhancing gameplay and overcoming challenges in video games as reaction times slow with age.
Jailbreaking TETRA Digital Radios and Base Stations - Security Analysis and Vulnerabilities
Dive into reverse engineering TETRA radio systems, uncovering cryptographic vulnerabilities, exploiting security flaws, and gaining control of Motorola MTM5x00 radios and base stations through practical demonstrations.