Building a Private Game Server by Reverse Engineering - DefCamp 2023
Explore reverse engineering techniques to build private game servers, enhancing cybersecurity skills and understanding network protocols in online gaming environments.
Custom Processing Unit - Tracing and Patching Intel Atom Microcode
Unveils groundbreaking framework for observing, tracing, and patching Intel Atom microcode execution, offering unprecedented insights into CPU internals and microcode update processes.
Déjà Vu - Uncovering Stolen Algorithms in Commercial Products
Techniques for detecting unauthorized use of algorithms in commercial products, including search methods, reverse-engineering, and a real-world case study. Provides strategies for addressing IP theft and prevention.
Ghost in the Wireless - iwlwifi Edition
Explore Intel Wi-Fi chip vulnerabilities through reverse-engineering, uncovering firmware exploits and code execution risks in complex features like Wake-on-WLAN and TDLS.

The 1s and 0s Behind Cyber Warfare
Explore cybersecurity research through pattern recognition and reverse engineering. Gain insights into decoding binary code and understanding the intricacies of cyber warfare in this engaging talk.
Better Bug Bounty Hunting, CTFs and Reverse Engineering - Cybertalk Episode 8
Insights on improving bug bounty skills, starting in pentesting, choosing laptops for security work, and comparing Android vs Windows reverse engineering techniques.
Programming a CTS-V Gauge Cluster into an ATS-V - A DIY Guide
Dive into the reverse engineering journey of programming a Cadillac CTS-V digital gauge cluster into an ATS-V, exploring GM electronics and sharing open-source solutions for automotive modifications.
QEMU-Native Hooking Bridge for Binary Fuzzing
Explore advanced binary fuzzing techniques through QEMU-Native Hooking Bridge, offering improved instruction hooking and memory control for efficient vulnerability detection in compiled code without source access.
Exploring Security Vulnerabilities in Flutter Mobile Applications
Discover critical security vulnerabilities in Flutter apps through reverse engineering techniques, focusing on hardcoded credentials and using tools like B(l)utter to analyze and protect mobile applications.
Reverse Engineering Android Apps With ACVTool
Discover how to effectively reverse engineer Android applications using ACVTool, exploring advanced techniques for app analysis and security assessment.
Indirect Syscalls: A Journey From High to Low
Dive into the mechanics of system calls, exploring both direct and indirect implementations while understanding their journey from high-level to low-level programming concepts and security implications.
Breaking the Ransomware Tool Set - When an OPSEC Failure Became an Intel Goldmine
Dive into a revealing analysis of ransomware operations through a critical OPSEC failure, uncovering valuable intelligence insights and defensive strategies against cybercrime toolsets.
Cracking The Chaos Ransomware Family
Dive into the technical analysis and decryption methods of the Chaos ransomware family, exploring its characteristics, vulnerabilities, and countermeasures.
Inside Dash Cam Custom Protocols and Security Vulnerabilities
Delve into comprehensive security analysis of network-connected dash cams, exploring vulnerabilities in boot processes, custom protocols, and configuration systems across multiple international manufacturers.
Unlocking the Gates: Hacking Industrial Remote Access Solutions
Dive into the vulnerabilities of industrial VPN gateways, exploring security flaws in remote access solutions and learning techniques to identify and understand potential system compromises.
Compromising Electronic Loggers and Creating Truck-to-Truck Worm - Security Vulnerabilities in ELD Systems
Discover critical security vulnerabilities in Electronic Logging Devices (ELDs) and their implications for truck network security, from reverse engineering to proof-of-concept attacks and industry-wide security reforms.
VDA Shenanigans: Attacking and Defending Vehicle Diagnostics Adapters
Dive into vehicle diagnostics adapter security through hardware reverse engineering, firmware analysis, and defensive strategies for automotive systems protection.
No Symbols When Reversing? No Problem - Bring Your Own Symbols for Binary Analysis
Discover efficient techniques for analyzing unknown functions in binaries, focusing on portable symbol creation and management using Ghidra, with practical examples from Golang-based malware analysis.
Generating Software Bill of Materials Through Hardware Hacking - A Case Study of Bob the Minion Router
Dive into hardware hacking techniques for extracting firmware and generating Software Bill of Materials (SBOM) from a WiFi router, exploring vulnerability discovery through practical disassembly methods.
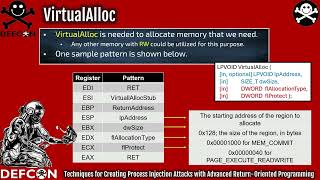
Process Injection Attacks with Return-Oriented Programming - Advanced Techniques and Methodologies
Discover advanced process injection techniques using return-oriented programming (ROP), including unique string comparison solutions, multiple WinAPI patterns, and practical methodologies for reliable implementation.
Sudos and Sudon'ts - Peering Inside Sudo for Windows
Delve into Windows security mechanisms through an analysis of Sudo for Windows, exploring process elevation, ALPC services, and Rust-Windows API interactions while uncovering potential security vulnerabilities.