AVR- Architecture, Assembly & Reverse Engineering
Explore AVR architecture, assembly language, and reverse engineering. Learn about timers, cycles, registers, and key instructions for efficient microcontroller programming and optimization.
Asm2Vec - Boosting Static Representation Robustness for Binary Clone Search
Innovative assembly code representation learning model for robust binary clone search, addressing challenges in reverse engineering against code obfuscation and compiler optimization.
The FaaS and the Curious - Exploring AWS Lambda Security in 2018
Explore AWS Lambda's attack surface, including function hijacking, cloud environment access, and runtime reverse engineering. Learn about FaaS security risks and potential exploits.
Advanced Android Studio Hacking - Part 2
Explore Android device hacking using Android Studio. Learn emulation, user agent tracking, reverse engineering, API tokens, decompilation, and SQL injection techniques.
Mach-O and the App Store - Understanding iOS Binary Format and Submission Process
Explore iOS app execution, Mach-O binary format, and App Store submission process. Gain insights into code storage, execution, and DRM implementation for iOS applications.
iOS Hacking - Inter-App Communication Vulnerabilities
Explore iOS inter-app communication vulnerabilities, focusing on pasteboard sharing, URL schemes, and universal links. Learn to use Frida for tracing and testing these mechanisms.
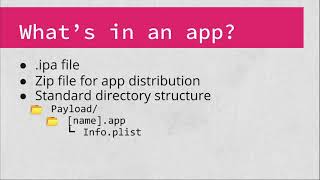
iOS Application Hacking - Understanding IPA Structure and Mach-O Binaries
Explore iOS app structure, IPA files, Mach-O binaries, and techniques to uncover hidden interfaces, API keys, and sensitive data. Learn to analyze and reconstruct app functionality.
Web Application Security - OWASP AppSecUSA 2014 Defenders Track
Explore cutting-edge web security topics including cloud security, malware analysis, and reverse engineering in this comprehensive conference track from OWASP AppSecUSA 2014.
.NET Reversing and Exploitation for Cool Kids
Explore .NET reverse engineering and exploitation techniques, including bypassing security features and modifying framework behavior through practical examples and demonstrations.
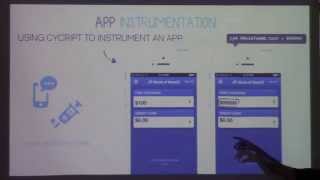
Uncovering OWASP's Mobile Risks in iOS Apps - AppSec California 2015
Explore iOS app vulnerabilities through reverse engineering techniques. Learn to extract, analyze, and identify common security risks in mobile applications using real-world examples.
Reversing Engineering Web Applications for Security - Behavior Analysis and WAF Detection
Explore web application reverse engineering, behavior analysis, and WAF detection techniques. Learn to create effective countermeasures against complex attacks using whitelist protection and traffic analysis.
Runtime Manipulation of Android and iOS Applications - Mobile Security Testing
Hands-on exploration of runtime manipulation and memory analysis techniques for Android and iOS apps, enhancing mobile security testing skills using tools like cycript and snoop-it.
Hacking the Oracle Application Framework - Deep-Dive Penetration Testing Techniques
Explore deep-dive penetration testing techniques for complex enterprise applications, using Oracle Application Framework as a case study. Learn about static reverse engineering, mock environments, and dynamic monitoring.
Android App Protection Techniques: Obfuscation, Packing, and Protection - APPSEC Cali 2018
Explore Android app protection techniques, including obfuscation, packing, and protection. Learn to analyze and counter these methods to identify potential malware and enhance app security.
BASHing iOS Applications - Command Line Tools for Mobile Auditors
Explore iOS application assessment using command-line tools. Learn mobile security fundamentals, binary analysis, data storage, and endpoint parsing while addressing OWASP Mobile Top 10 vulnerabilities.
Scripting Android Applications for Social Botnet Creation - Network Exploitation Techniques
Explore techniques for scripting Android applications, including APK manipulation, API exploitation, and creating realistic social botnets using JRuby sessions and network data.
Linux USB HID Interfacing in Userspace with Rust - Writing Drivers and Reverse Engineering
Explore userspace USB HID driver development in Rust, covering reverse engineering, protocol analysis, and MIDI device integration using mio for efficient I/O operations.
Insiders Guide to Mobile AppSec with Latest OWASP MASVS
Explore mobile app security with OWASP MASVS, covering data storage, network calls, authentication, coding, and reverse engineering. Gain insights from real-world experience and latest tools for effective mobile pentesting.
Panopticon: A Libre Cross-Platform Disassembler in Rust
Explore Panopticon: a libre cross-platform disassembler in Rust. Learn its architecture, features, and how Rust enhances development for reverse engineering and vulnerability discovery.
Why Port 10,000 Lines of Code to Rust - Lessons Learned
Explore the challenges and benefits of porting 10,000 lines of code to Rust, as discussed in this Rust Cologne meetup talk by Kai Michaelis.
First Steps in Analyzing Smali Code for Android Apps - Mobile Hacking
Explore Smali code analysis for Android apps, gaining essential techniques and tools. Learn to dissect and understand app internals, enhancing your mobile security and development expertise.