
Find All the Badness, Collect All the Things
Explore GRR, an open-source remote live-forensics system for rapid incident response and large-scale threat hunting. Learn about artifact collection, fleet-wide analysis, and future developments in digital forensics.
Dynamic Flash Instrumentation for Fun and Profit
Explore dynamic analysis of malicious Flash files using binary instrumentation, enabling faster and more detailed automatic analysis without decompilation.
File Disinfection Framework - Striking Back at Polymorphic Viruses
Explore an open-source framework for combating polymorphic viruses through advanced static analysis and emulation. Learn innovative techniques for file disinfection, malware analysis, and incident response.
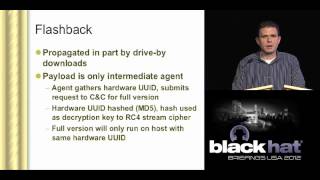
Flowers for Automated Malware Analysis
Explore advanced malware obfuscation techniques that bind execution to specific host environments, making automated analysis ineffective. Learn about the arms race between malware authors and security practitioners.
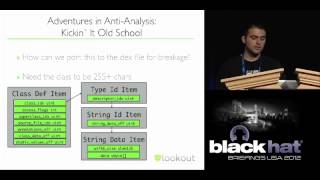
Dex Education - Practicing Safe Dex
Explore Android's dex file format, analyze vulnerabilities in dex analysis tools, and learn techniques to detect post-compilation modifications and protect against potential exploits.
The Sandbox Roulette - Are You Ready For The Gamble?
Explore application sandbox vulnerabilities and evasion techniques through a "Sandbox Roulette" demonstration, comparing various commercial solutions and their effectiveness against different exploit vectors.
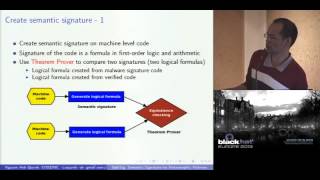
OptiSig - Semantic Signature for Metamorphic Malware
Explore semantic signatures for detecting metamorphic malware, overcoming limitations of traditional pattern matching. Learn about OptiSig toolset for generating and evaluating signatures on Intel platforms.
Hot Knives Through Butter - Bypassing Automated Analysis Systems
Explores advanced techniques used by malware to evade automated analysis systems, including extended sleep calls, mouse click triggers, and timed activation. Provides insights for security professionals on evolving threats.
End-to-End Analysis of a Domain Generating Algorithm Malware Family
Comprehensive analysis of a Domain Generating Algorithm malware family, covering deobfuscation, DGA analysis, sinkholing, and attribution of the malware's author and accomplices.
CuteCats.exe and the Arab Spring
Analysis of malware targeting activists during Middle Eastern uprisings, exploring distribution methods and impact on digital dissent and online communities.
I Know You Want Me - Unplugging PlugX
Comprehensive analysis of PlugX malware, exploring its evolution, detection techniques, and countermeasures. Gain insights into advanced threat intelligence and cybersecurity strategies.
Z - MAKE TROY NOT WAR - Case Study of the Wiper APT in Korea, and Beyond
Análisis detallado del ataque "Wiper" en Corea del Sur en 2013, explorando el vector de infección inicial, examinando muestras de malware y estableciendo conexiones con otros casos de APT desde 2009.
TOR - All the Things
Explore Tortilla, a new tool for securely routing all TCP/IP and DNS traffic through Tor on Windows, enabling anonymous use of any program without additional hardware or VPNs.
CrowdSource - Crowd Trained Machine Learning Model for Malware Capability Detection
Innovative machine learning tool for automated malware capability detection, trained on web technical documents. Provides probabilistic and traceable output for rapid reverse engineering of active malware variants.
New Trends in FastFlux Networks
Explores new trends in fast-flux networks, including slower change rates, shared resources, multi-level structures, and similarities with benign applications. Proposes novel detection approaches based on these findings.
Adventures in Bouncer Land
Explore techniques for bypassing Google Play's security measures, including strategies for evading detection and transforming benign apps into malicious ones.
Press ROOT to Continue - Detecting OSX and Windows Bootkits with RDFU
Explore UEFI rootkit detection with RDFU framework. Learn about OSX bootkit functionality, including password sniffing and privilege escalation. Discover tools to combat emerging UEFI-based threats.
All You Always Wanted to Know About Antiviruses
Demystifying antivirus software: internals, detection methods, and trade-offs. Explores AV engines, whitelists, signatures, real-time monitoring, and network inspection across Windows, Linux, and Android platforms.
Hello 1994
Découvrez les nouvelles techniques de dissimulation du malware PlugX utilisant les API Windows via COM, son exploitation de Windows Explorer et sa capacité de propagation par clé USB.
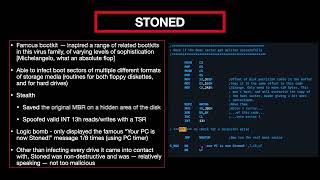
Portrait of the Artist as a Young VX-er - This Painting Is an MBR Bootkit
Exploring MS-DOS malware techniques to create art, blending assembly programming with vintage bootkit analysis. Insights on legacy vulnerabilities and modern applications in firmware and IoT security.
Mac-ing Sense of the 3CX Supply Chain Attack - Analysis of the macOS Payloads
Detailed analysis of the 3CX supply chain attack's macOS payloads, exploring the first "chained" supply chain attack and its impact on macOS systems. Insights into advanced cybersecurity threats and defenses.