Malware Analysis - Spring 2017
Comprehensive malware analysis course covering static and dynamic techniques, assembly language, file formats, and practical debugging using various tools and real-world examples.

Miscellaneous Malware Analysis
Explore diverse malware analysis techniques, from deobfuscation and reverse engineering to hunting and classification. Gain practical skills in handling various malware types and writing analysis reports.
Classifying Malware with YARA
Learn to classify malware using YARA rules, from setup to integration. Explore writing techniques, resources, and practical applications for effective malware analysis and detection.
Let Me YARA That For You
Explore advanced YARA rule creation techniques for malware detection and analysis, enhancing your cybersecurity skills and threat hunting capabilities.
TLS Callbacks in PE Files - Detection and Analysis
Explore TLS callbacks in PE files, their use in malware, and detection methods. Learn to identify and analyze these anti-debugging techniques using various tools and Yara rules.
Open-source Projects in Cyber Security
Explore open-source cybersecurity projects, including YARA-related tools like GenRex, YARI, and YLS. Gain insights into innovative developments enhancing malware analysis and industry protection.
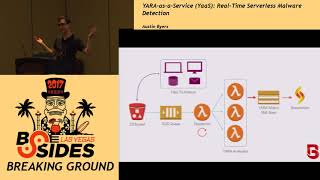
YARA-as-a-Service - Real-Time Serverless Malware Detection
Explore real-time serverless malware detection using YARA and Binary Alert. Learn about scalable security tools, features, and implementation for enhanced threat protection.
KLara - Your New Friend
Cloud-based Yara scanner for efficient malware detection. Scans large malware libraries at high speeds, enhancing threat intelligence and APT hunting capabilities. Open-source project with live demo.
Operationalizing Yara
Learn to effectively implement and utilize Yara rules for enhanced threat detection and malware analysis in operational environments.
Malware Armor
Explore malware analysis techniques, including dynamic and static analysis, anti-virtualization detection, anti-debugging, and obfuscation methods. Learn to use various tools for effective malware armor analysis.
Detection of Malicious Capabilities Using YARA
Explore YARA for malware detection, covering heuristics, memory analysis, and comparison with other frameworks. Learn to create effective rules for identifying malicious capabilities.
Autopsy Update
Comprehensive update on Autopsy digital forensics tool, covering new features like Web Domain interfaces, scoring, and Solr 8 upgrade. Explores improvements in UI, artifact pipelines, and integration with other forensic tools.

Black Hat USA 2025
Black Hat USA 2025