Reverse Engineering Windows Malware 101 Workshop
Hands-on workshop introducing reverse engineering fundamentals for Windows malware analysis. Learn to set analysis goals, use tools, and apply computer science concepts through practical exercises.
Lessons Learned Hunting IoT Malware
Explore IoT malware hunting techniques, honeypot designs, and real-world case studies. Learn reverse-engineering strategies for embedded systems and gain insights into next-generation threat detection.
Burning Down the Haystack to Find the Needle
Explore network flow pattern analysis to detect and prevent contemporary threats, and learn how to build a security analytics program for enhanced threat visibility and response.
When Documents Bite
Explore malicious document attacks, their evolution, and impact on cybersecurity. Learn about real-world techniques and strategies for defending against targeted attacks in enterprise networks.
Offensive Pcap
Explore libpcap for offensive security: bypass firewalls, intercept traffic, manipulate network connections, and evade detection. Hands-on techniques with source code provided.
You Don't See Me - Abusing Whitelists to Hide and Run Malware
Explore techniques for exploiting whitelists to conceal and execute malware, enhancing your understanding of cybersecurity vulnerabilities and defense strategies.
Helping Johnny to Analyze Malware - A Usability-Optimized Decompiler and Malware Analysis User Study
Explore a usability-optimized decompiler for malware analysis, featuring readability improvements that significantly enhance analysts' ability to understand and combat complex malicious software.
Following Devil's Footprints - Cross-Platform Analysis of Potentially Harmful Libraries on Android and iOS
Cross-platform analysis of potentially harmful libraries in Android and iOS apps, revealing widespread infection and risky behaviors like unauthorized data access and audio/video recording.
SoK - Deep Packer Inspection - A Longitudinal Study of the Complexity of Run-Time Packers
Longitudinal study analyzing run-time packers' complexity and evolution, proposing a taxonomy for measurement and presenting statistics on packer structures used in malware obfuscation.
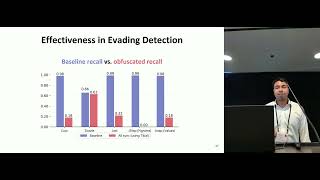
Wobfuscator - Obfuscating JavaScript Malware via Opportunistic Translation to WebAssembly
Explore innovative techniques for obfuscating JavaScript malware through WebAssembly translation, enhancing code protection and evading detection mechanisms.
SYMBEXCEL - Automated Analysis and Understanding of Malicious Excel 4.0 Macros
Explore automated techniques for analyzing and understanding malicious Excel 4.0 macros, enhancing cybersecurity defenses against sophisticated threats in spreadsheet files.
Vulnerabilities in Application Whitelisting - Malware Case Studies
Explore vulnerabilities in application whitelisting through real-world malware case studies. Learn detection techniques and gain insights into bypassing security measures.
Technical A02 - The Current State of Memory Forensics
Explore memory forensics techniques, acquisition methods, and analysis goals. Learn about Windows 10 memory compression and Virtual Secure Mode impacts on forensic investigations.
Cybersecurity Zero to Hero with CyberChef
Learn to perform complex cybersecurity tasks using CyberChef, a user-friendly web app that simplifies malware analysis and streamlines workflows for both beginners and experienced analysts.
Binee - Complete Emulation of Advanced Malware
Explore advanced malware emulation with Binee, a Windows Process emulator. Learn to create detailed memory models, mimic OS kernels, and gather dynamic analysis data for reverse engineering and vulnerability research.
Automating Bulk Intelligence Collection
Explore techniques for automating bulk intelligence collection in cybersecurity, including data mining, malware analysis, and email campaign investigation. Learn about the Yalda framework for efficient threat intelligence gathering.
Your Mac Defenestrated Post OSXploitation Elevated - FuzzyNop Noncetonic
Explore advanced Mac post-exploitation techniques, including persistence methods, keychain access, and system event manipulation for enhanced security understanding.
REDIScovering HeadCrab - A Technical Analysis of a Novel Malware and the Mind Behind It
Uncover the secrets of HeadCrab, an advanced malware utilizing Redis Modules. Explore its sophisticated techniques, worldwide infiltration, and the mind of its creator in this technical analysis.
Defeating the Transparency Feature of DBI
Techniques to break transparency in dynamic binary instrumentation tools, exposing limitations and enabling detection of analysis environments for malware and binary applications.
Prevalent Characteristics in Modern Malware
Explore prevalent characteristics in modern malware, including evasion techniques, anti-analysis methods, and defensive capabilities. Learn to improve malware prevention and analysis strategies.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.